Stay ahead of what’s next in Agentic AppSec.
Explore research, guides, webinars, analyst insights, and technical resources on securing AI-generated code and modern, AI-first software development.
Best Practices
Meet Legit MCP: AI-Powered Security That Works Where Your Team Works
Get details on the newly released Legit MCP Server.

Announcing New Legit ASPM AI Capabilities
Get details on Legit's new AI capabilities.
Strengthening Software Security Under the EU Cyber Resilience Act: A High-Level Guide for Security Leaders and CISOs
Get guidance on key tenets of the EU CRA and how Legit can help address them.
What to Look for in Application Security Posture Management (ASPM)
Get details on the key capabilities for an ASPM platform.
How Legit Is Using Classic Economic Tools to Prevent Application Vulnerabilities
Prevent vulnerabilities and learn how Legit uses data-driven methods like the Lorenz Curve and the Gini Index to…
Legit Scans for Secrets in SharePoint
Get details on Legit's new ability to scan for secrets in SharePoint.
The Power of Identifying Continuously Vulnerable Repositories (CVRs)
Legit Security is redefining application security by analyzing CVRs, helping enterprises prevent vulnerabilities from…
Legit and Traceable: Better Together
Get details on Legit's new partnership with Traceable.
Legit Announces New Vulnerability Prevention Capabilities
Get details on Legit's new capabilities that allow AppSec teams to prevent introducing vulnerabilities.
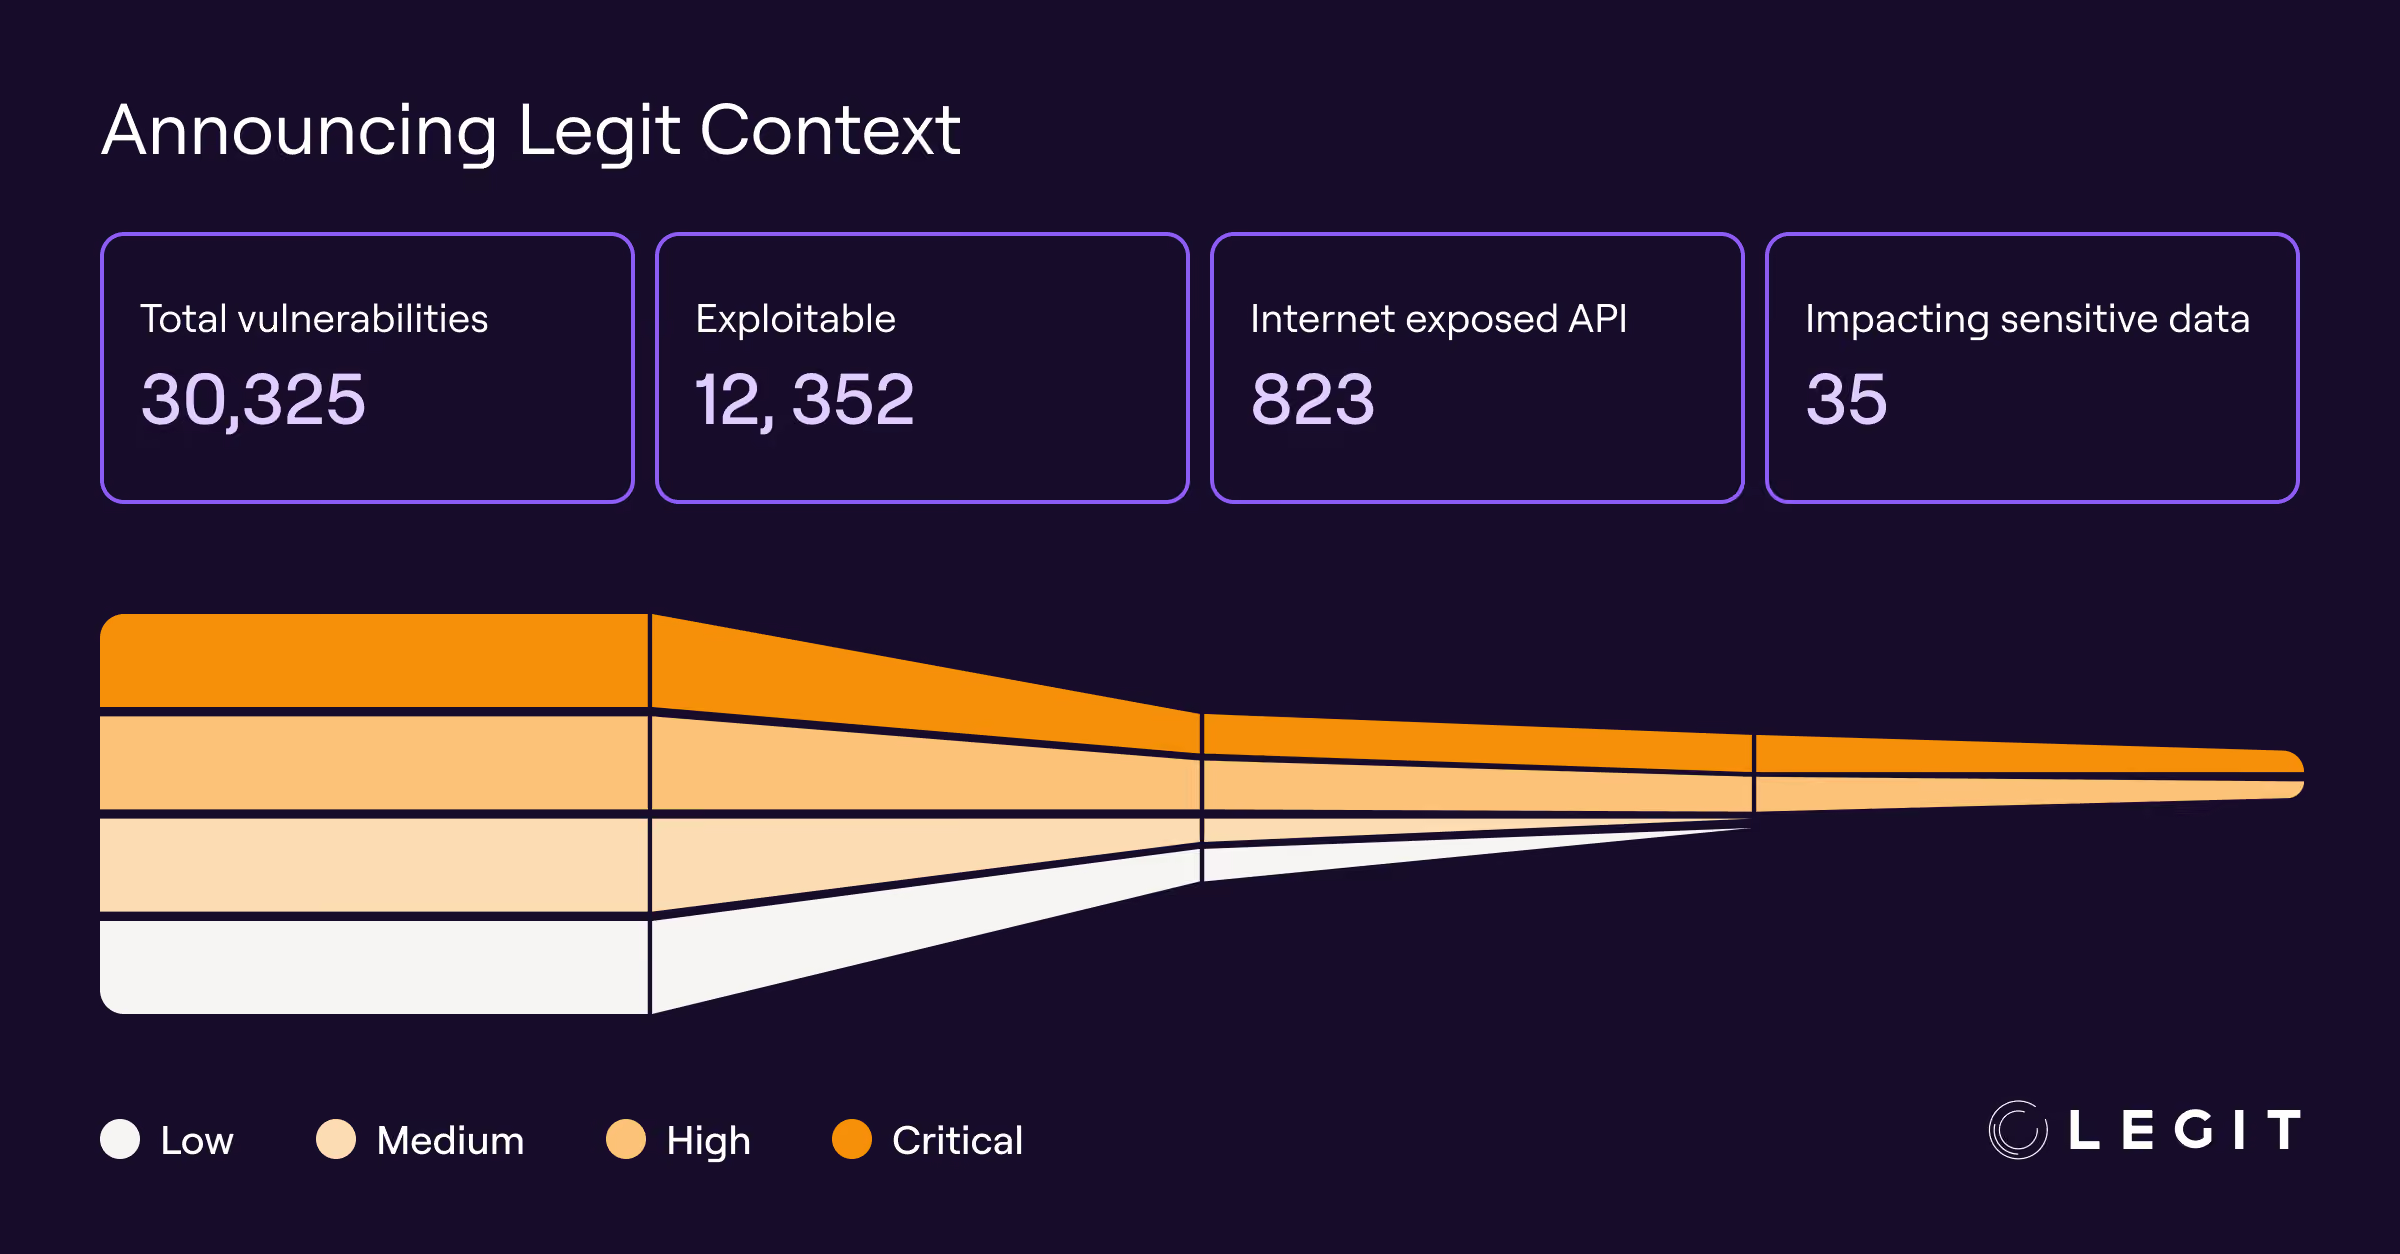
Announcing Legit Context: The Missing Link to True Business-Driven ASPM
Get details on Legit's new capabilities that allow AppSec teams to focus on the issues posing real risk.
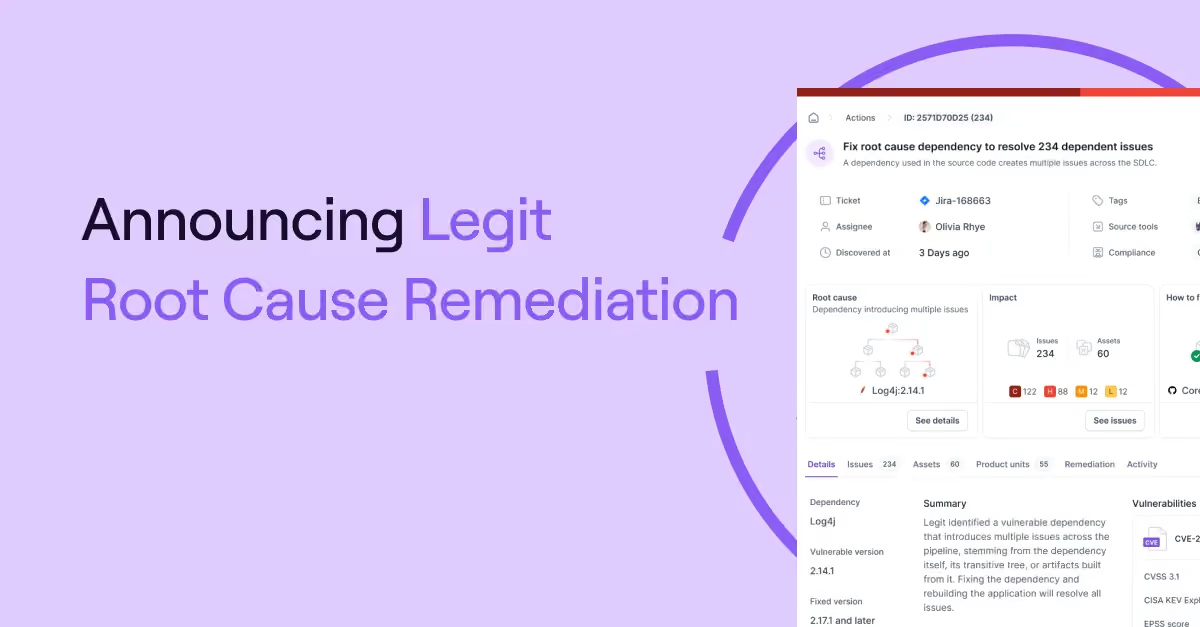
Announcing Legit Root Cause Remediation
Get details on Legit's new capabilities that allow teams to quickly fix what matters most.

Announcing the 2025 State of Application Risk Report
Use the data and analysis in this report to prioritize your 2025 AppSec efforts.
How to Reduce Risk From Exposed Secrets
Understand how secrets end up exposed, and how to prevent this risk.
Unlocking the Power and Potential of GenAI in Software Development
GenAI's rapid adoption brings with it significant challenges in security, governance, and visibility.
How to Reduce Risk From Developer Permissions Sprawl
How to Reduce Risk From Developer Permissions Sprawl. Get steps to prevent risky permissions sprawl in your SDLC.
How to Reduce Risk From Misconfigured Build Assets
How to Reduce Risk From Misconfigured Build Assets. Get steps to prevent risky misconfigurations in your SDLC.

Software Security Best Practices: Where to Focus First
Software Security Best Practices: Where to Focus First. Get our recommendations on where to focus your software…
How to Mitigate the Risk of GitHub Actions
How to Mitigate the Risk of GitHub Actions. Get highlights of our research into the security of GitHub Actions, and…

The Risks Lurking in Publicly Exposed GenAI Development Services
The Risks Lurking in Publicly Exposed GenAI Development Services. Get our research team's analysis of the security of…
ESG Survey Report Finds AI, Secrets, and Misconfigurations Plague AppSec Teams
ESG Survey Report Finds AI, Secrets, and Misconfigurations Plague AppSec Teams. Find out how your peers are managing…

Preview of State of GitHub Actions Security Report: Security of GH Workflows Building Blocks
Security of the Building Blocks of GitHub Actions Workflows. Understand the security status of GitHub Actions…
Why Legit Security Immediately Joined the New Coalition for Secure Artificial Intelligence (CoSAI)
Why Legit Security Immediately Joined Google’s New Coalition for Secure Artificial Intelligence (CoSAI). Get details…
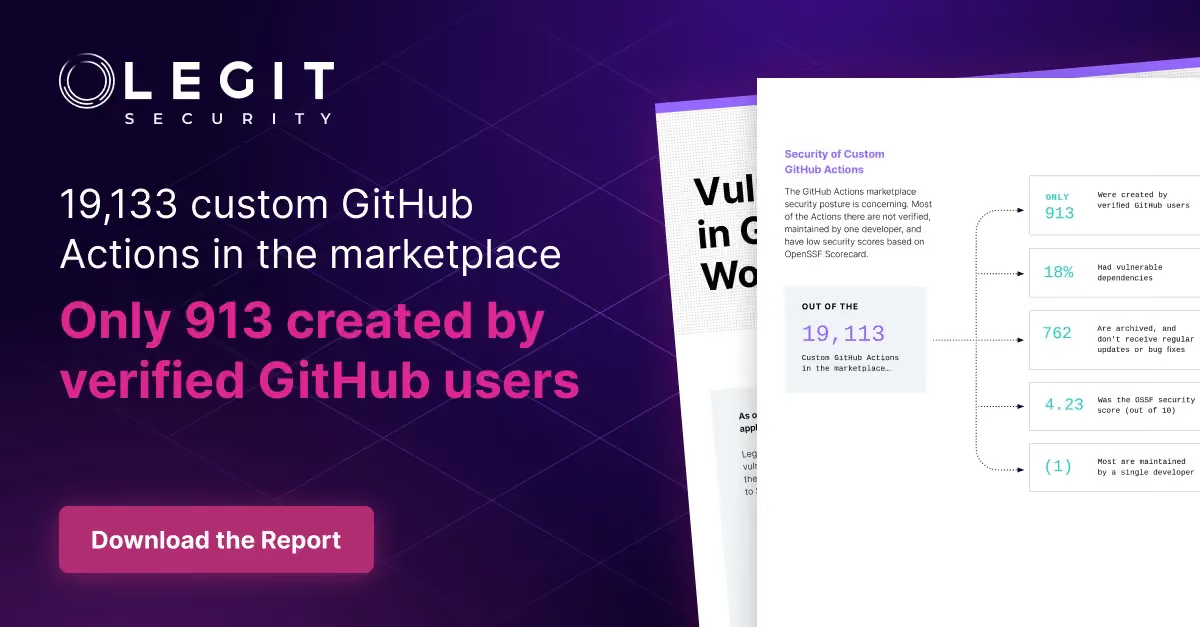
Security of Custom GitHub Actions
Security of Custom GitHub Actions. Get details on Legit's research on the security of custom GitHub Actions.
Announcing The State of GitHub Actions Security Report
Announcing the State of GitHub Actions Security Report. Get details on Legit's research on the security of GitHub…
EU Cyber Resilience Act: Updates and Important Requirements
Ensure compliance with the EU Cyber Resilience Act. Learn CRA essentials, how to secure digital products, and how…
What is ASPM? Application Security Posture Management 101
Learn how Legit Security enhances Application Security Posture Management (ASPM) by automating key processes to ensure…

Security Challenges Introduced by Modern Software Development
Security Challenges Introduced by Modern Software Development. Understand how modern software development is changing…
Don’t Protect Your Software Supply Chain, Defend the Entire Software Factory
Don't Protect Your Software Supply Chain, Defend the Entire Software Factory. Find out why a too-narrow definition of…
Securing the Gateway: Why Protecting Build Systems Is Crucial in Modern Software Development
Securing the Gateway: Why Protecting Build Systems Is Crucial in Modern Software Development. Understand why securing…

Verizon 2024 DBIR: Key Takeaways
Verizon 2024 DBIR Key Takeaways. Get key data points and takeaways from the 2024 Verizon Data Breach Investigations…

New Survey Finds a Paradox of Confidence in Software Supply Chain Security
New Survey Finds a Paradox of Confidence in Software Supply Chain Security. Get results of and analysis on ESG's new…

Dependency Confusion Vulnerability Found in an Archived Apache Project
Dependency Confusion Vulnerability Found in an Archived Apache Project. Get details on the Legit research team's…
How to Reduce the Risk of Using External AI Models in Your SDLC
How to Reduce the Risk of Using External AI Models in Your SDLC. Understand how AI models add risk and how to address…
Securing the Software Supply Chain: Risk Management Tips
Securing the Software Supply Chain: Risk Management Tips. Securing the software supply chain can seem daunting, but…

How to Get the Most From Your Secrets Scanning
How to Get the Most From Your Secrets Scanning. Secret scanning is essential for unlocking next-level software supply…
Microsoft Under Attack by Russian Cyberattackers
Microsoft Under Attack by Russian Cyberattackers. Understand how these attackers are operating and what their tactics…
Using AI to Reduce False Positives in Secrets Scanners
Using AI to Reduce False Positives in Secrets Scanners. Get an overview of how secrets scanners work, and how Legit is…
Understanding the White House Report on Secure and Measurable Software
Understanding the White House Report on Secure and Measurable Software. Get details on the report, how to address it…

Don't Miss These Emerging Trends in Cloud Application Security
Don't Miss These Emerging Trends in Cloud Application Security. Get details on trends and best practices in cloud…

How to Address CISA Attestation
How to Address CISA Attestation. Get details on the CISA Attestation, how to address it, and how Legit can help.

What to Look for in a Secrets Scanner
What to Look for in a Secrets Scanner. Find out the key capabilities of secrets scanners and what to consider when…

It's Time to Automate Your Security Testing w/ DevSecOps Tools
Your security is only as good as your team, so why leave it to chance? Learn how automated DevSecOps tools can…
Scaling Security in Cloud-Native Environments with CNAPP
How CNAPP works and why it's a critical component of an effective code to cloud application security strategy.
A Guide to Securing Secrets in CI/CD Pipelines
Dive into the world of software secrets, learn best practices for secure CI/CD, and safeguard sensitive data in this…

6 Cloud Application Security Best Practices You Can't Miss
Discover cloud application security best practices: risks, benefits, and strategies for a secure cloud environment.

Top Vulnerability Management Best Practices and Tips
Master vulnerability management best practices with our guide. Secure your organization using effective strategies and…
Emerging Risks with Embedded LLM in Applications
Learn how the use of Large Language Models (LLMs) like OpenAI's GPT and Google's Bard can create security risks in…

Application Security Testing: Types and Best Practices
Enhance your application security testing and identify vulnerabilities faster. Learn best practices and improve your…

How to Choose the Right Vulnerability Management Tools
Discover core functions, benefits, and tips for selecting the best vulnerability management solutions to boost your…

The Business Risks and Costs of Source Code Leaks and Prevention Tips
Protect your business from the serious consequences of code leaks by taking proactive measures to enhance your…
Modern AppSec Needs Code to Cloud Traceability
We talk about why you need code to cloud traceability to modernize your application security and secure your SDLC and…
Top 8 Cloud Application Security Challenges and Issues
Discover top cloud security threats and learn effective techniques to keep your cloud applications secure year-round.
Exposing Secrets Via SDLC Tools: The Artifactory Case
Our team investigated how sensitive information can get exposed via SDLC tools that may be used as part of your…

Top Open Source Supply Chain Security Risks & Tips to Prevent
Learn tips to strengthen software supply chain security and address open source software security risks and best…

What is Secure SDLC? Best Practices for Enhanced Security
Understand SDLC security with our breakdown of each Software Development Life Cycle stage for enhanced software…
GUAC Explained in 5 Minutes
We cover GUAC and its value for your team once GUAC reaches maturity and untangle the complexity of security and…
2023 Predictions for Modern Application Security
This blog analyzes trends in application security and predicts the future direction of enterprise application security…

What are the Five Elements of the NIST Cybersecurity Framework?
This blog details the five elements of the NIST cybersecurity framework and identifies the critical aspects of…
How to Continuously Detect Vulnerable Jenkins Plugins to Avoid a Software Supply Chain Attack
See how attackers used compromised Jenkins plugins to attack the software supply chain and how to continuously detect…
Modern AppSec Requires Extending Beyond SCA and SAST
Examining the evolution of application security and why securing the modern SDLC requires organizations to embrace new…
GitHub Codespaces Security Best Practices
GitHub configurations aren't secure out of the box. It's up to you to secure them. This blog discusses GitHub's new…
Integrating Security into DevOps: A Step-By-Step Guide
If you haven’t already been integrating security into DevOps, now’s the time. Learn about the benefits & use this…
Software Supply Chain Risks to Be Aware of
Discover four key supply chain risks every CISO must address as software technology evolves and security becomes…
Software Artifacts Best Practices to Prevent Getting Hacked
Malicious actors are poisoning your artifacts to compromise your software supply chain. Learn how to protect your…

8 Best Practices in Cyber Supply Chain Risk Management to Stay Safe
Discover the four types of threats to business software supply chains and the 8 best practices in risk management to…
How Was LastPass Compromised? Software Supply Chain Attack Tips
LastPass data breach: unauthorized access compromised developer accounts and proprietary source code. Learn about the…
10 Agile Software Development Security Concerns You Need to Know
Agile development methodology has become increasingly popular, but it doesn’t come without security concerns. Get to…
Secure Software Development Lifecycle (SDLC): Key Phases Guide
Explore how to seamlessly integrate security into SDLC phases, transforming your development process to achieve…
Data Security Best Practices to Code Securely and Protect Your Data
Boost your business with secure coding practices. Explore our list to improve data security practices and ensure…
A 10-Step Application Security Risk Assessment Checklist
An application risk assessment is an essential tool to help security and development teams spot hidden vulnerabilities…
Secure GitHub: How to Keep Your Code and Pipelines Safe from Hackers
Is GitHub safe? Discover how developers can avoid misconfigurations and vulnerabilities to ensure secure collaboration…
GitHub Security Best Practices Your Team Should Be Following
This article will explain why security and GitHub should go hand in hand and describes a few best practices we believe…

Forget about DevOps, It’s Time to Adopt the DevSecOps Mindset
Debunk common DevSecOps myths and discover why understanding the actual role of DevSecOps is essential for modern…
What Are Immutable Tags And Can They Protect You From Supply Chain Attacks?
Some tags cannot be trusted to reference the same object all the time, and can be changed without the users’…
Vulnerable GitHub Actions Workflows Part 2: Actions That Open the Door to CI/CD Pipeline Attacks
We examine a bug we’ve found in a popular third-party GitHub action and how it could lead to your SDLC pipeline being…