The board expects answers you don't have yet.
Risk you can't fully see
AI coding tools generate more code, dependencies, and infra changes than any team can manually review, leaving blind spots legacy tools were never built to catch.
A backlog that outpaces headcount
The find-it-fix-it model was built for a slower era. Findings pile up faster than a resource-constrained team can triage them, and the riskiest issues sit the longest.
Compliance exposure that
keeps growing
Every unaddressed vulnerability is a harder conversation with auditors and regulators, and the backlog makes that conversation worse every quarter.
Traditional AppSec vs. Agentic AppSec.
Traditional AppSec
Finds issues after they ship
Buries teams in false positives
Leaves fixes to manual triage
Backlogs grow faster than teams
Agentic

Stops issues before commit
Prioritizes by real business risk
Remediates autonomously
Gets smarter with every fix
How LegitWorks
Legit gives your program a continuous cycle: prevent what you can at generation, prioritize what's left by real business risk, and remediate autonomously, improving every cycle.
Fewer new vulnerabilities enter your codebase.
VibeGuard enforces policy at the moment AI generates code, so your team spends less time explaining why the backlog grew again this quarter.
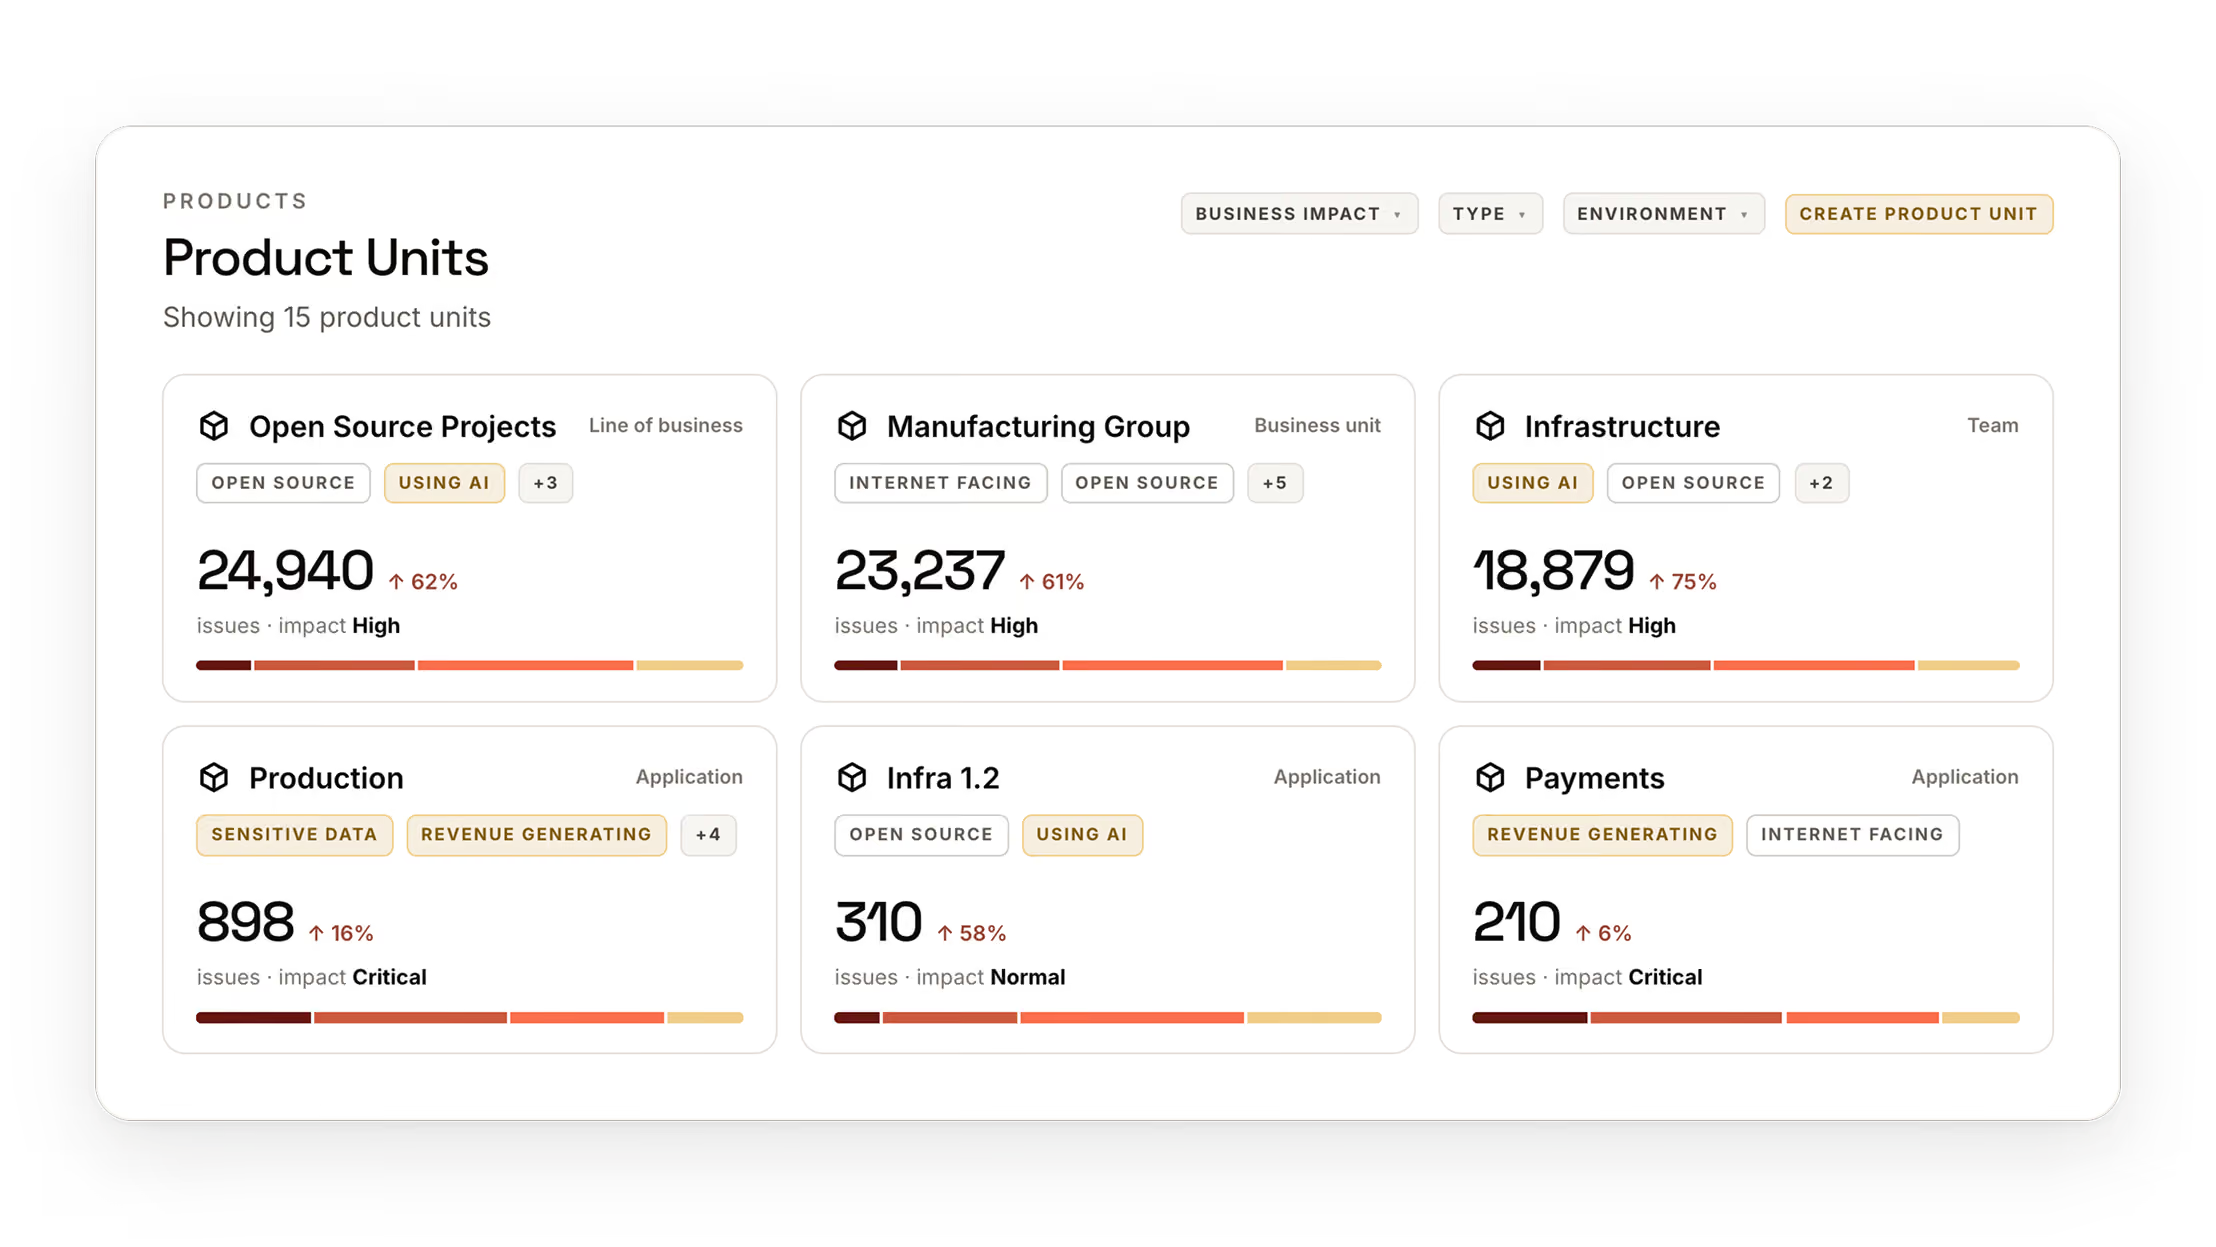
Only real risk reaches your team's queue.
Business criticality, exposure, and exploitability decide what's urgent, so your program reports on risk reduction, not raw finding counts.
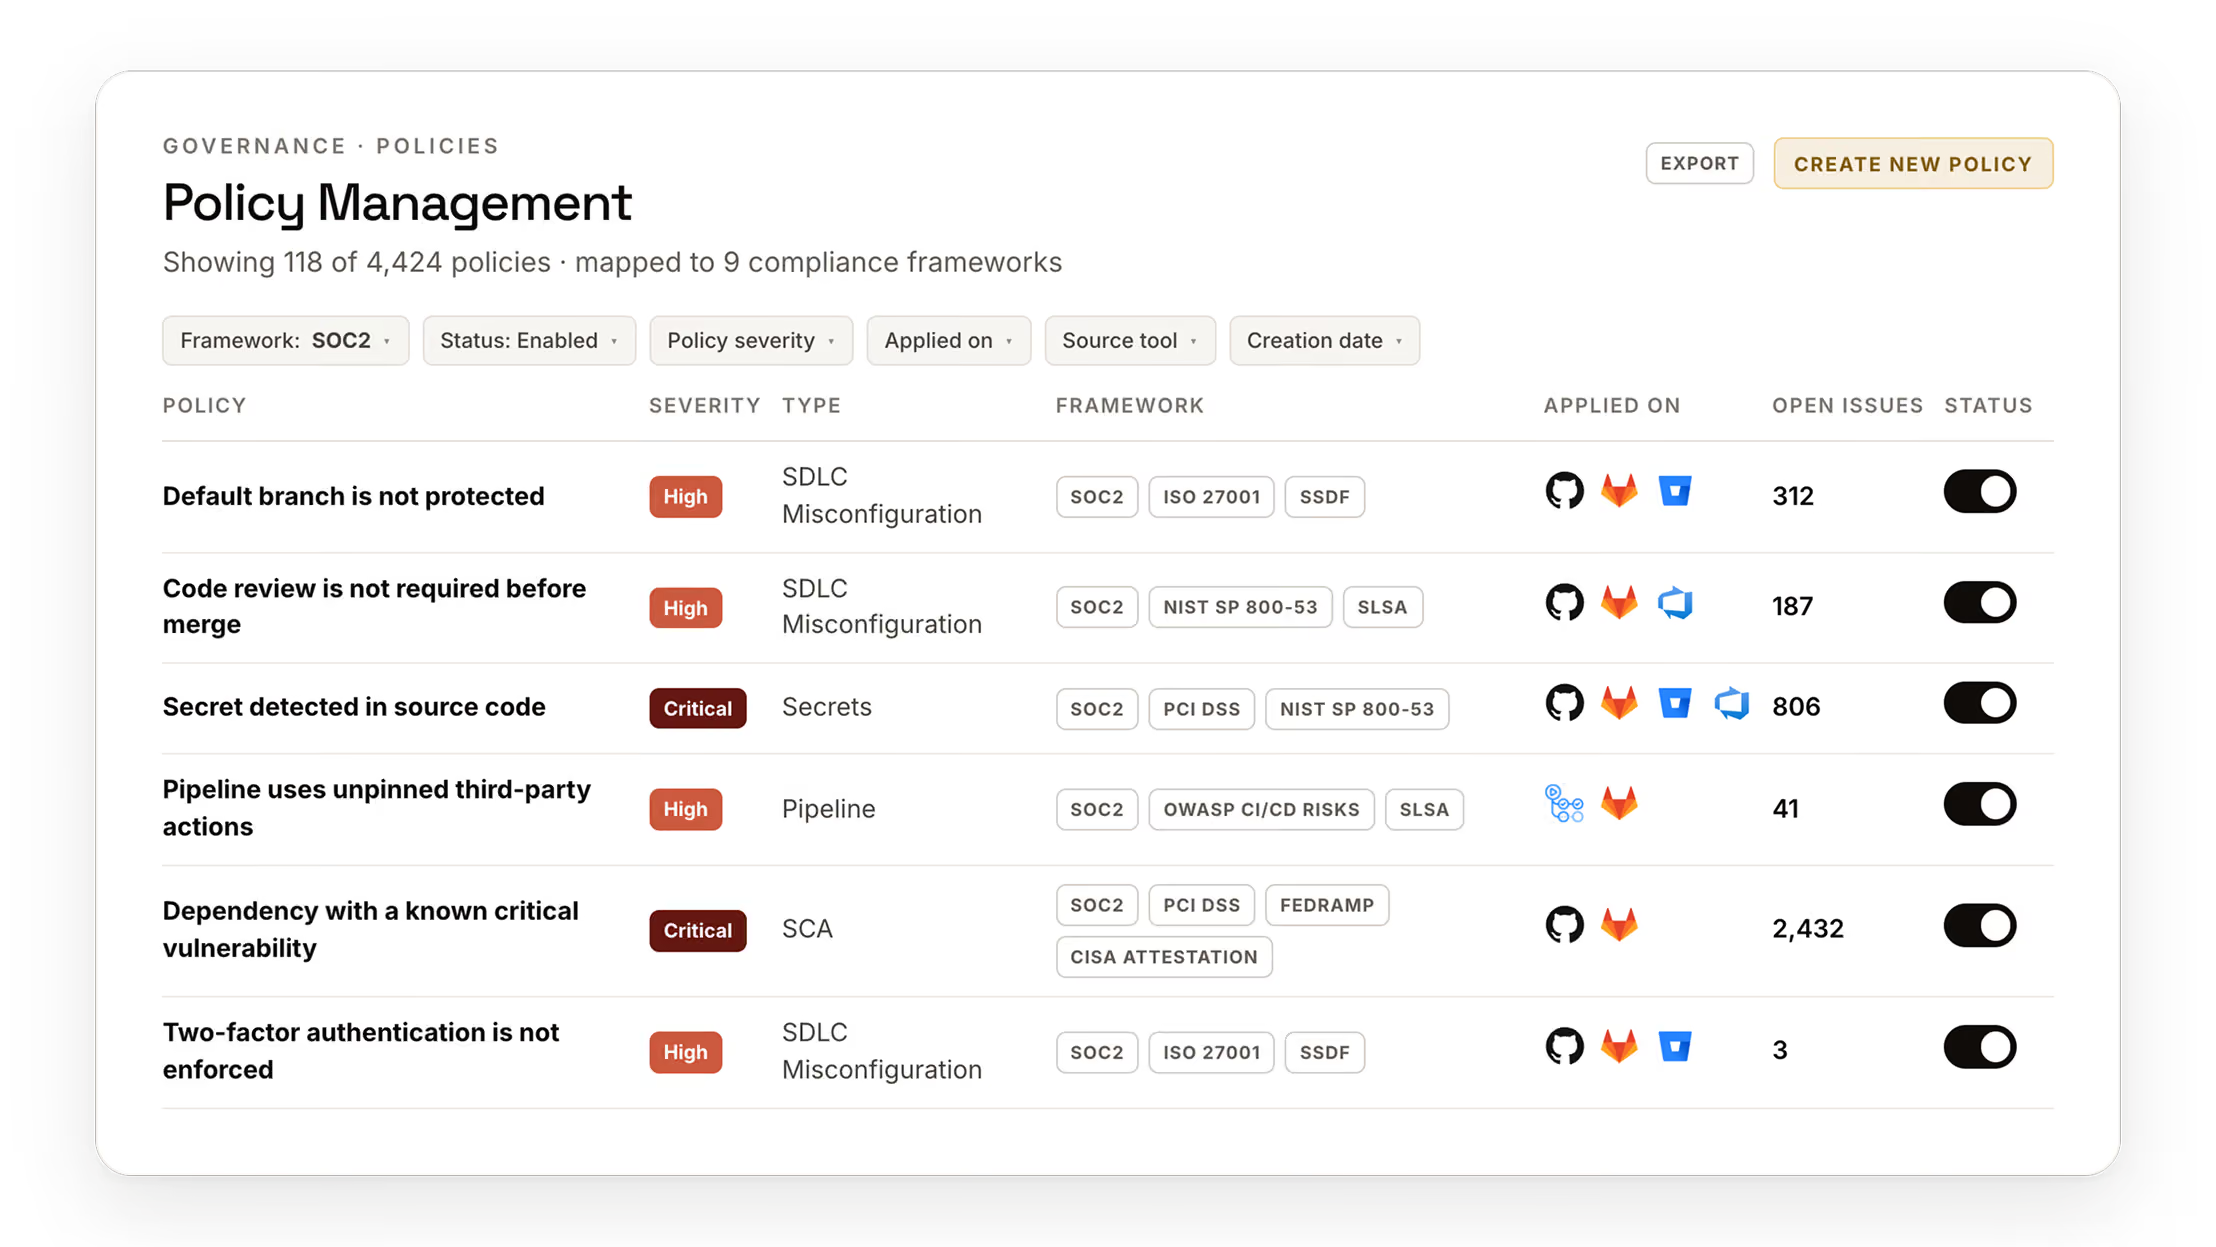
Fixes happen without waiting on headcount.
Autonomous agents remediate the highest-risk issues and validate the fix, so your program shows measurable progress between board meetings.
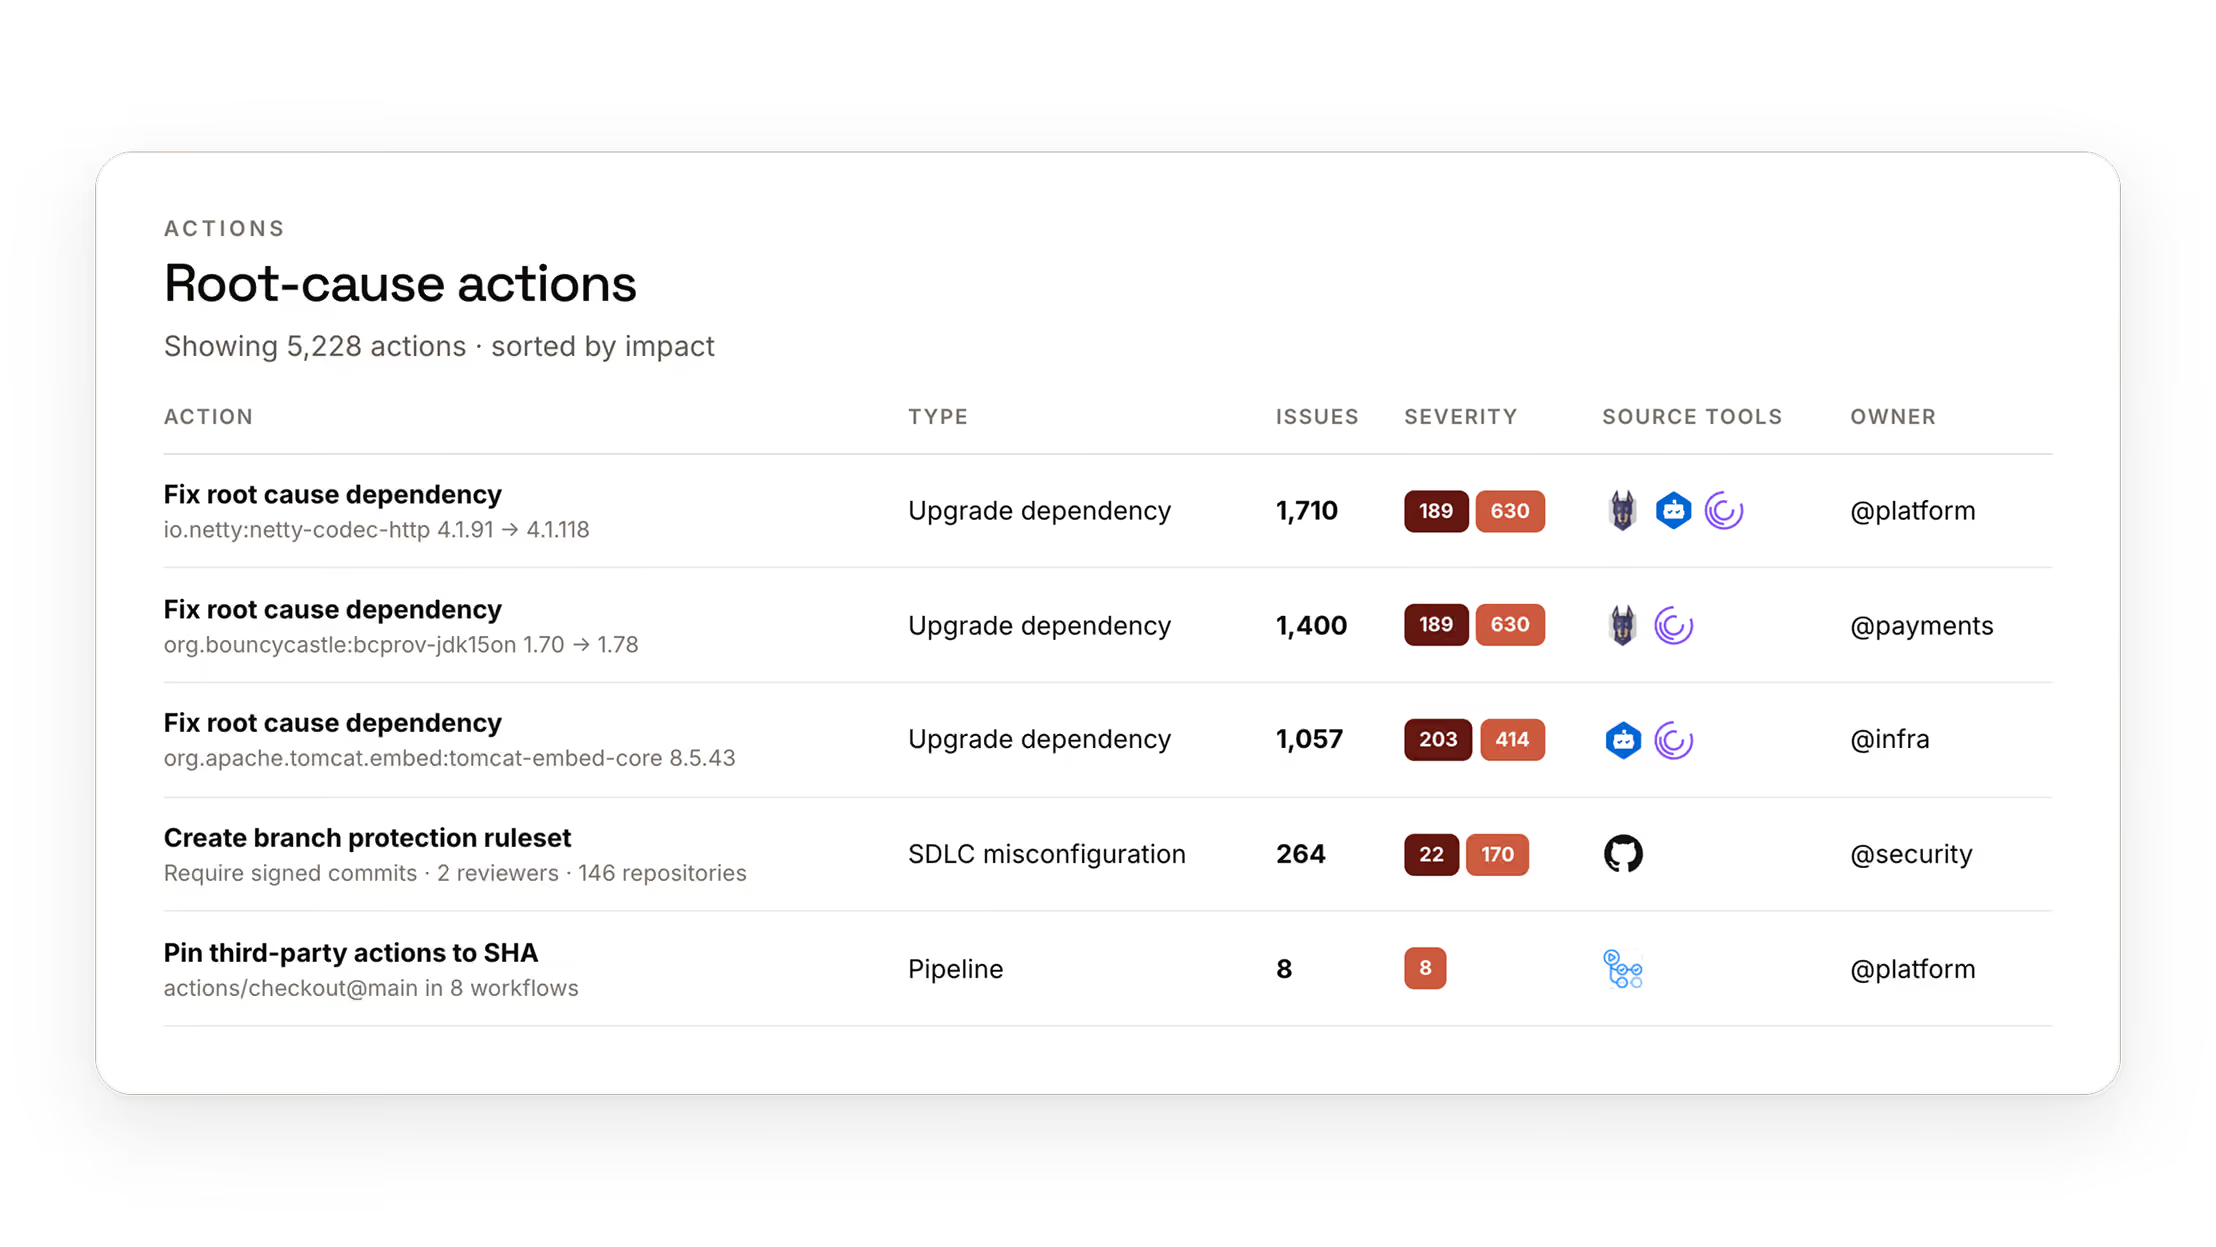
What changes with Legit
A program the board can actually track and trust quarter over quarter.

Context and reachability analysis reduce vulnerability noise by more than 90%, so your team reports on real risk, not raw finding counts.

AI-driven detection cuts false positives by over 95%, validated in secret scanning, so what reaches your board is worth acting on.

Legit is rated 4.8 on Gartner Peer Insights by the security teams running programs like yours.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."


More insights for modern AppSec teams

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
Agentic Remediation Just Got Bigger: Now Fixing Vulnerabilities in Your Dependencies, Not Just Your Code
Legit Security's Agentic Remediation now tackles vulnerabilities in dependencies, ensuring faster, verified fixes and enhancing AppSec in an AI-driven landscape.