Point tools were never meant to add up.
A fragmented security architecture
SAST, SCA, secrets, and IaC scanners each hold their own view of risk, so no single tool can tell you what's reachable, exploitable, or actually worth fixing first.
Integration overhead that never ends
Every new scanner means another connector to SCM, CI/CD, and ticketing, and another set of findings that don't share context with anything else in the stack.
No shared context across the toolchain
Without a common data layer, prioritization happens tool by tool, so the same vulnerability can look critical in one system and invisible in another.
Traditional AppSec vs. Agentic AppSec.
Traditional AppSec
Finds issues after they ship
Buries teams in false positives
Leaves fixes to manual triage
Backlogs grow faster than teams
Agentic

Stops issues before commit
Prioritizes by real business risk
Remediates autonomously
Gets smarter with every fix
How LegitWorks
Legit runs as one context layer across your stack: preventing issues at generation, prioritizing with a single risk model, and remediating through agents that plug into your existing tools.
Deploys on top of the tools you already run.
Legit connects to GitHub, GitLab, Wiz, and Jfrog, among others, as an Agentic AppSec layer, or natively replaces point tools where you're ready to consolidate.
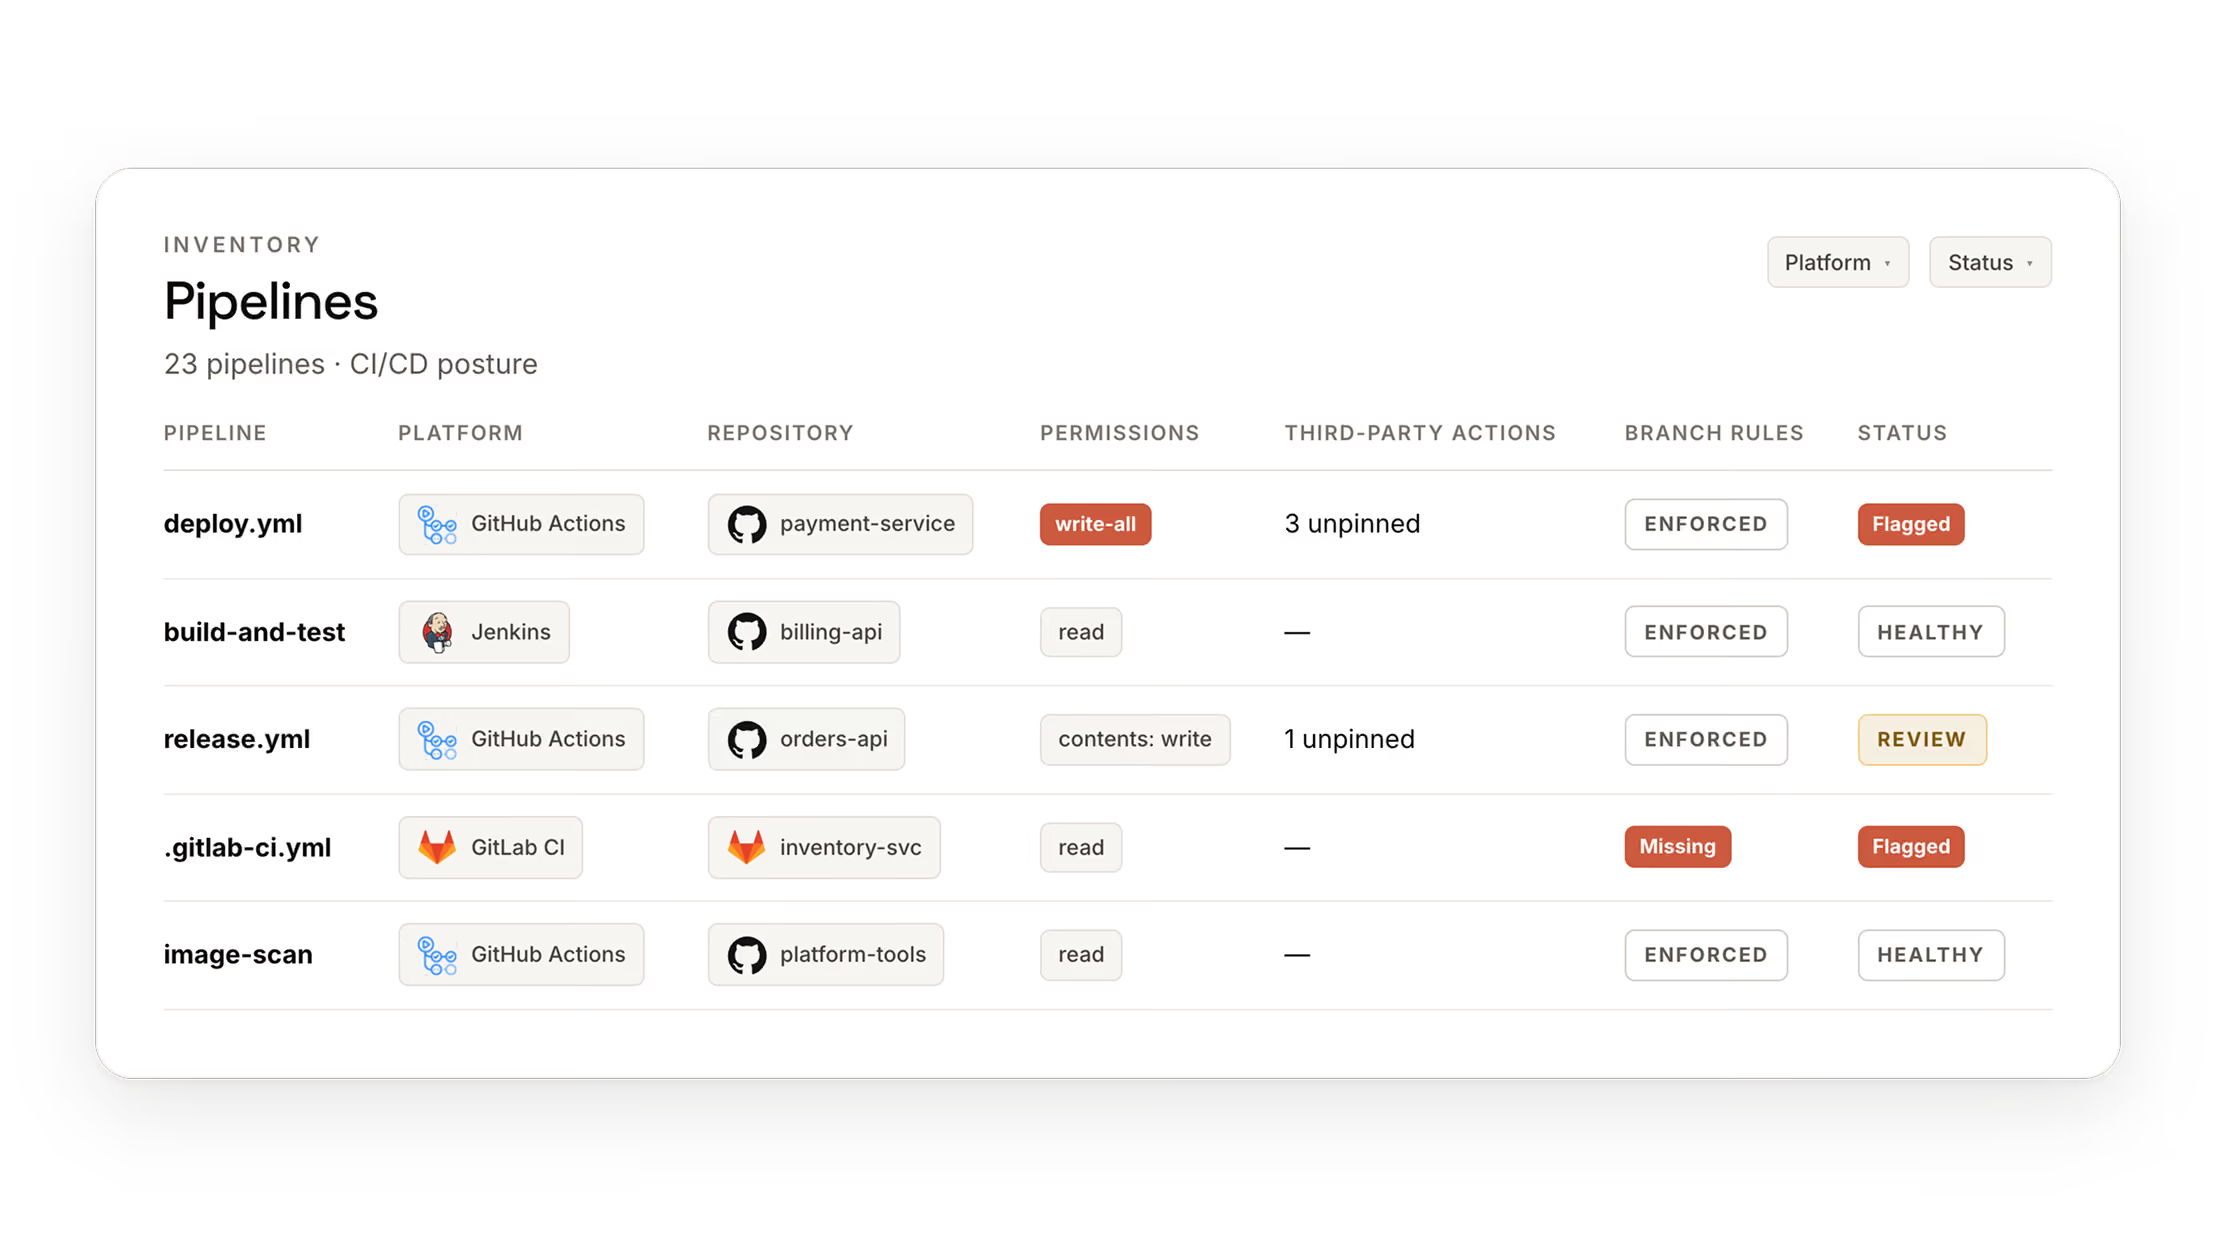
One risk model scores every finding the same way.
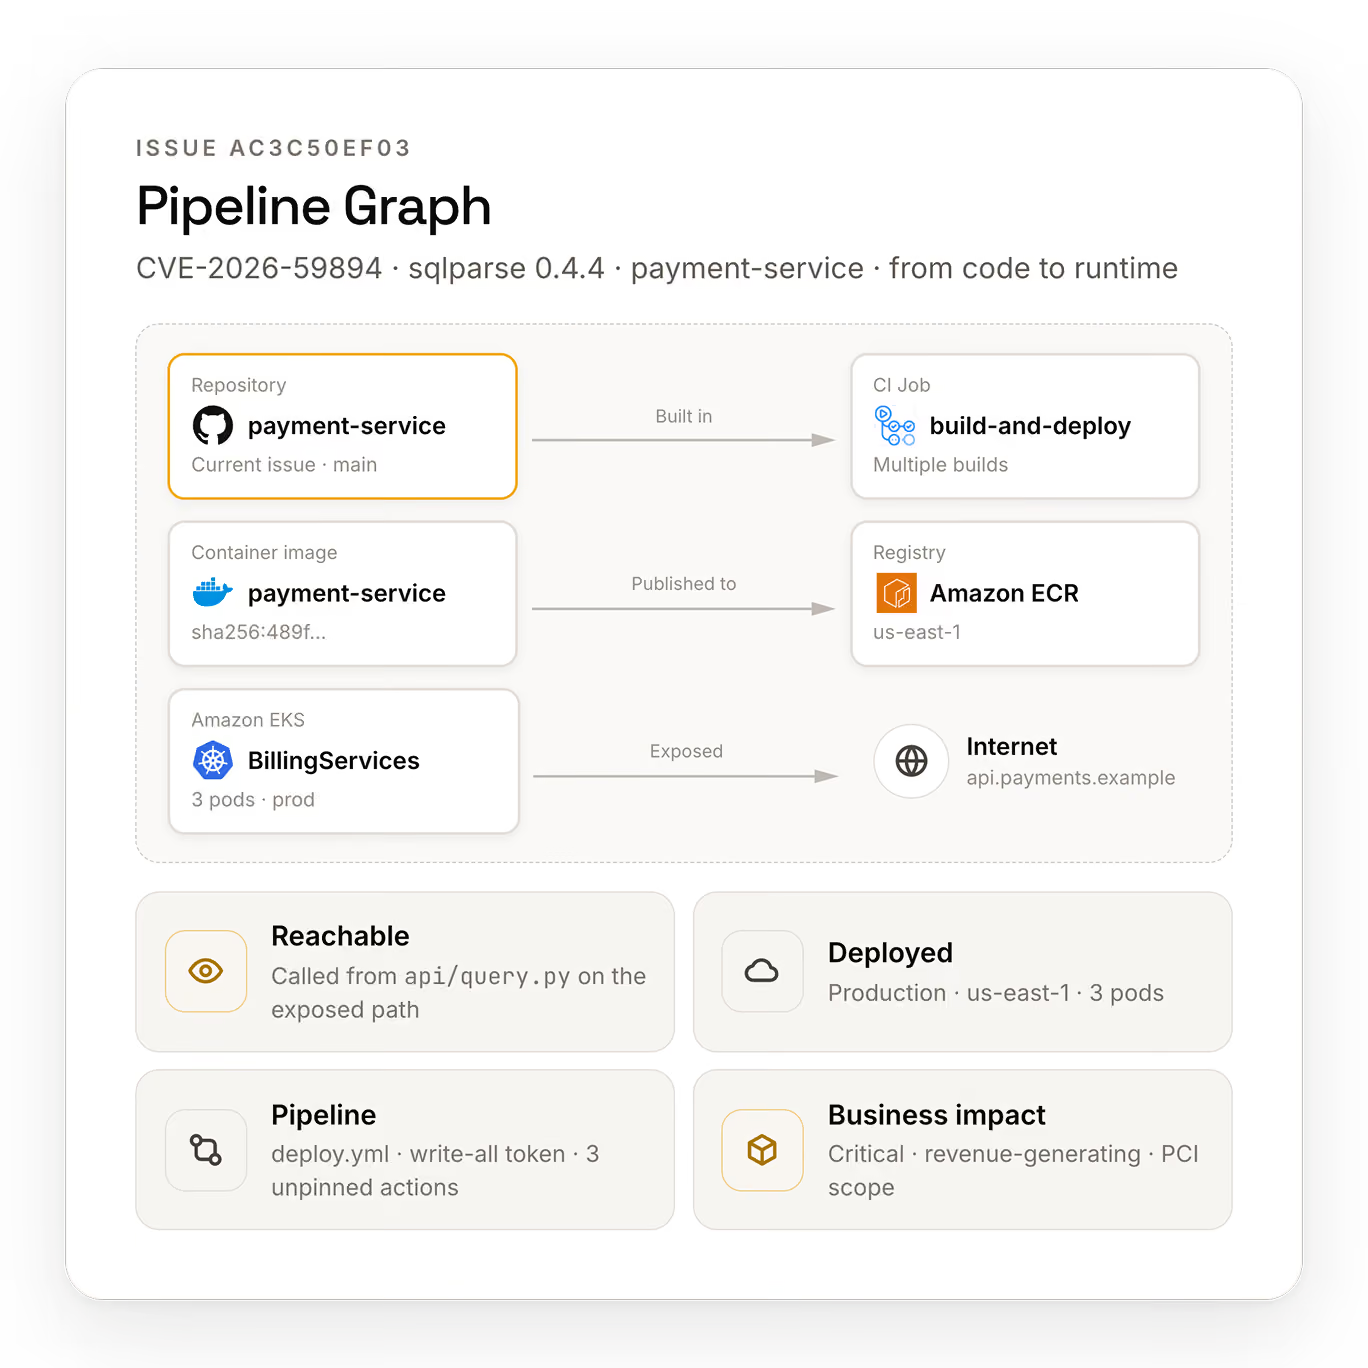
Reachability and business context feed one risk model, so severity means the same thing whether a finding came from Legit or a connected 3rd party scanner.
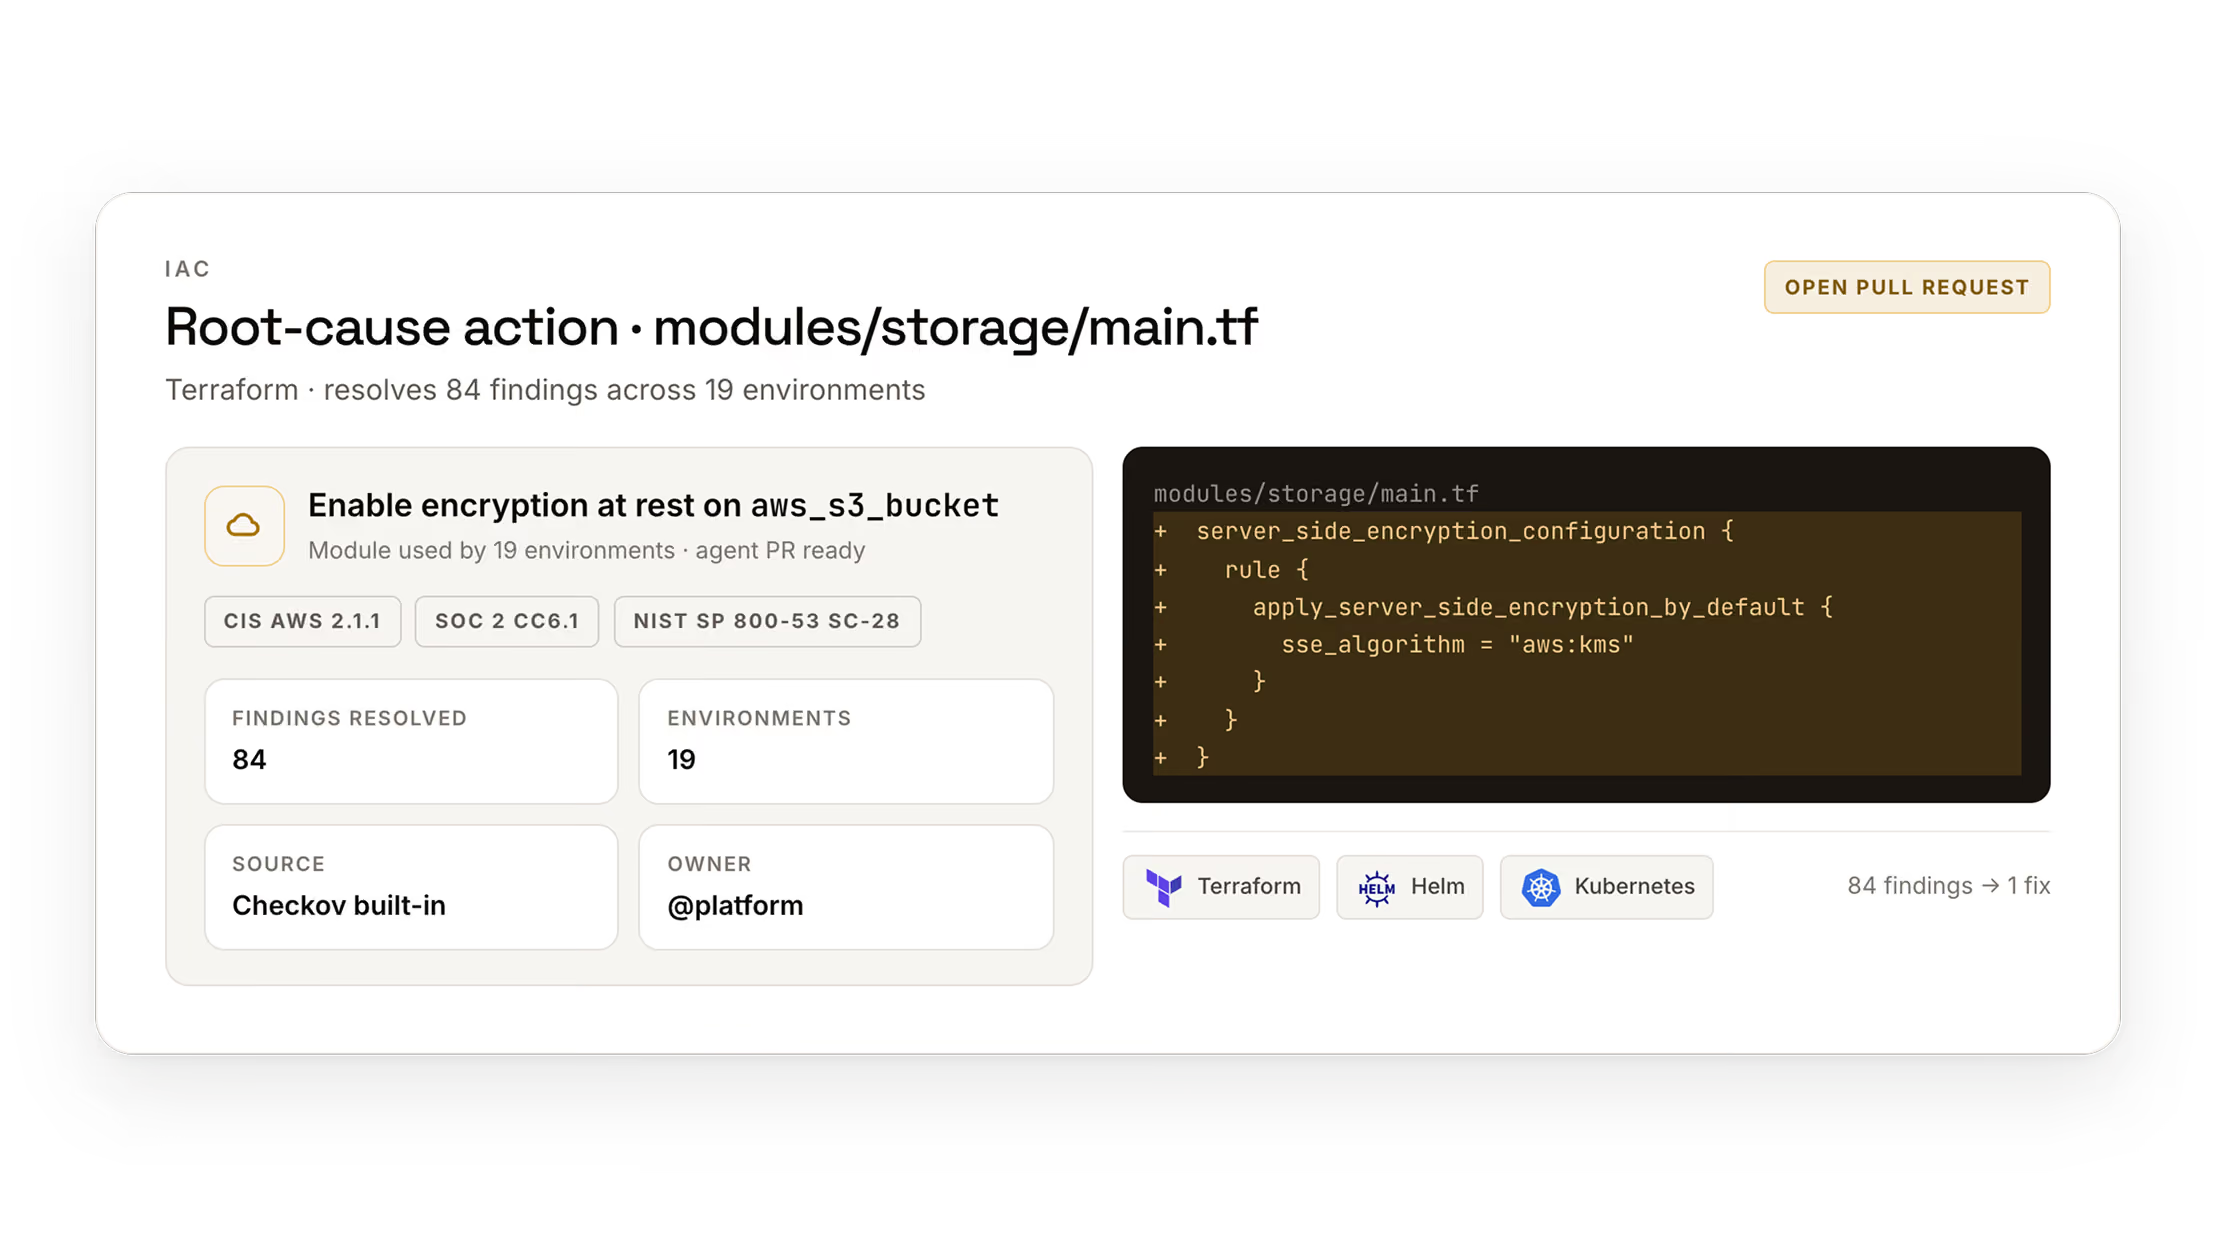
Remediation agents plug into your existing workflow.
Agents open pull requests through your SCM, routed to the right owner, so remediation fits the architecture you have instead of replacing it.
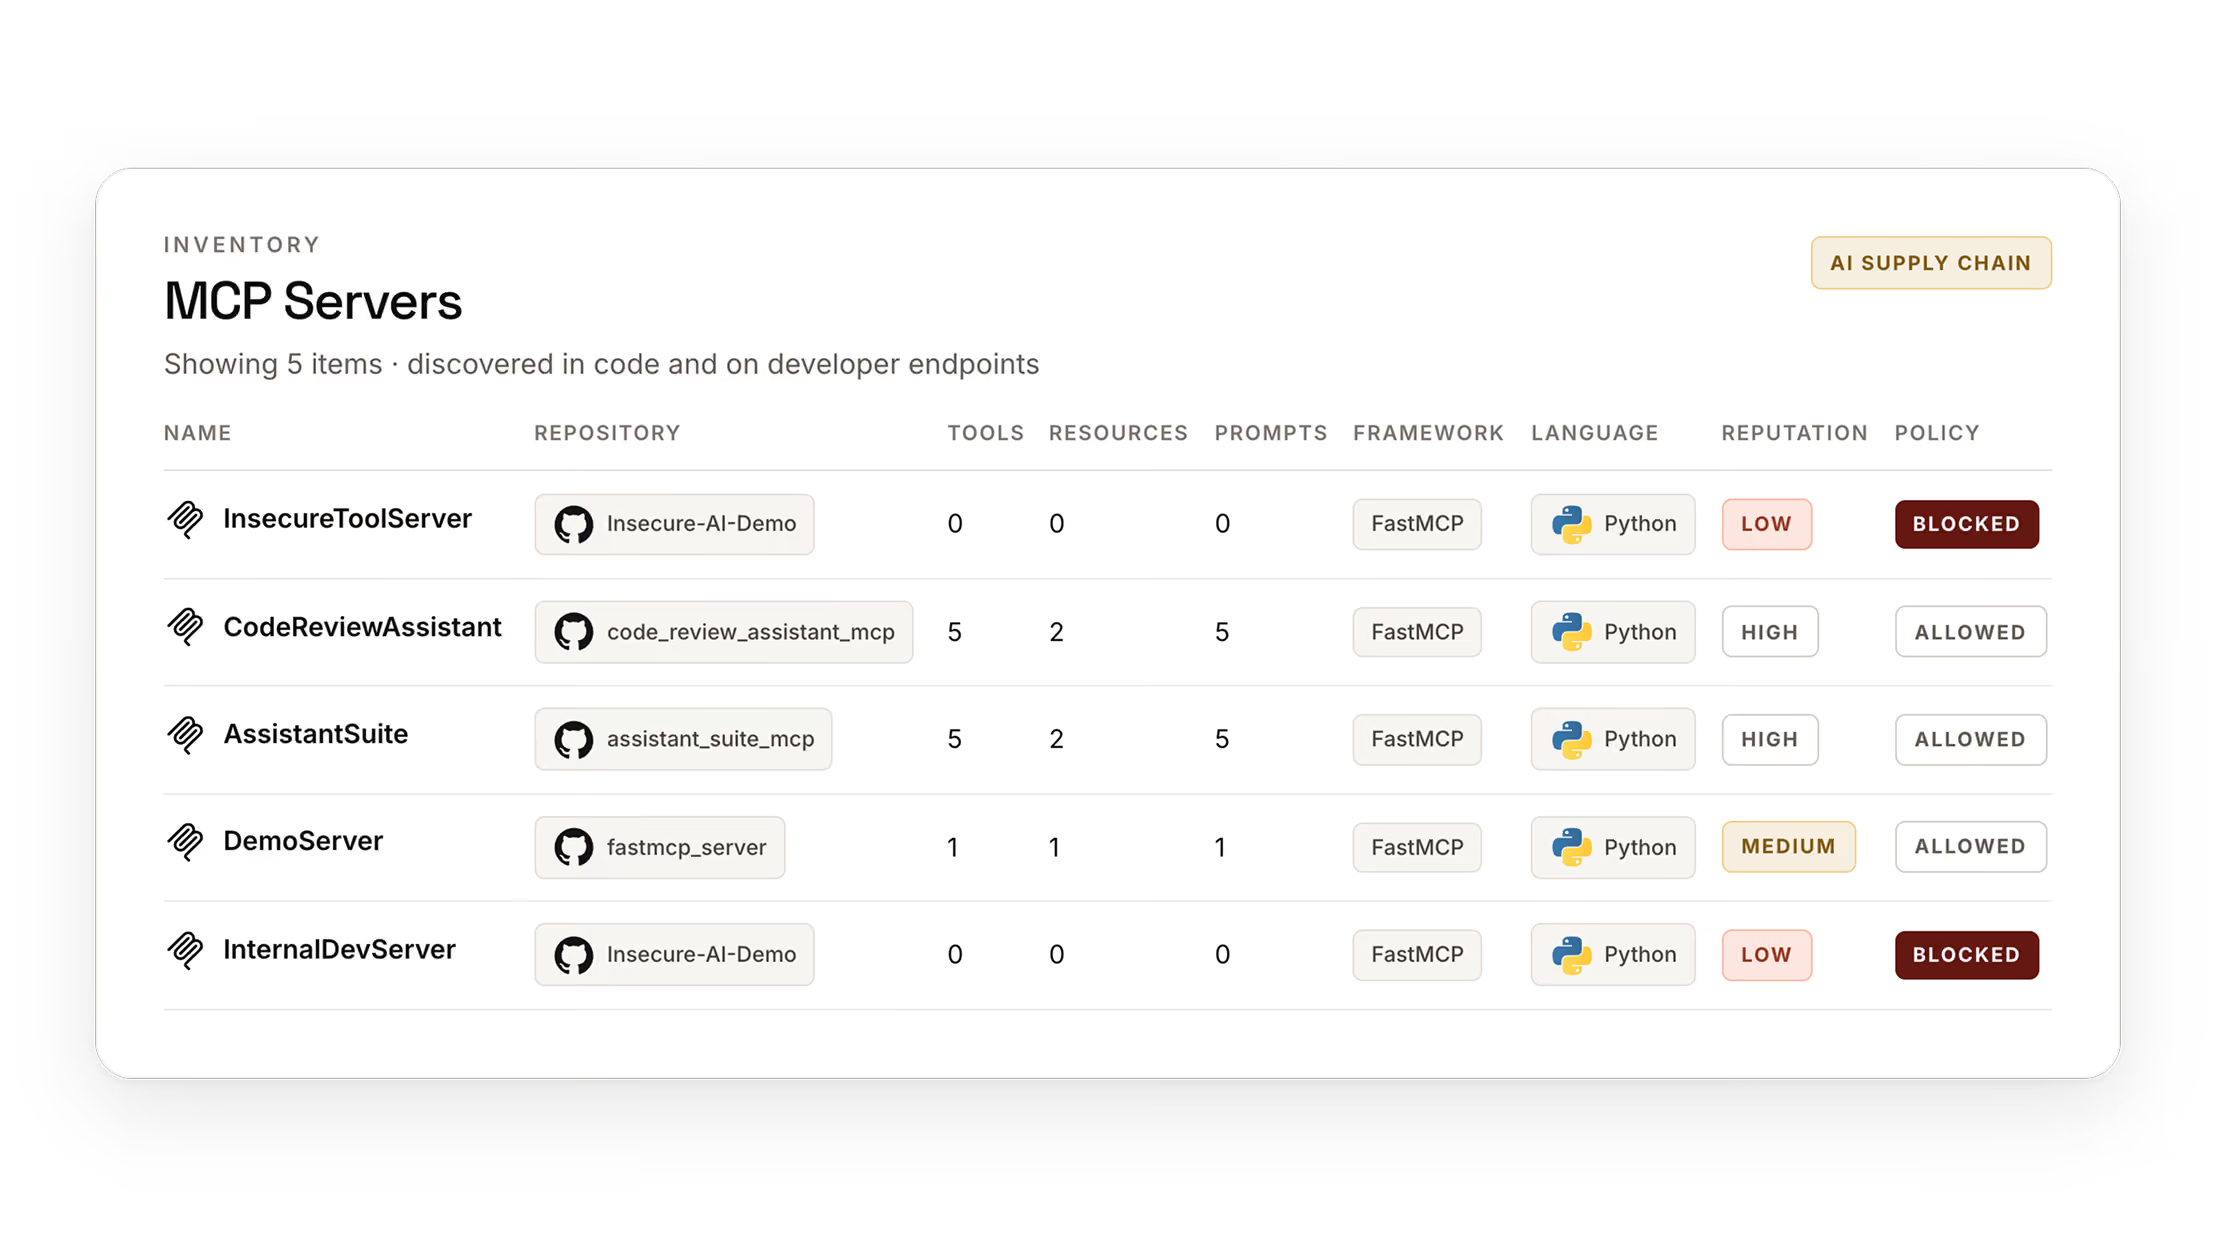
What changes with Legit
A single context layer for AppSec, not another silo to manage.

Context and reachability analysis reduce vulnerability noise by more than 90%, no matter which scanner in the stack surfaced the finding.

AI-driven detection cuts false positives by over 95%, validated in secret scanning, so severity means the same thing across every connected tool.

Legit is rated 4.8 on Gartner Peer Insights by architects who've run it alongside their existing stack.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."


More insights for modern AppSec teams

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
Agentic Remediation Just Got Bigger: Now Fixing Vulnerabilities in Your Dependencies, Not Just Your Code
Legit Security's Agentic Remediation now tackles vulnerabilities in dependencies, ensuring faster, verified fixes and enhancing AppSec in an AI-driven landscape.