
Legit Security vs ArmorCode Comparison.
Explore a side-by-side analysis between Legit Security vs. ArmorCode and see why Legit Security is the best ASPM option for protecting your business.
How Do ArmorCode and Legit Security Compare?
Prevent vulnerabilities earlier. Prioritize the risks that matter. Automate remediation.

ArmorCode mainly aggregates vulnerabilities from existing tools; Legit also prioritizes and root-causes them for faster remediation.

ArmorCode relies entirely on external tools; Legit brings its own SCA, SAST, pipeline, and source control scanners, plus integrations with your stack.

ArmorCode focuses on a consolidated view of findings; Legit gives full software factory visibility to prioritize and remediate the highest risk areas.

ArmorCode doesn't map controls to compliance frameworks; Legit maps to PCI-DSS, ISO 27001, NIST 800-53, FedRAMP, SLSA, and OWASP standards.

Legit context unifies an app's business criticality, exposure, sensitive data, and AI usage into one risk picture that ArmorCode doesn't provide.
Why Legit Security is the Best Alternative to ArmorCode
Legit brings prevention, context, and autonomous remediation together in a single platform, helping teams secure AI-driven development with no developer slowdowns.
Prevent vulnerabilities before they're introduced.
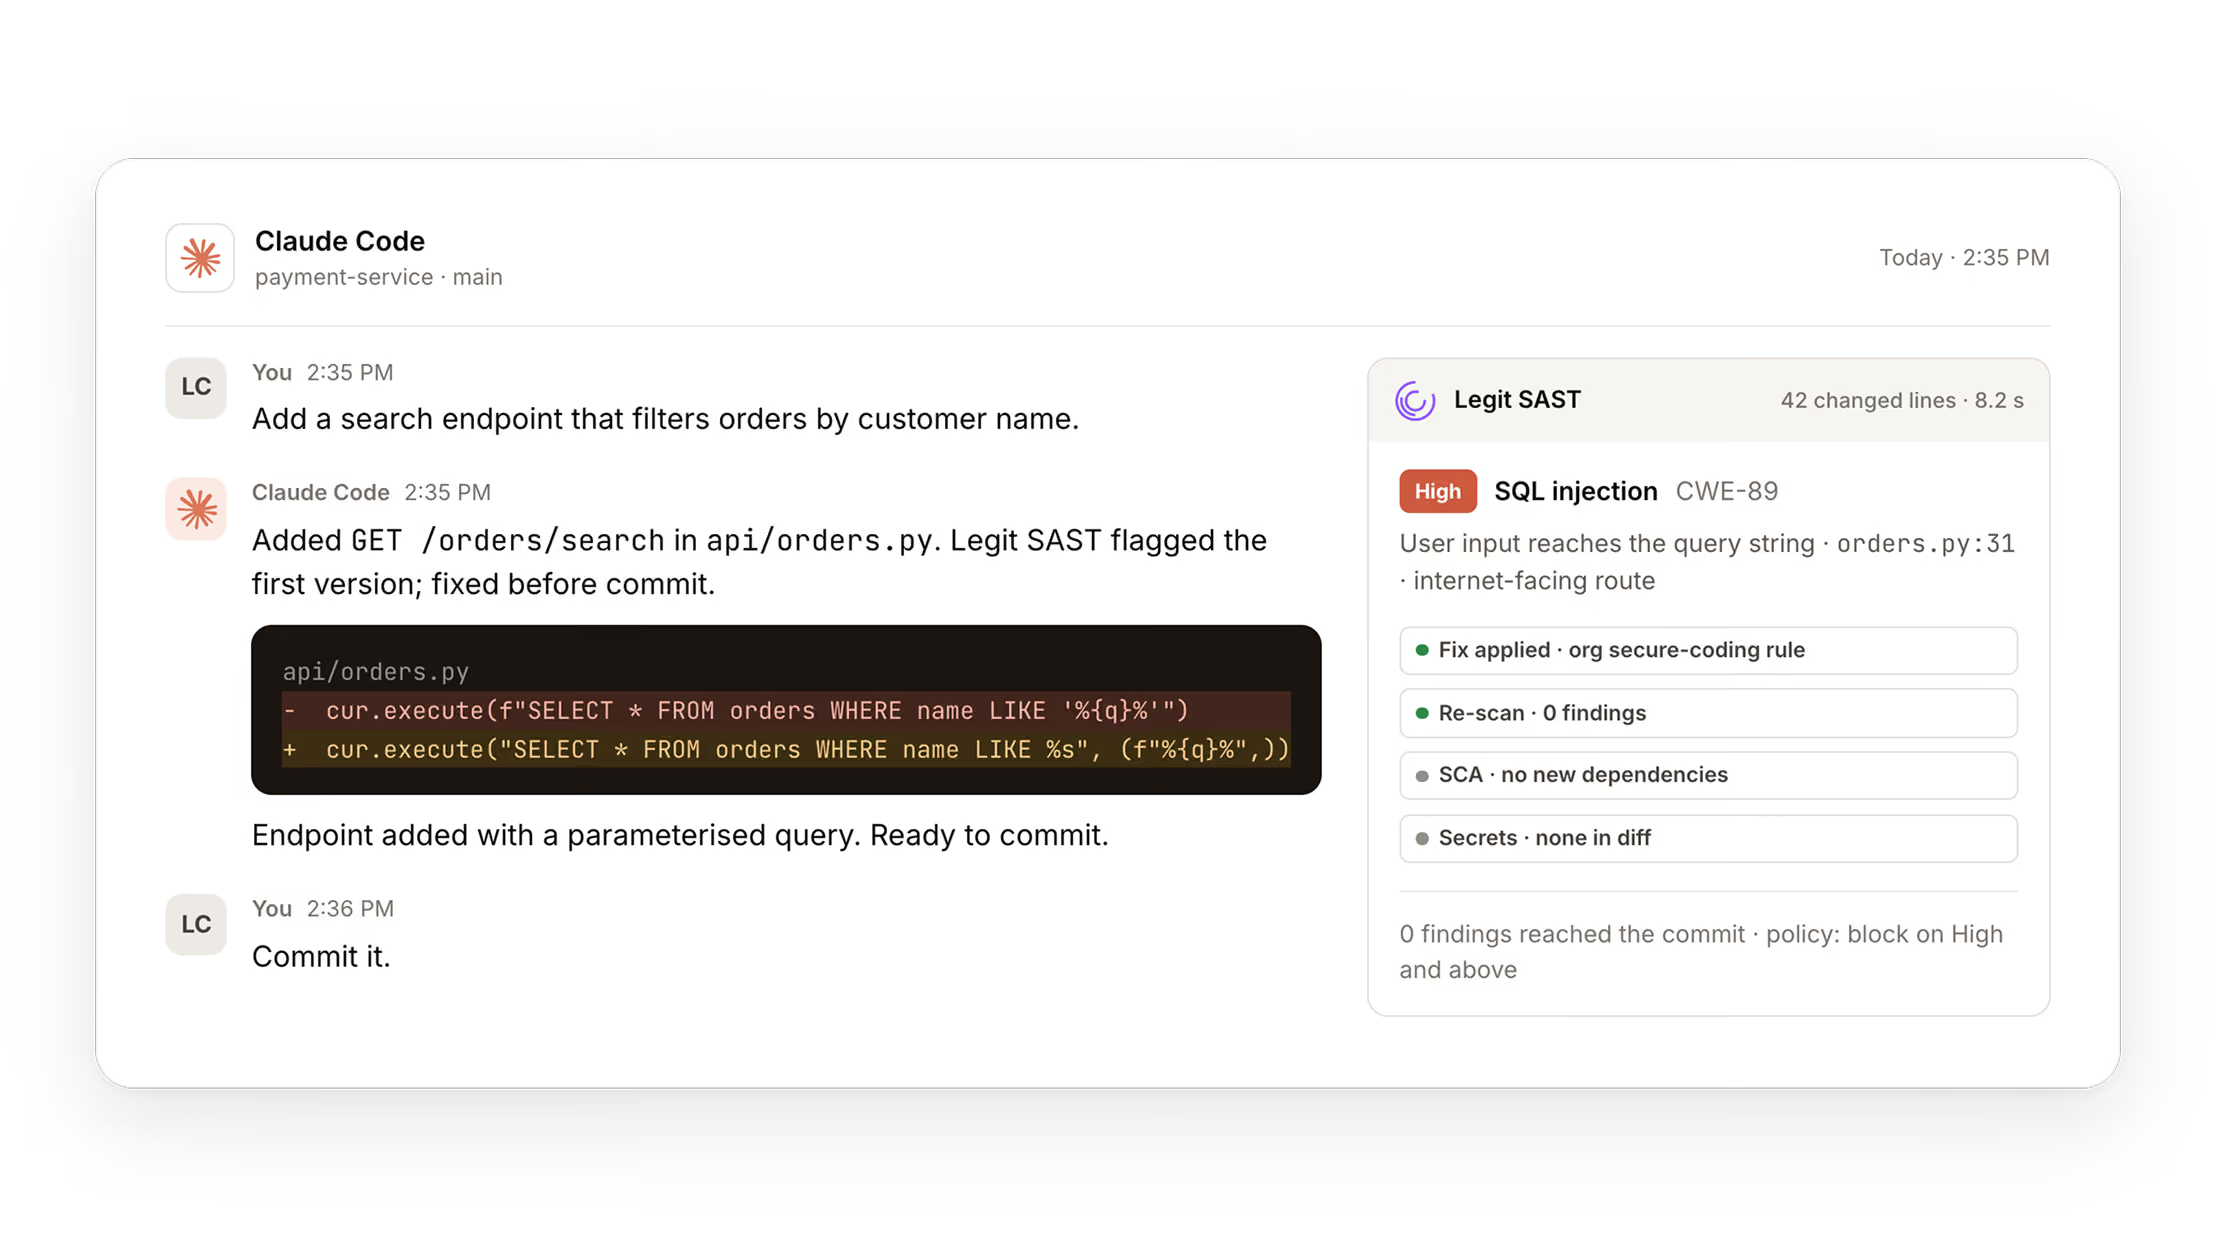
Provide developers with real-time guidance during AI-assisted code generation to reduce risk before code reaches commit.
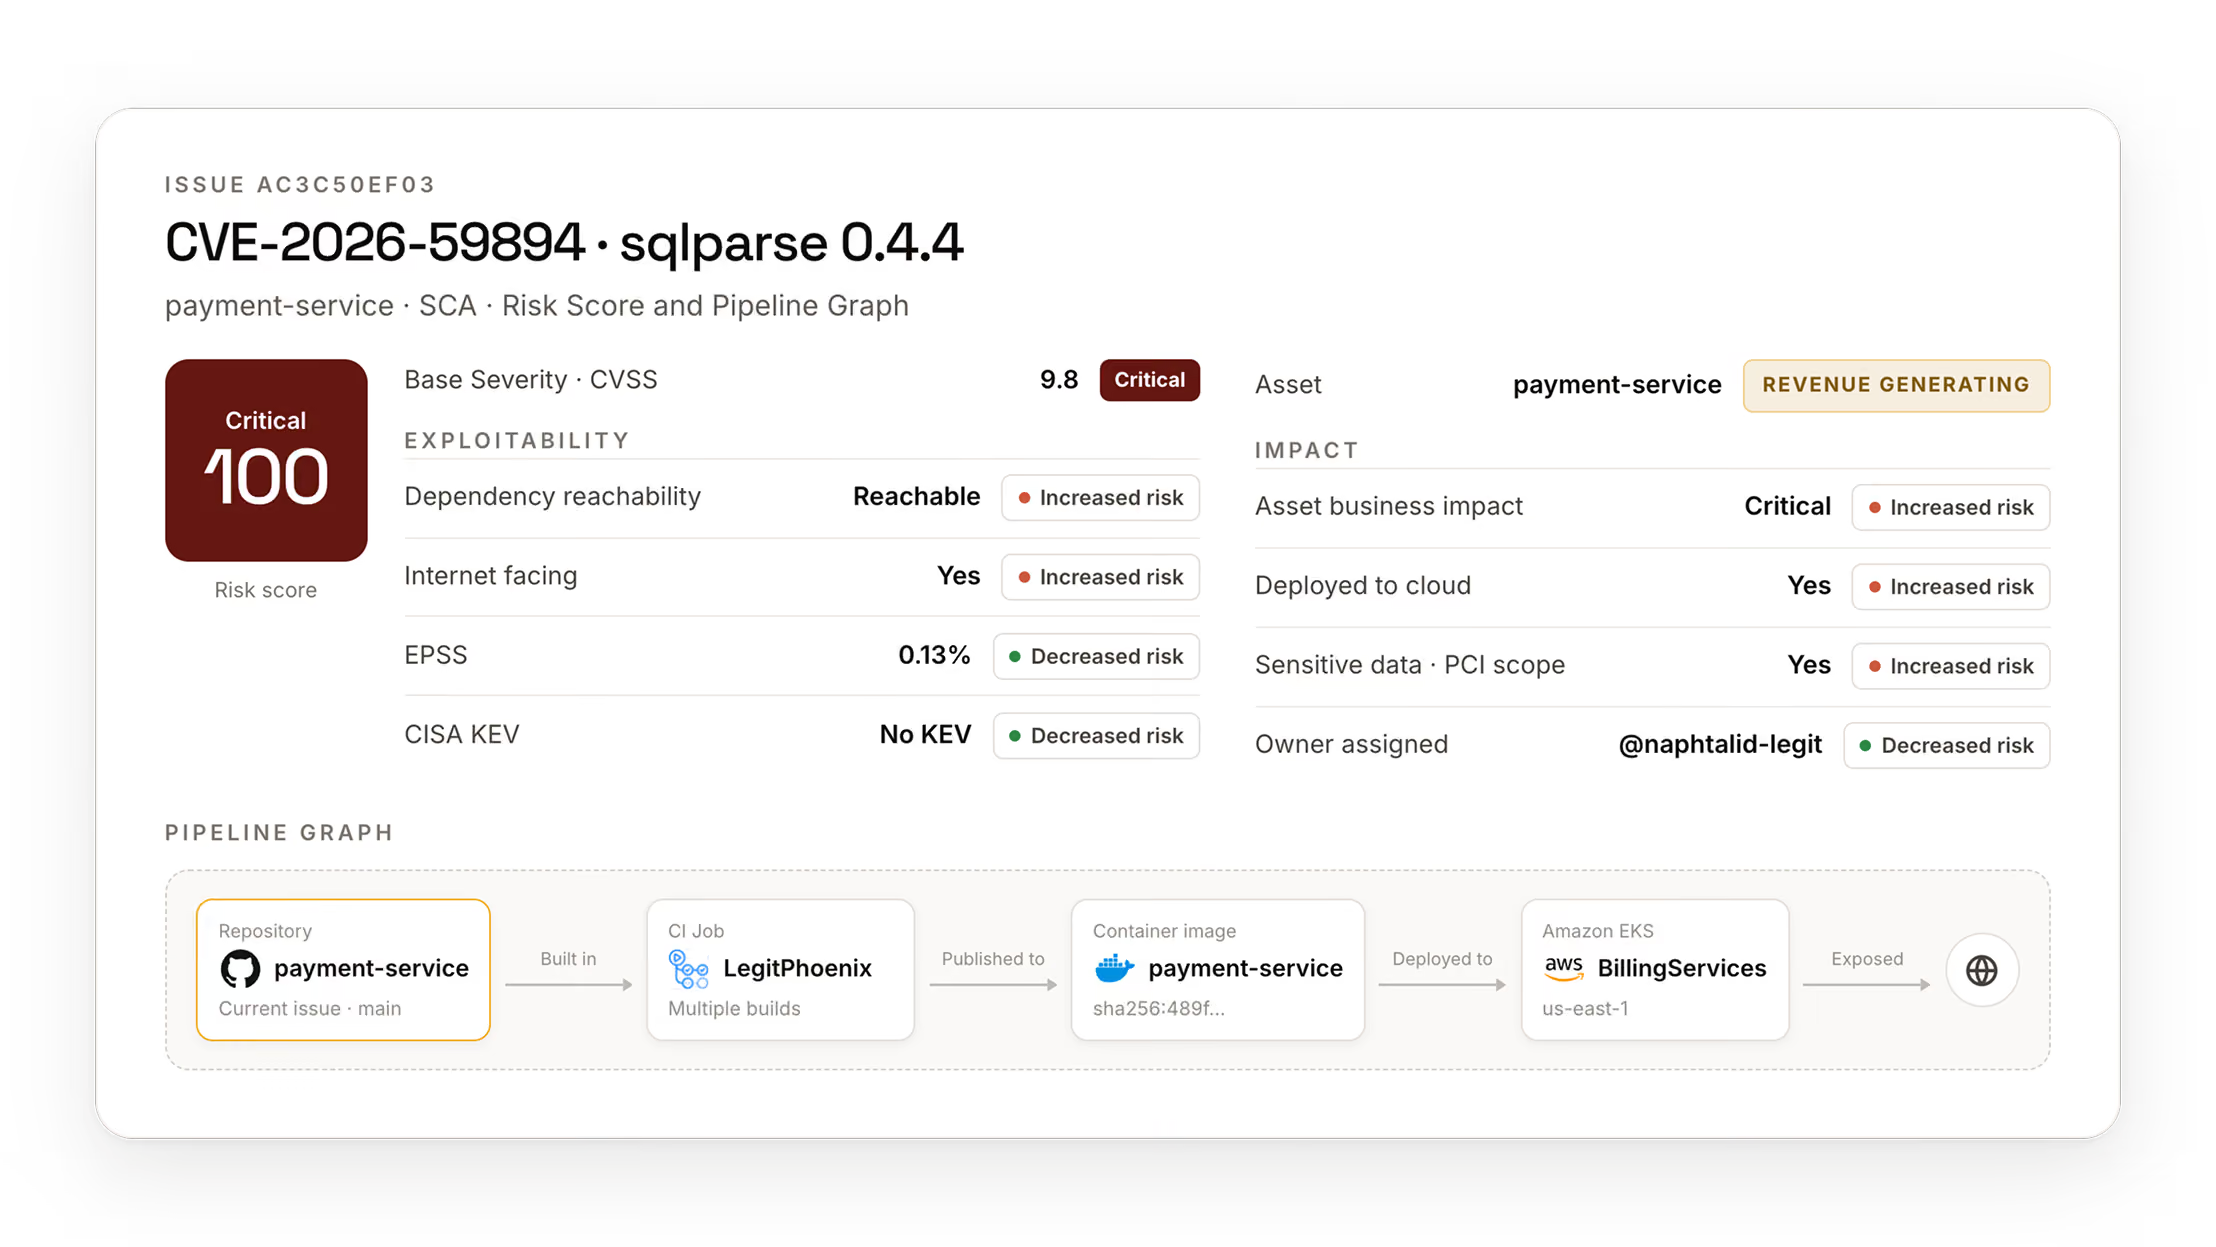
Rank risk by real business impact, not severity alone.
Legit context weighs an app's business criticality, exposure, sensitive data, and AI usage to surface the risks that matter most first.
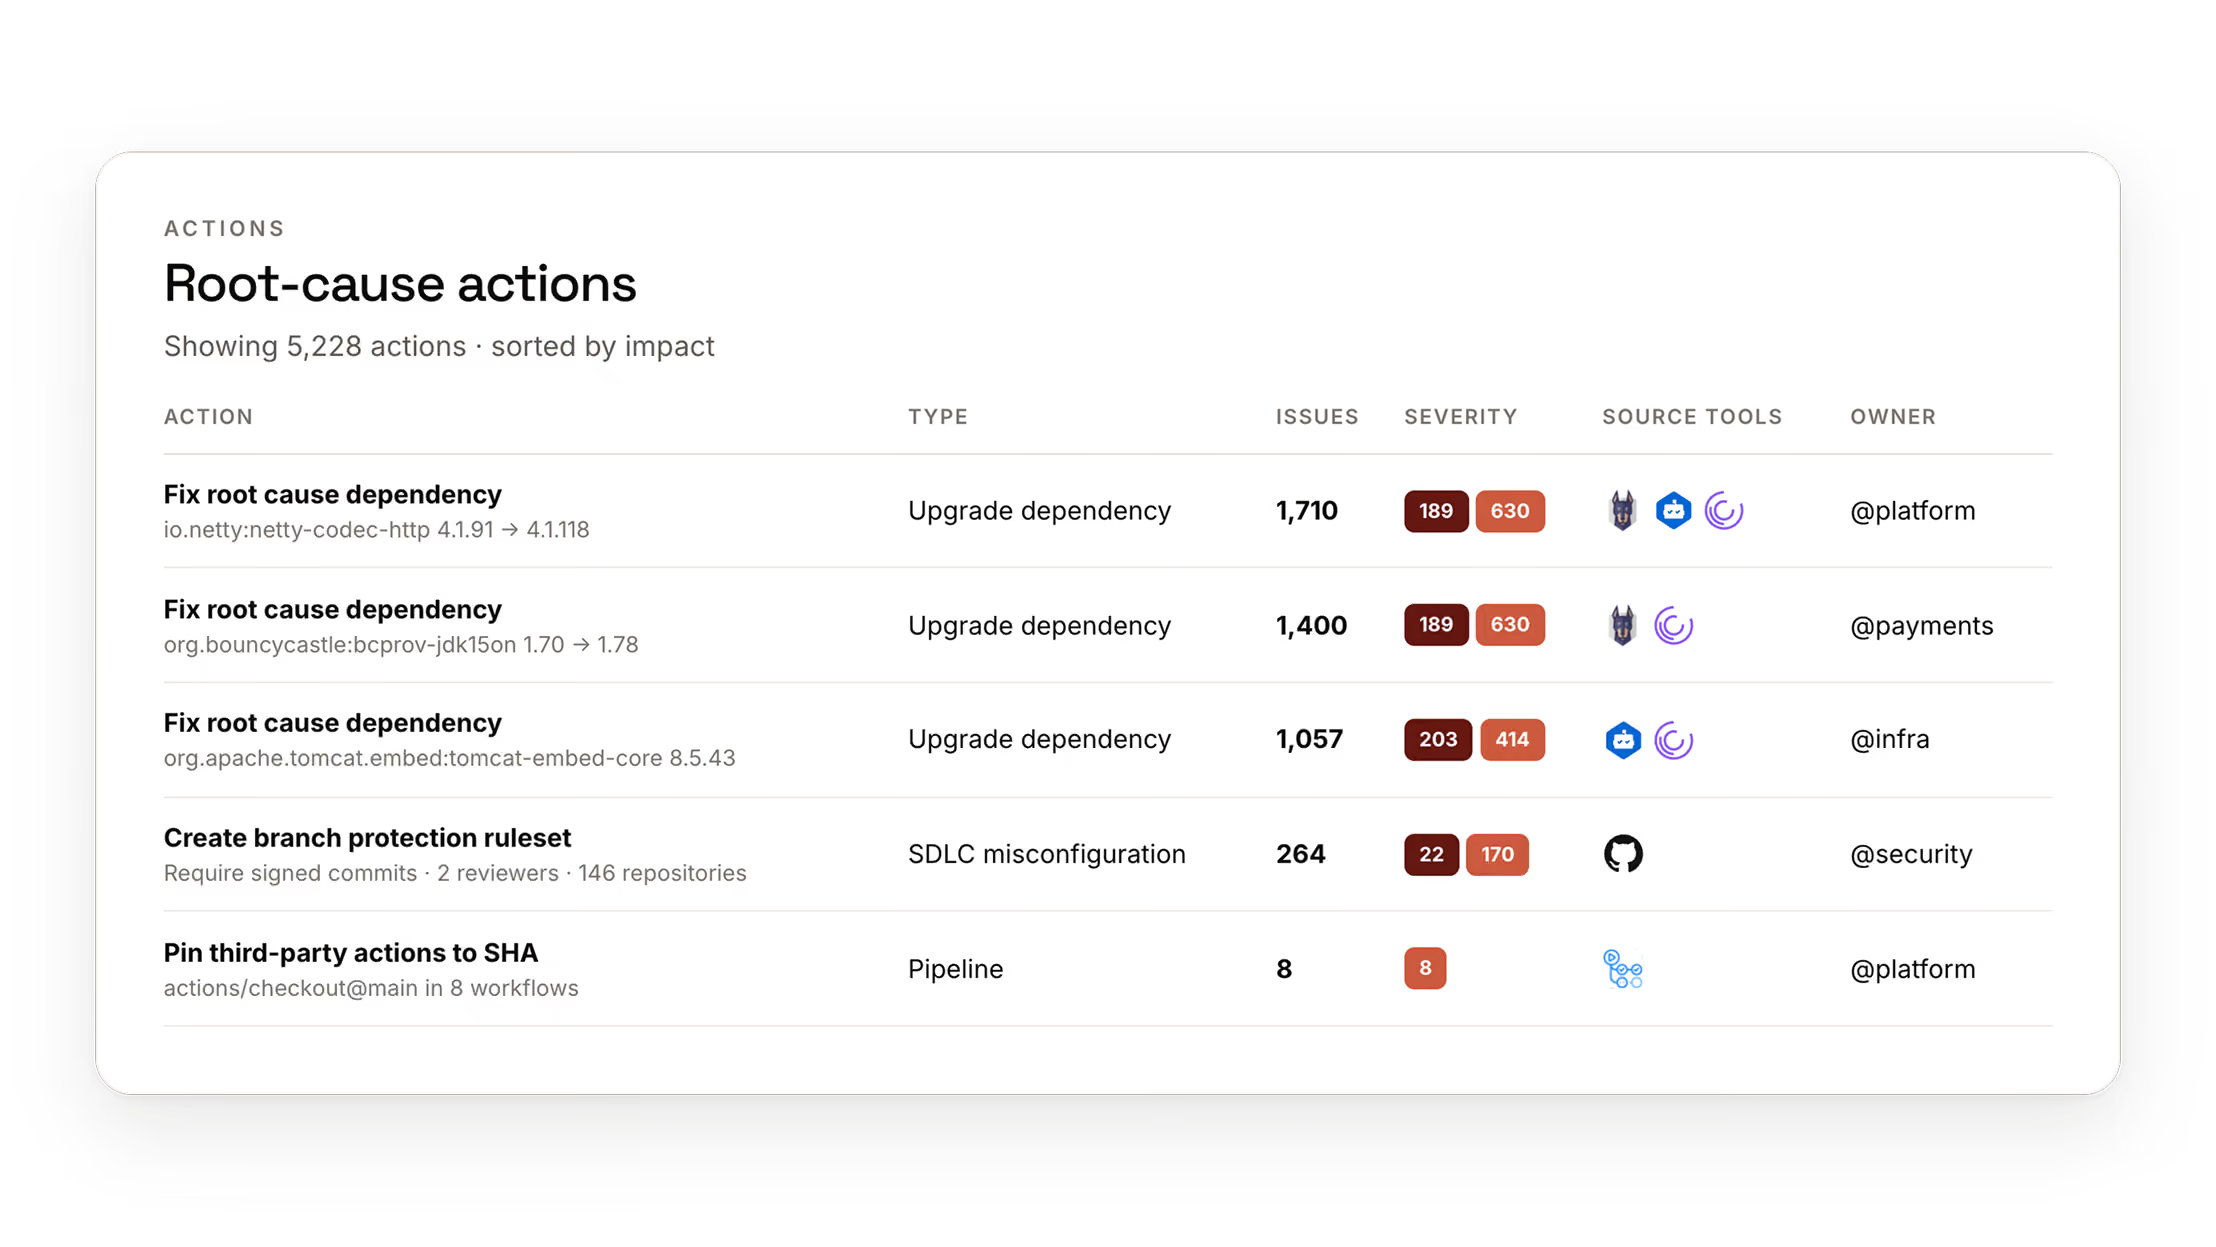
Fix root causes, not just symptoms.
Legit pinpoints the root cause behind multiple findings, so one fix resolves many issues and cuts the burden on developers.
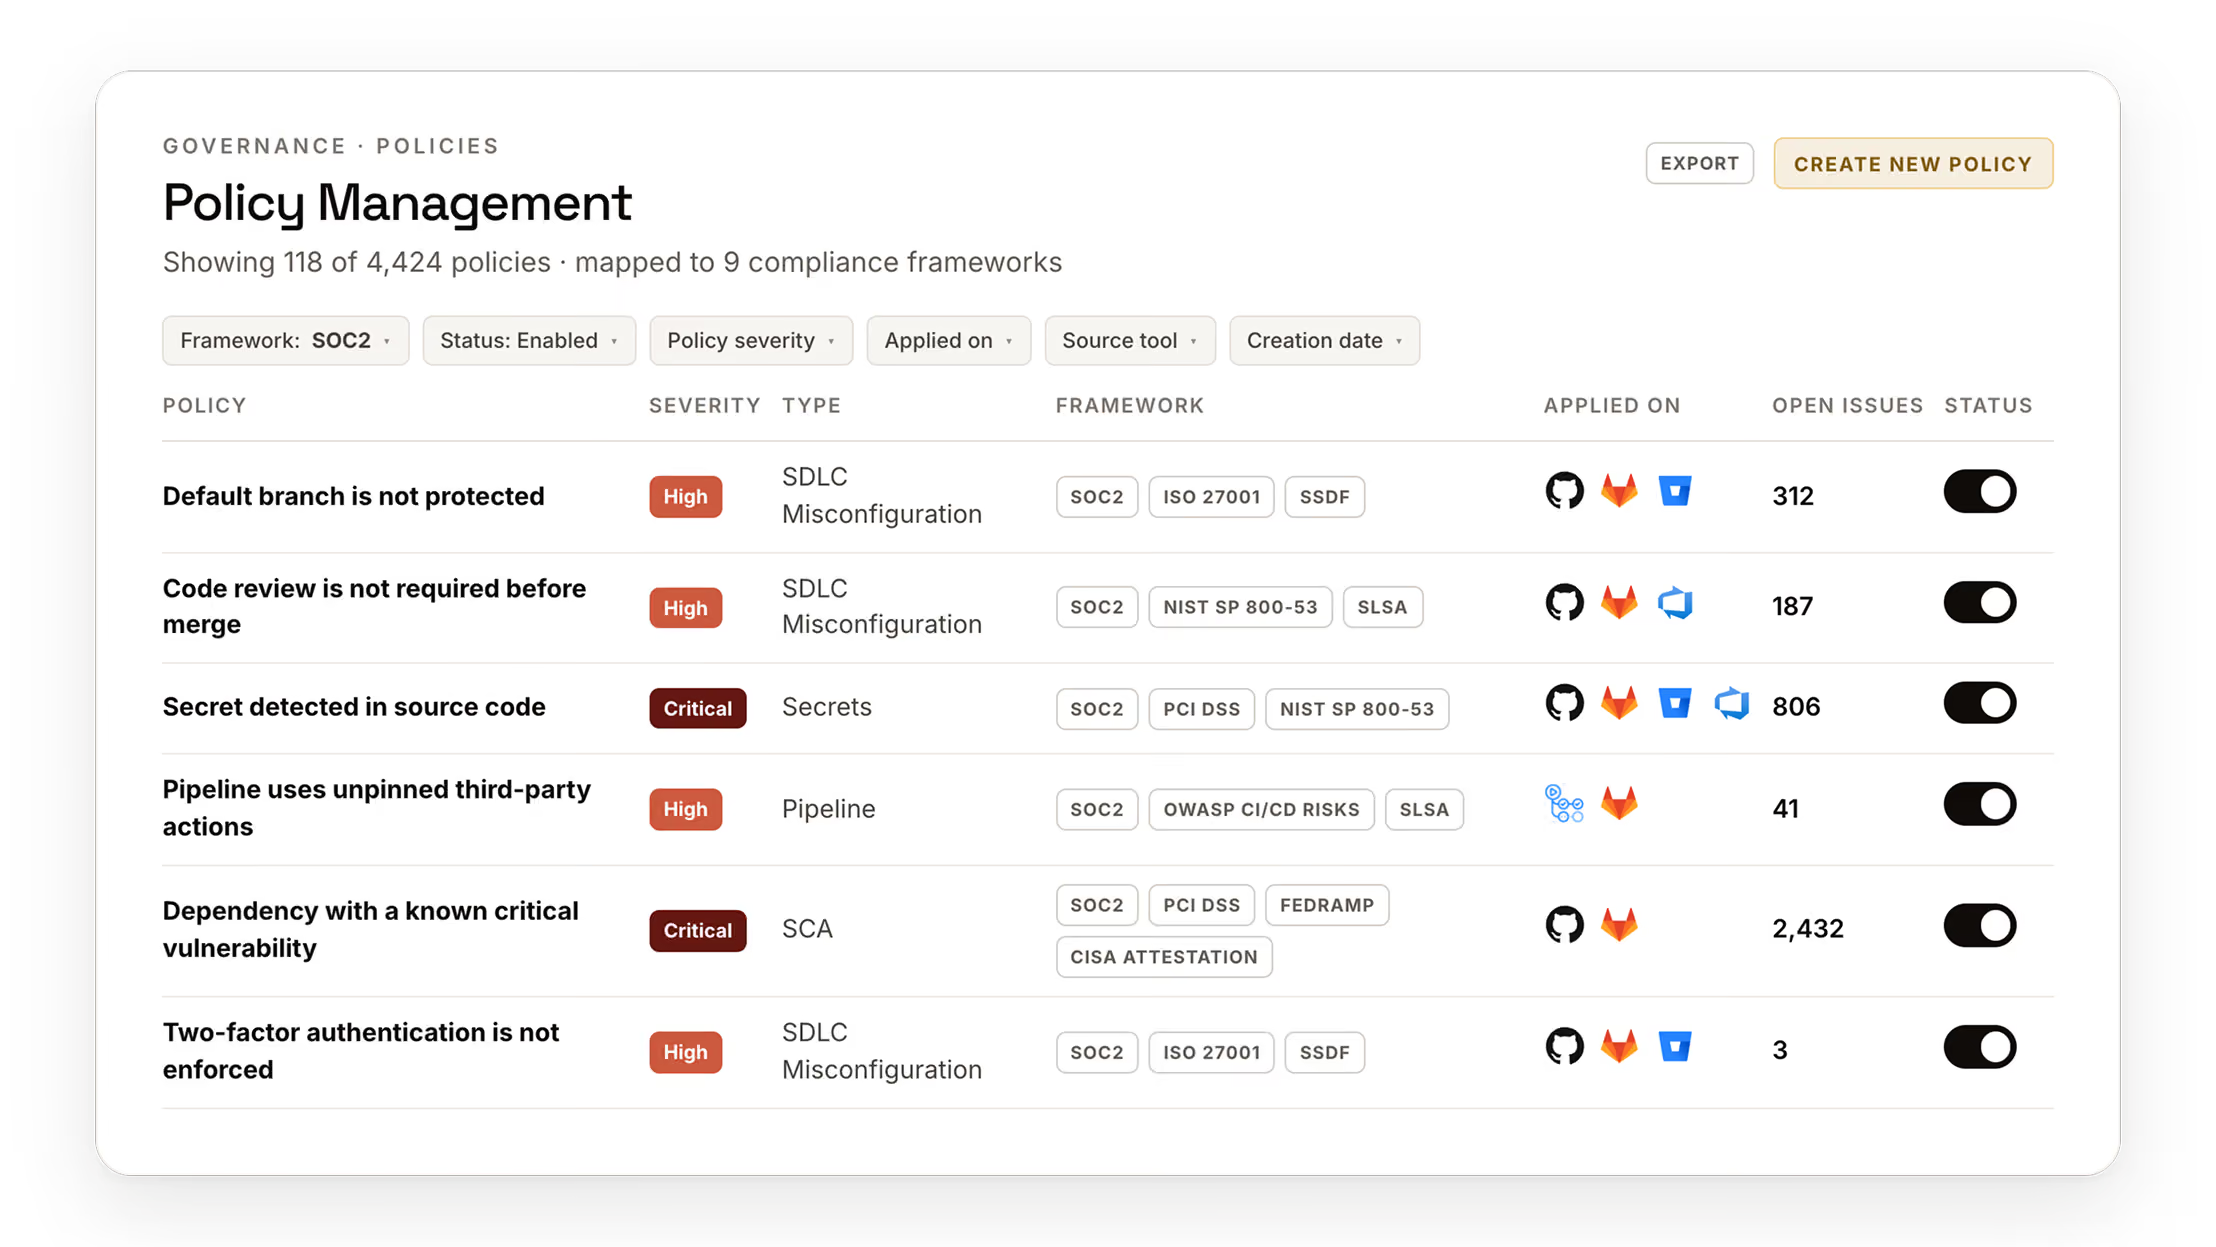
Map controls to the frameworks you're held to.
Legit aligns security controls with PCI-DSS, ISO 27001, NIST 800-53, FedRAMP, SLSA, and OWASP, with real-time alerts on compliance drift.
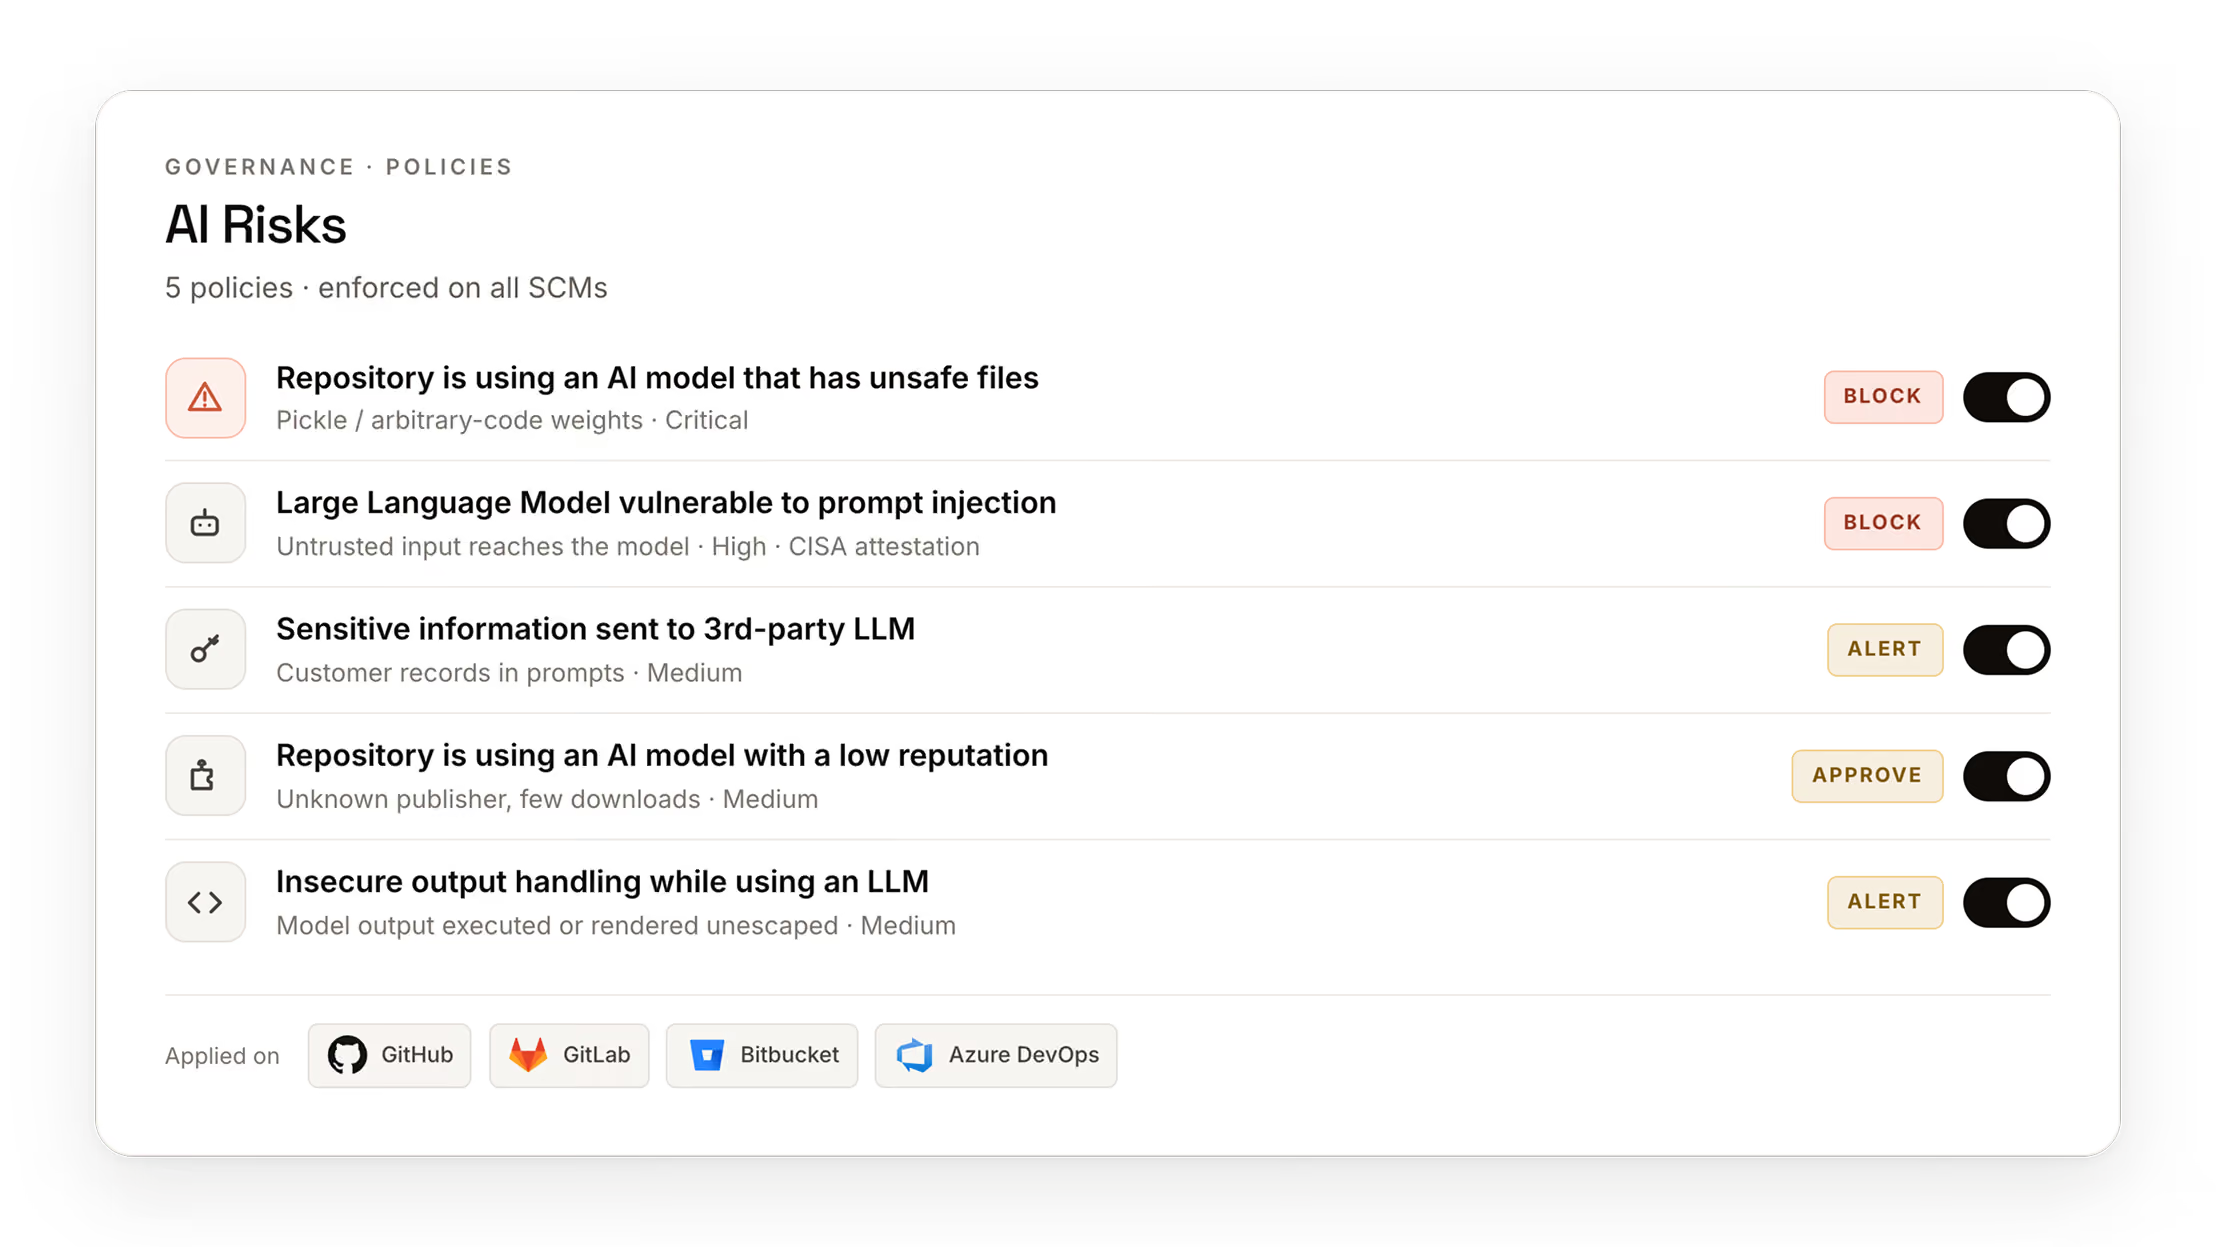
Govern how AI writes and ships code.
Legit inventories GenAI, LLM, and MLOps usage across your SDLC, giving security teams visibility and control over AI-generated code.
Request a Demo
Request a demo including the option to analyze your own software supply chain.


FAQ

More insights for modern AppSec teams
Why I Joined Legit
We believe that security tools had become very good at identifying problems, but that developers were still left with the hardest part: understanding those findings and turning them into secure code changes.

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.