
The new risk in insurance development

Legacy and modern systems don't talk.
Policy systems and customer-facing applications create integration points that legacy tools can't monitor, leaving blind spots attackers can exploit.

Audits eat time compliance needs.
Manual evidence collection for NAIC, HIPAA, and GDPR consumes hours while gaps persist, leaving point-in-time compliance instead of continuous assurance.

Not every finding threatens policyholders.
Generic severity scores don't show which vulnerabilities put PHI or PII at risk, so critical issues wait behind low-priority noise.
Traditional AppSec wasn't built for hybrid insurers.
Traditional AppSec
Misses legacy integration points
Relies on manual audit evidence
Scores risk by generic severity
Produces point-in-time compliance
Agentic

Unifies legacy and modern visibility
Automates audit-ready evidence
Prioritizes by policyholder data risk
Delivers continuous compliance
Meet AgenticAppSec.
Legit brings prevention, context, and autonomous remediation into a single platform, giving insurers continuous compliance across hybrid systems.
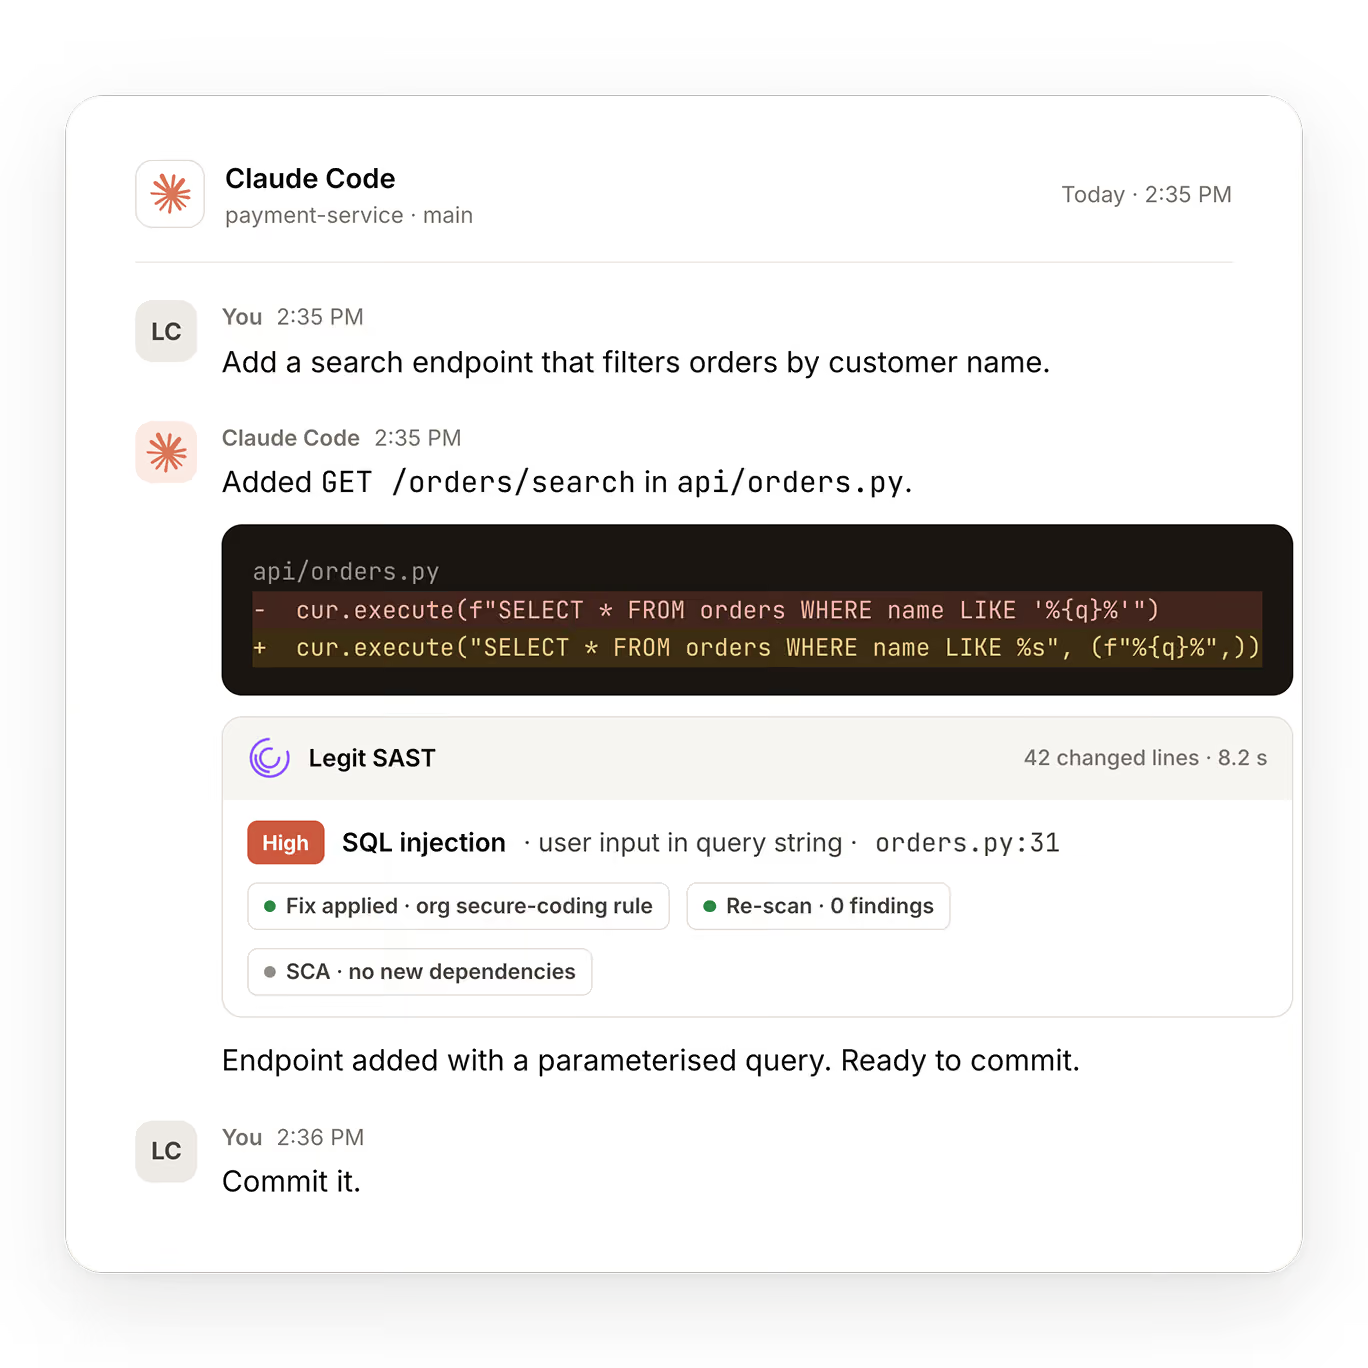
Stop vulnerabilities before they reach your repo.
Catch risky AI-generated code and exposed credentials before commit, reducing what reaches regulated production systems.
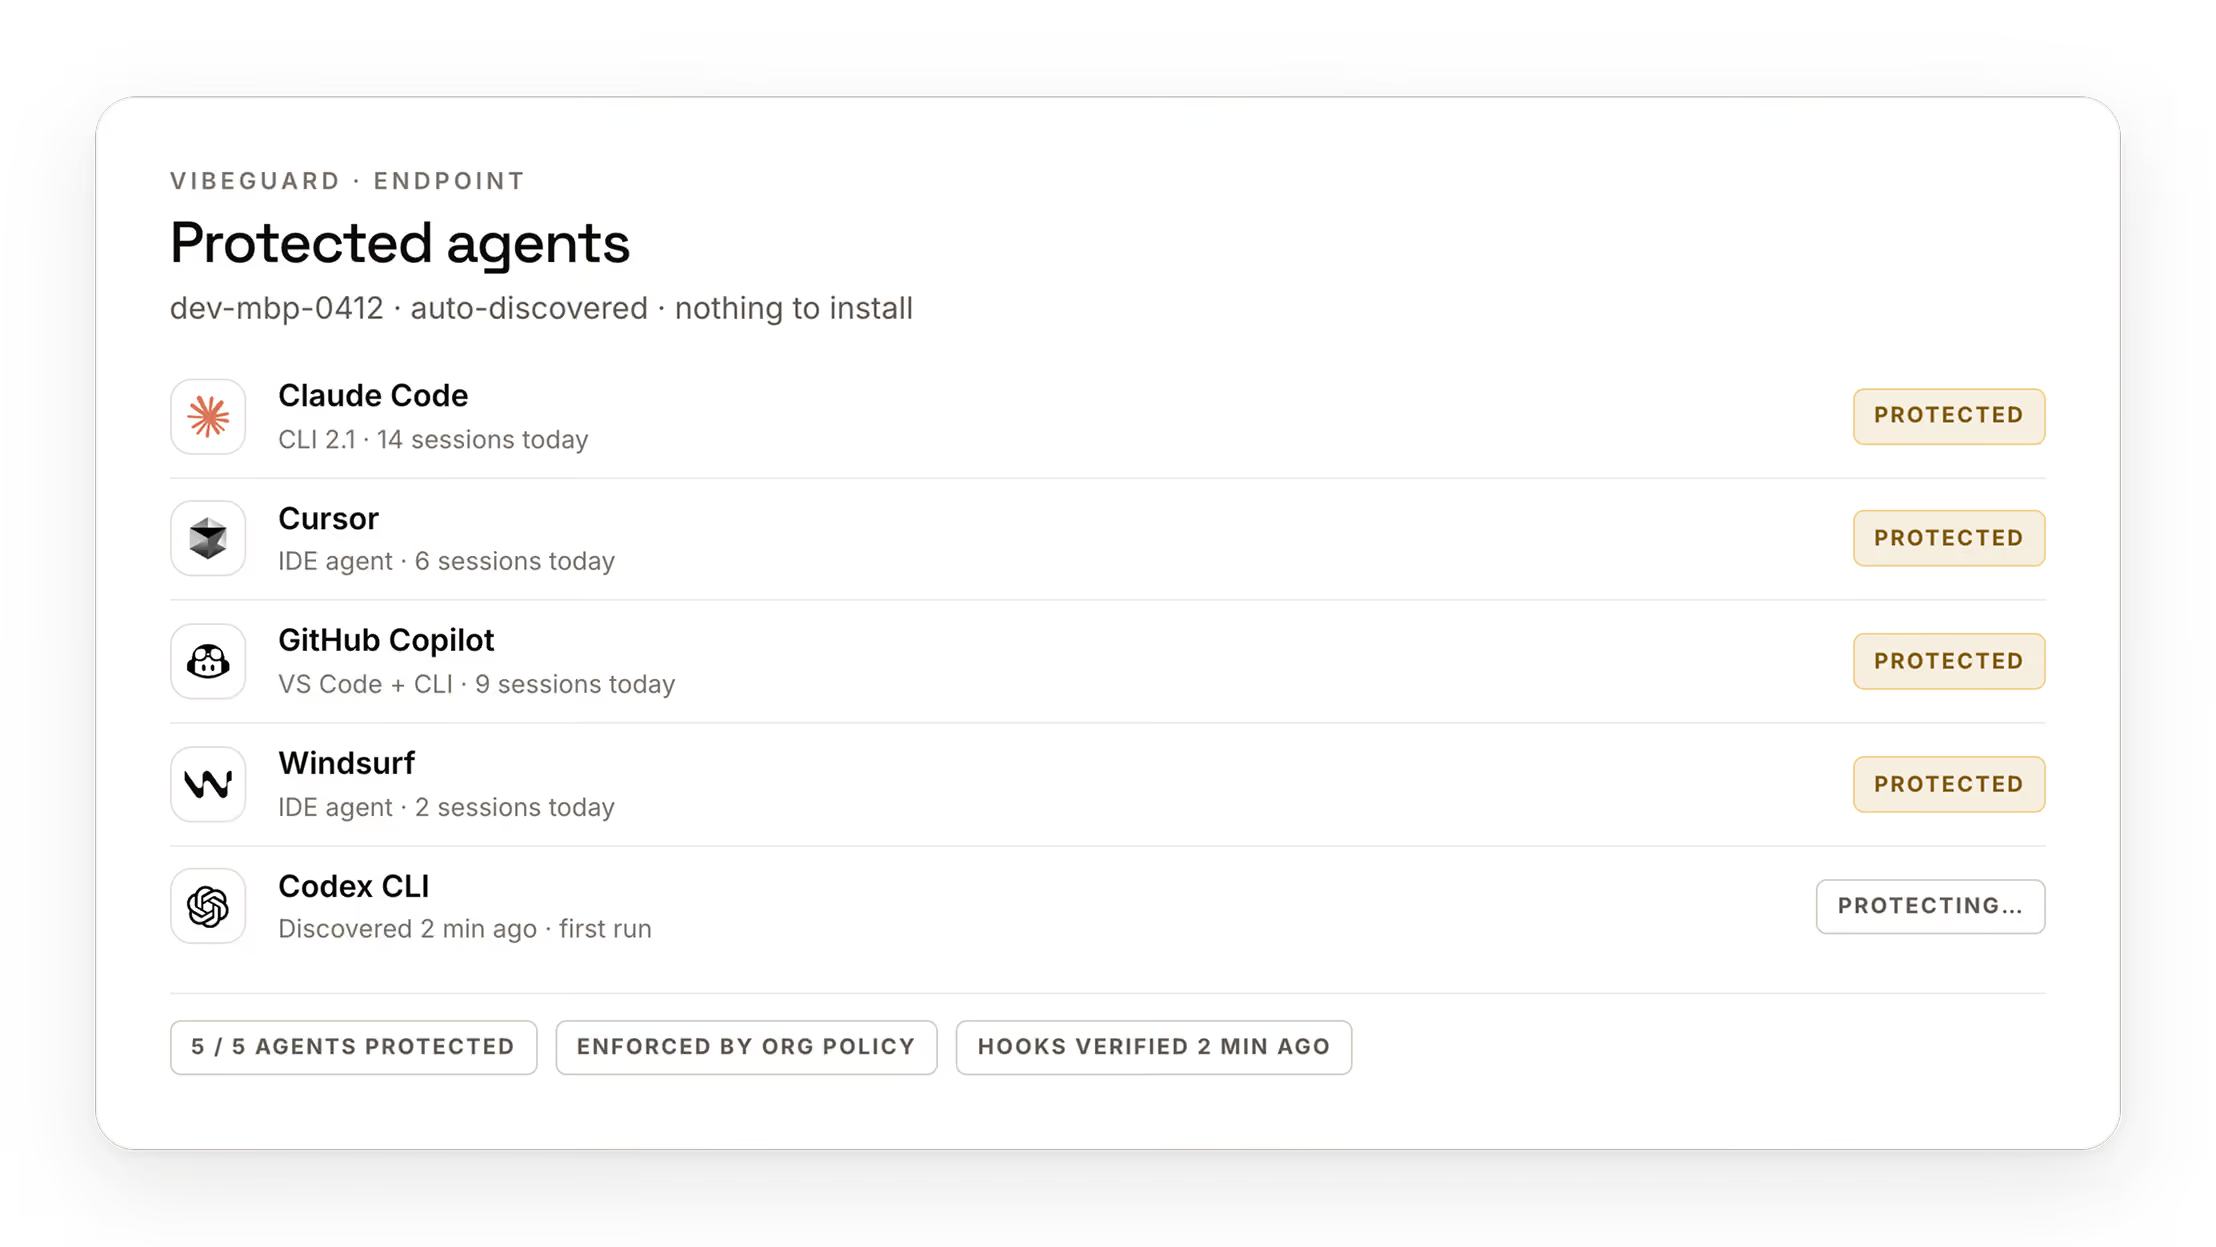
Focus on what threatens policyholder data.
Score every finding by proximity to PHI, PII, and regulated workflows, not generic severity scores.
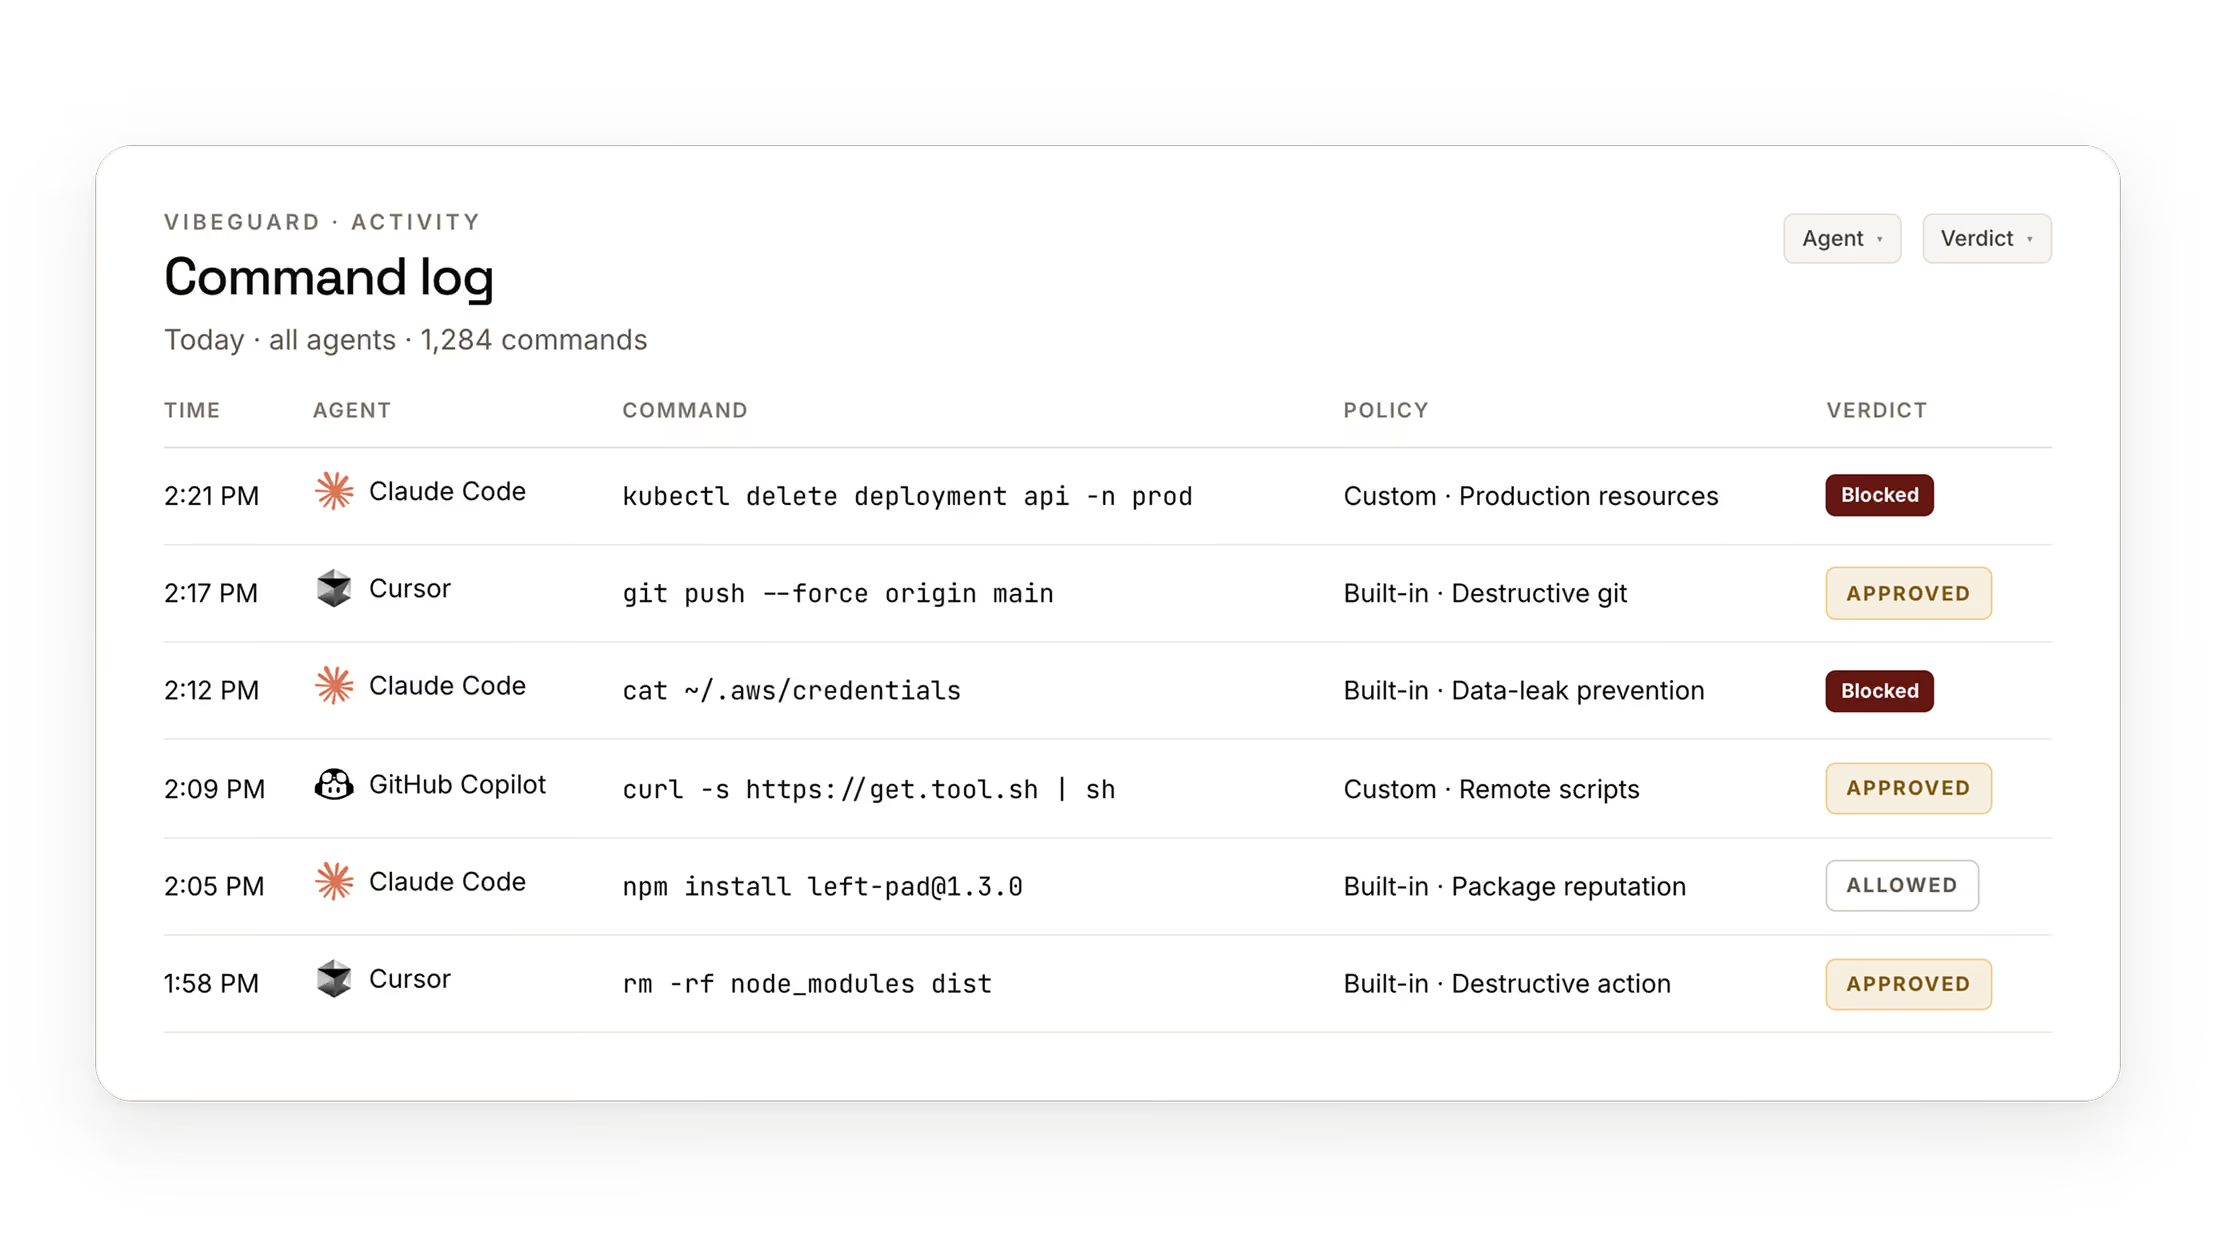
Fix root causes and validate automatically.
Autonomous agents generate fixes, open pull requests, and rescan code to confirm each issue is resolved.
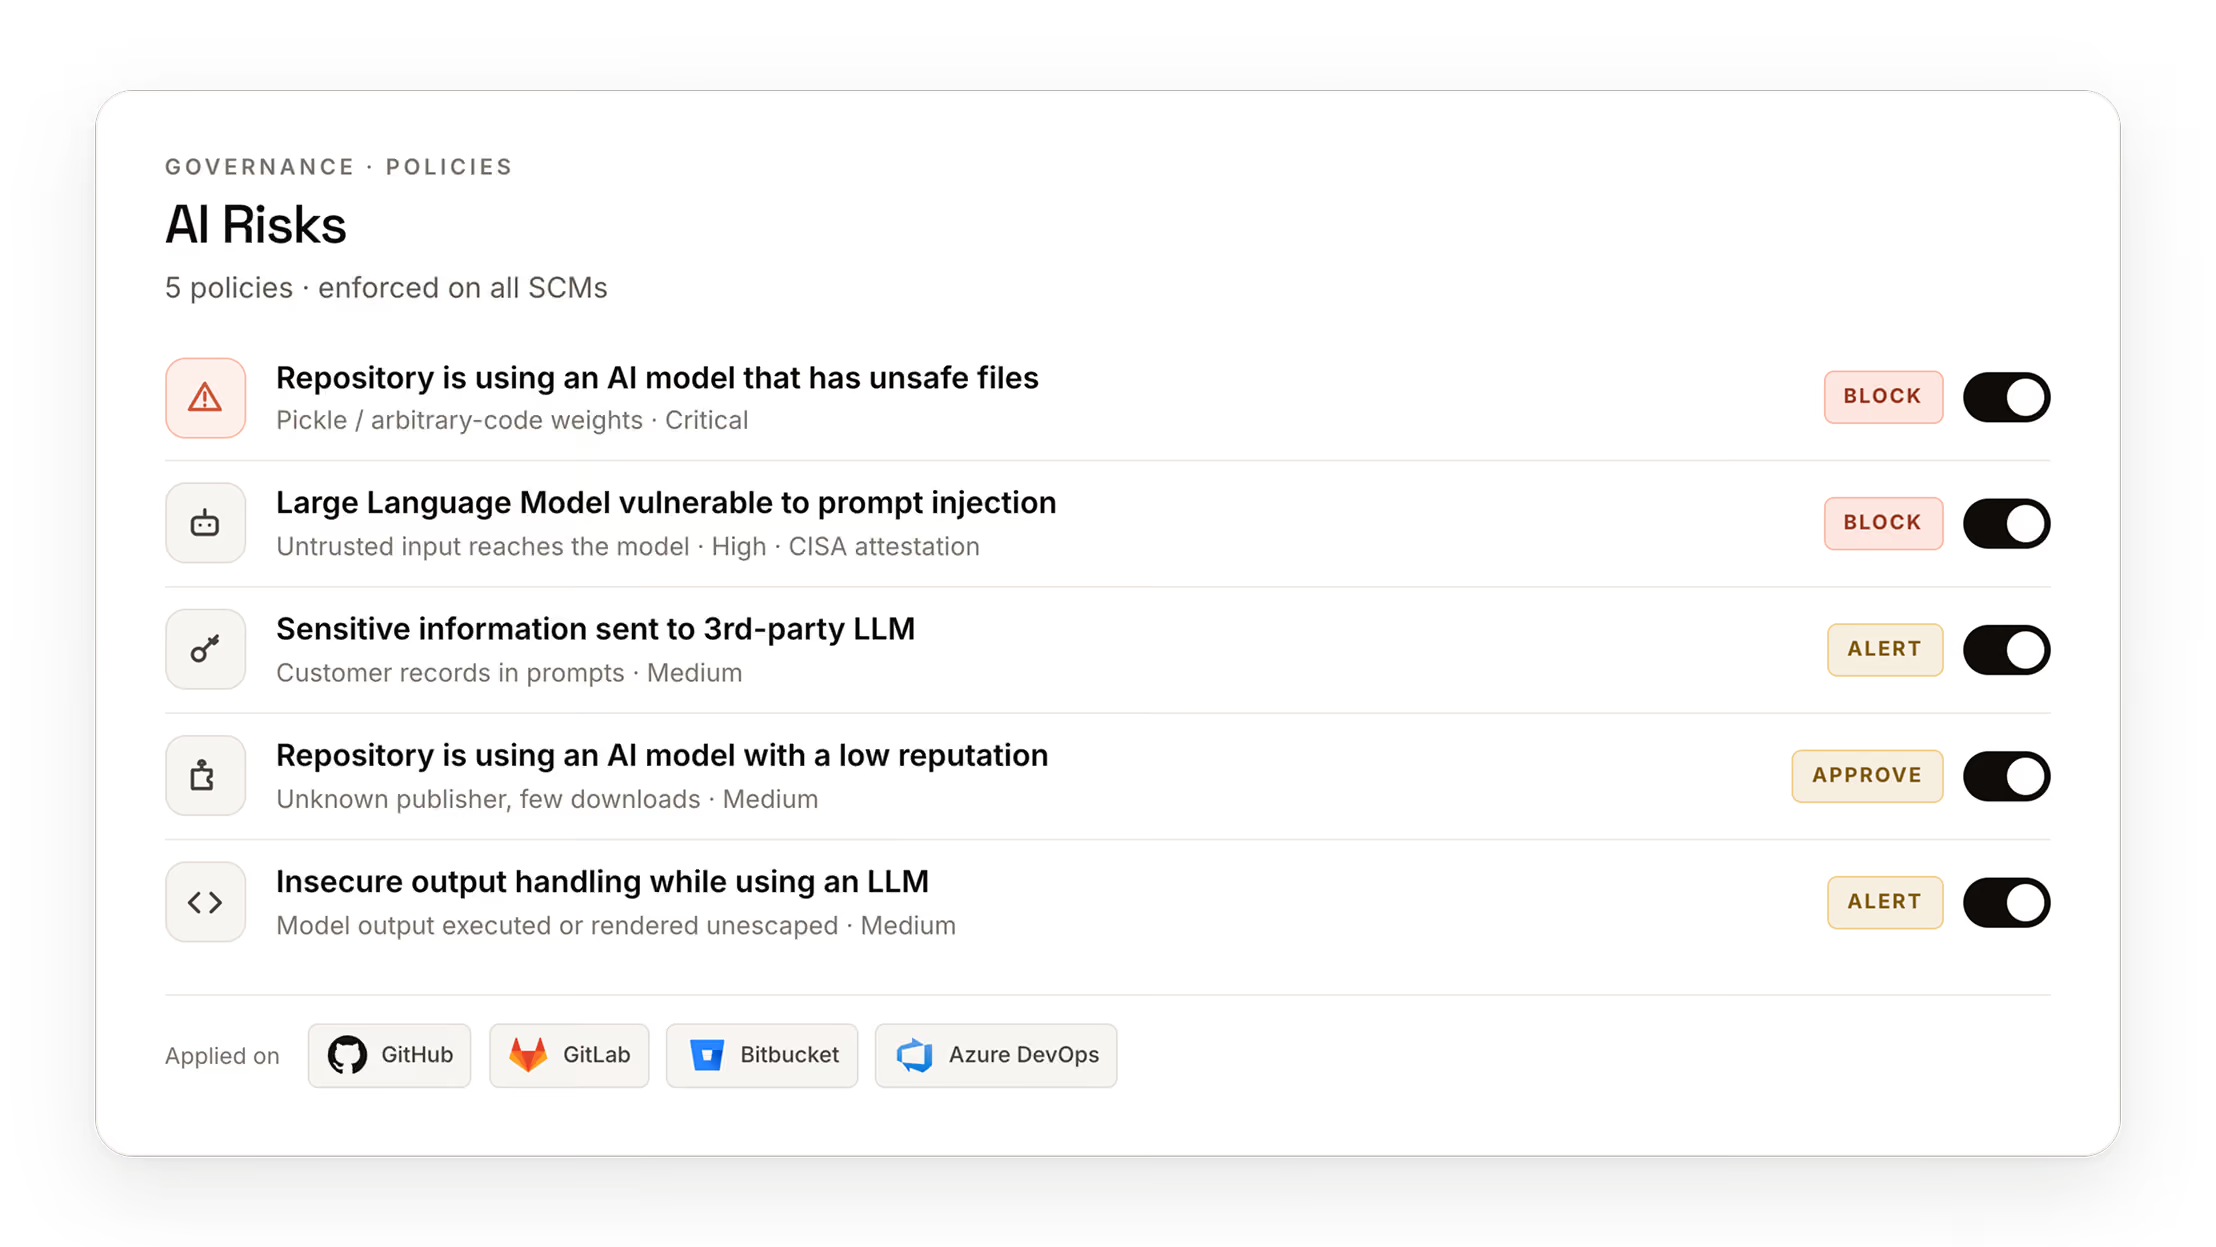
What changes with Legit
Prevent vulnerabilities earlier. Prioritize policyholder risk. Automate compliance.

Automated evidence generation replaces manual audit prep, mapping controls to NAIC, HIPAA, and GDPR as your environment changes.

AI-powered correlation reduces total vulnerability noise by more than 90%, so teams focus on regulated risk over alert volume.

Secrets scanning across code, pipelines, and artifacts cuts false positives by over 95%, protecting PHI and PII from exposure.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."
More insights for modern AppSec teams
Why I Joined Legit
We believe that security tools had become very good at identifying problems, but that developers were still left with the hardest part: understanding those findings and turning them into secure code changes.

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.