The new risk in game development

Attackers move at game speed.
Coordinated attacks target open-source dependencies, CI/CD pipelines, and AI coding assistants faster than legacy tools can keep pace.

More code, more attack surface.
AI-assisted development accelerates output across plug-ins, microservices, and third-party SDKs, faster than manual reviews can realistically cover.

Fragmented repos hide real risk.
Modern games span dozens of repositories and engines. Without unified visibility, it's hard to tell what actually threatens players or uptime.
Traditional AppSec wasn't built for live-service games.
Traditional AppSec
Finds issues after they ship
Floods teams with false positives
Can't cover fragmented repos
Adds friction to release cycles
Agentic

Stops issues before commit
Surfaces only genuine threats
Unifies visibility code to cloud
Fits existing developer workflows
Meet AgenticAppSec.
Legit brings prevention, context, and autonomous remediation into a single platform, so studios secure AI-driven development without losing release cadence.
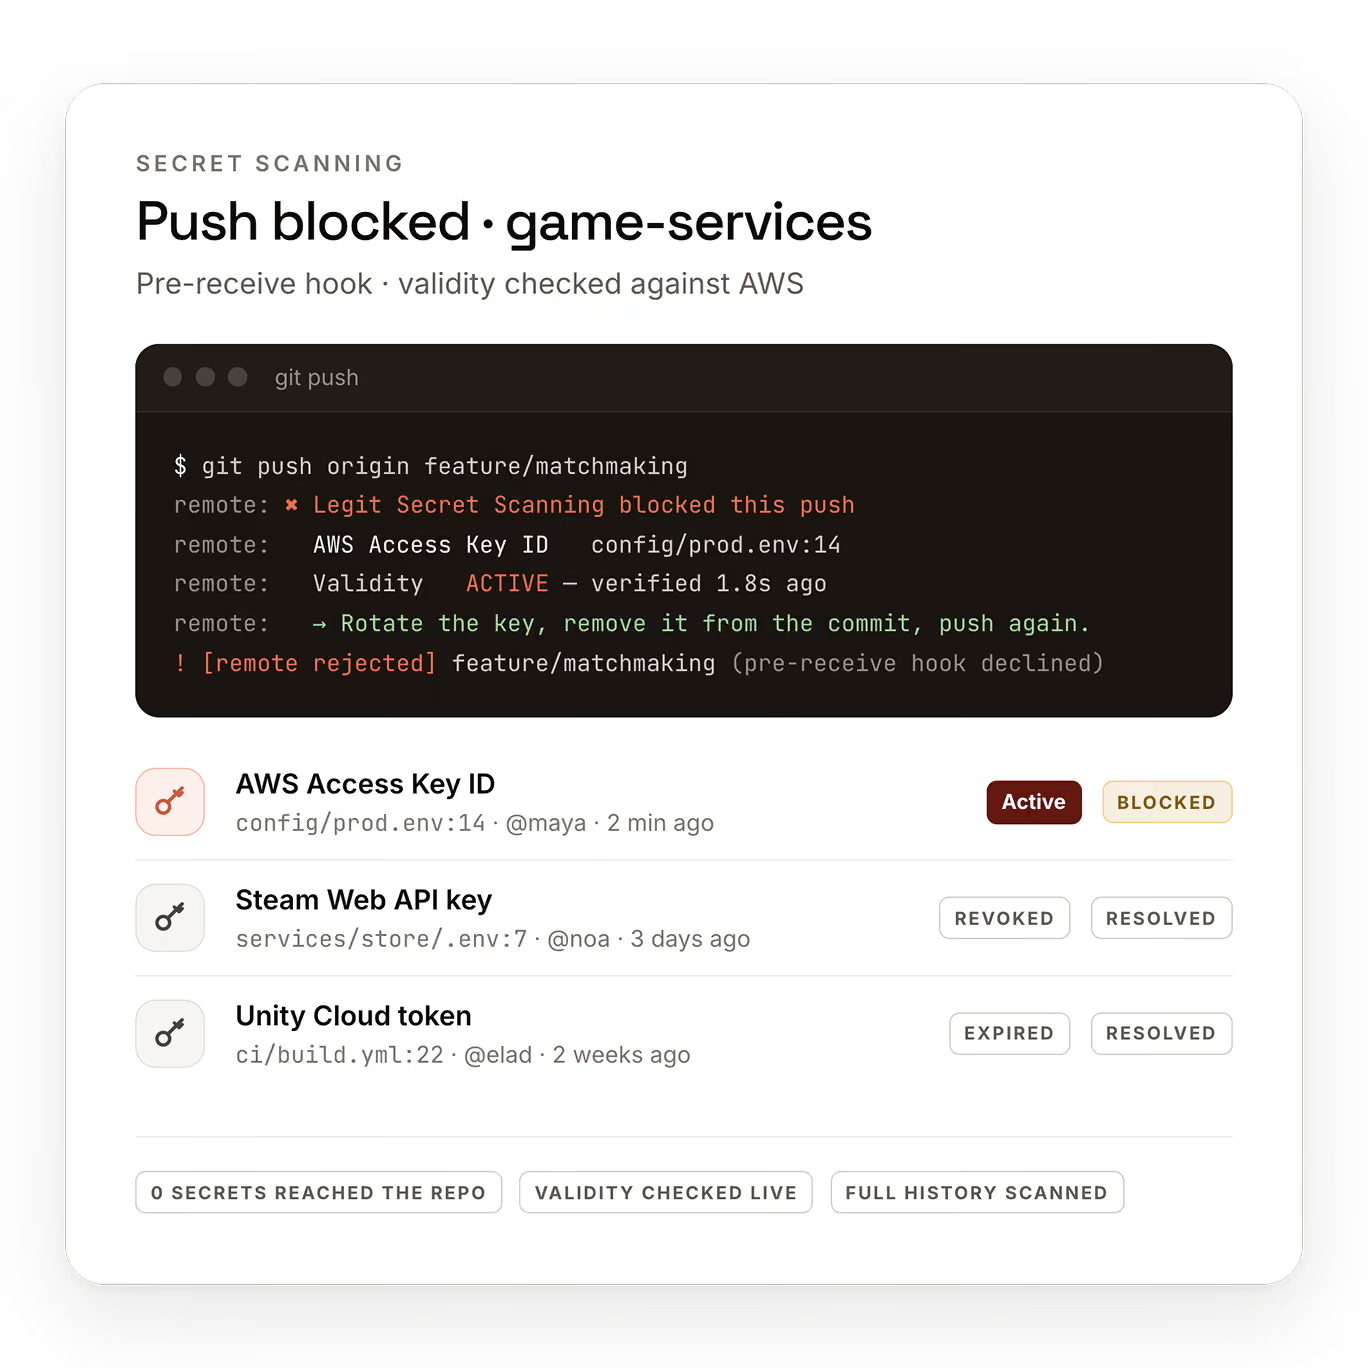
Stop vulnerabilities before they reach your repo.
Inject real-time guardrails into AI coding tools, catching risky code and exposed secrets before it ever reaches commit.
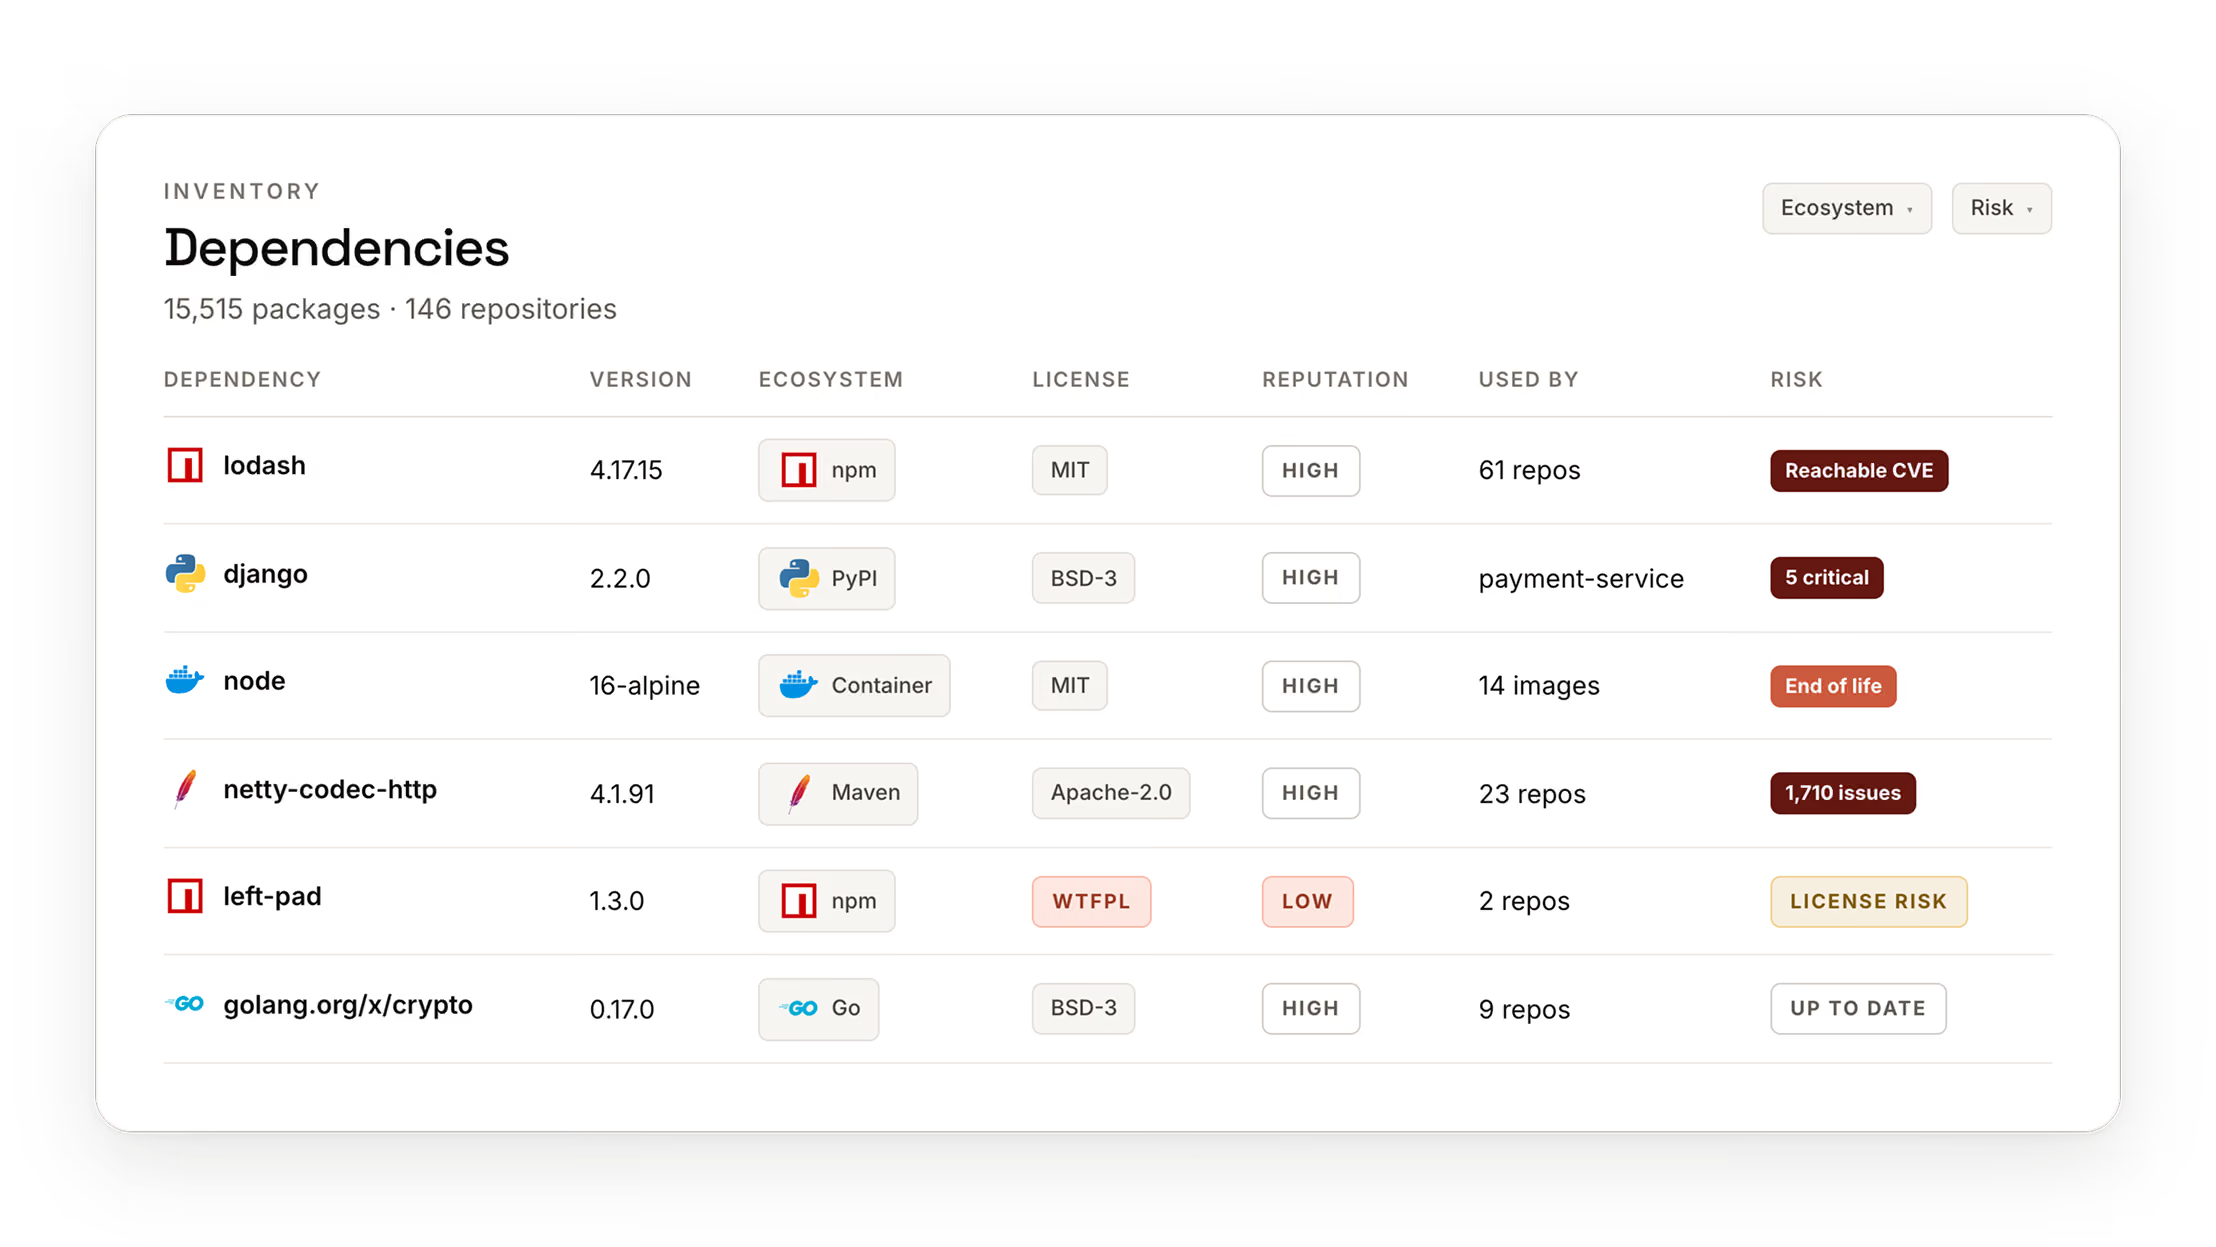
Focus on what threatens players and uptime.
Score every finding by exposure to player data, payment systems, and live-service uptime, not generic severity.
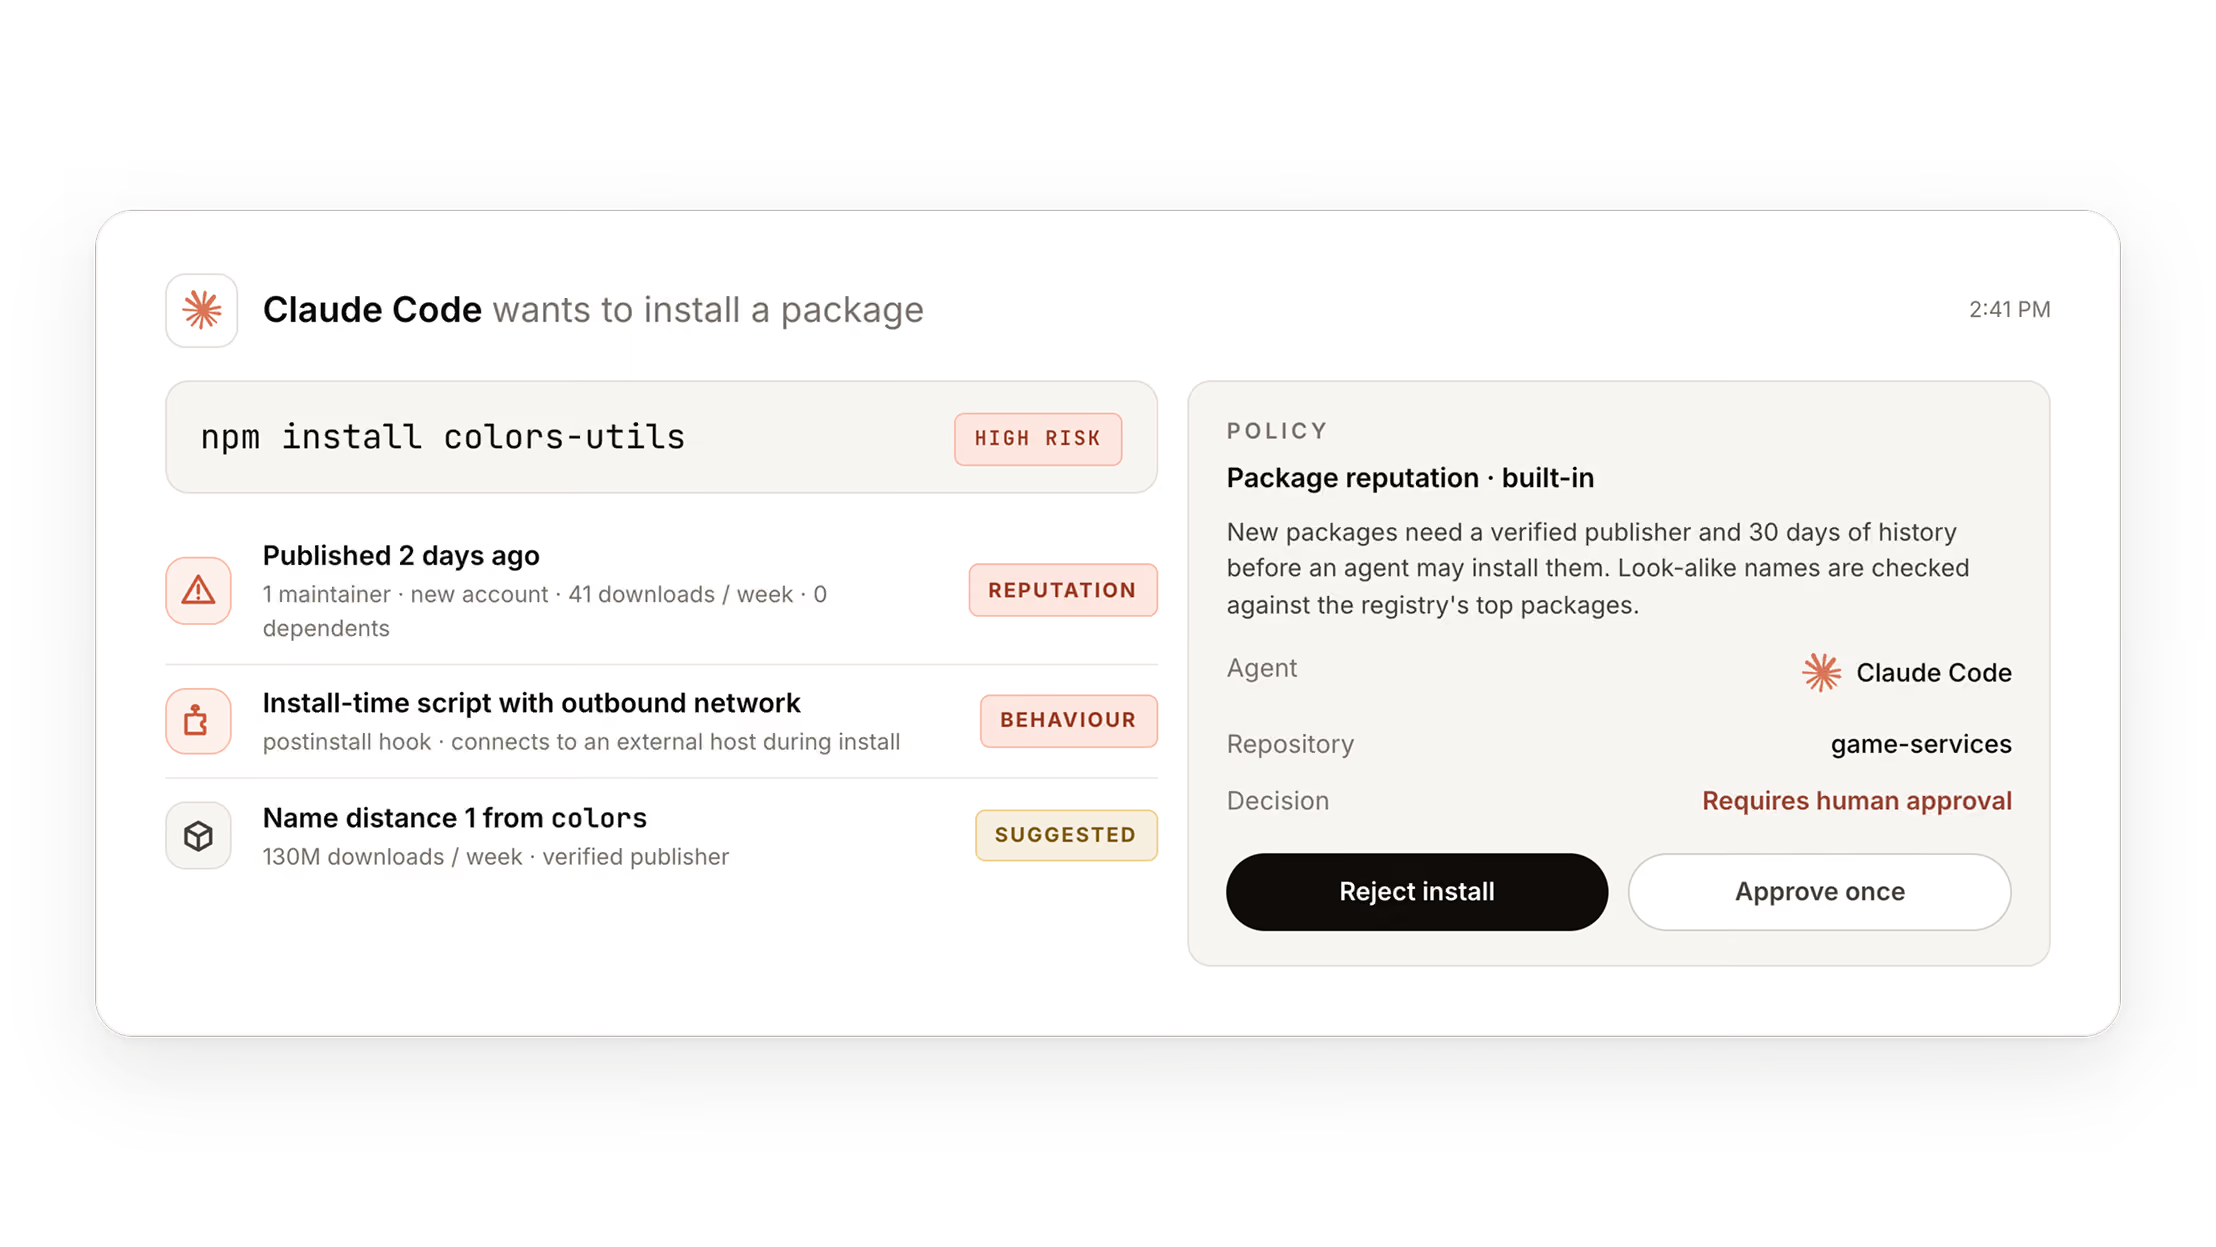
Fix root causes and validate automatically.
Autonomous agents generate fixes, open pull requests, and rescan every affected repository at once.
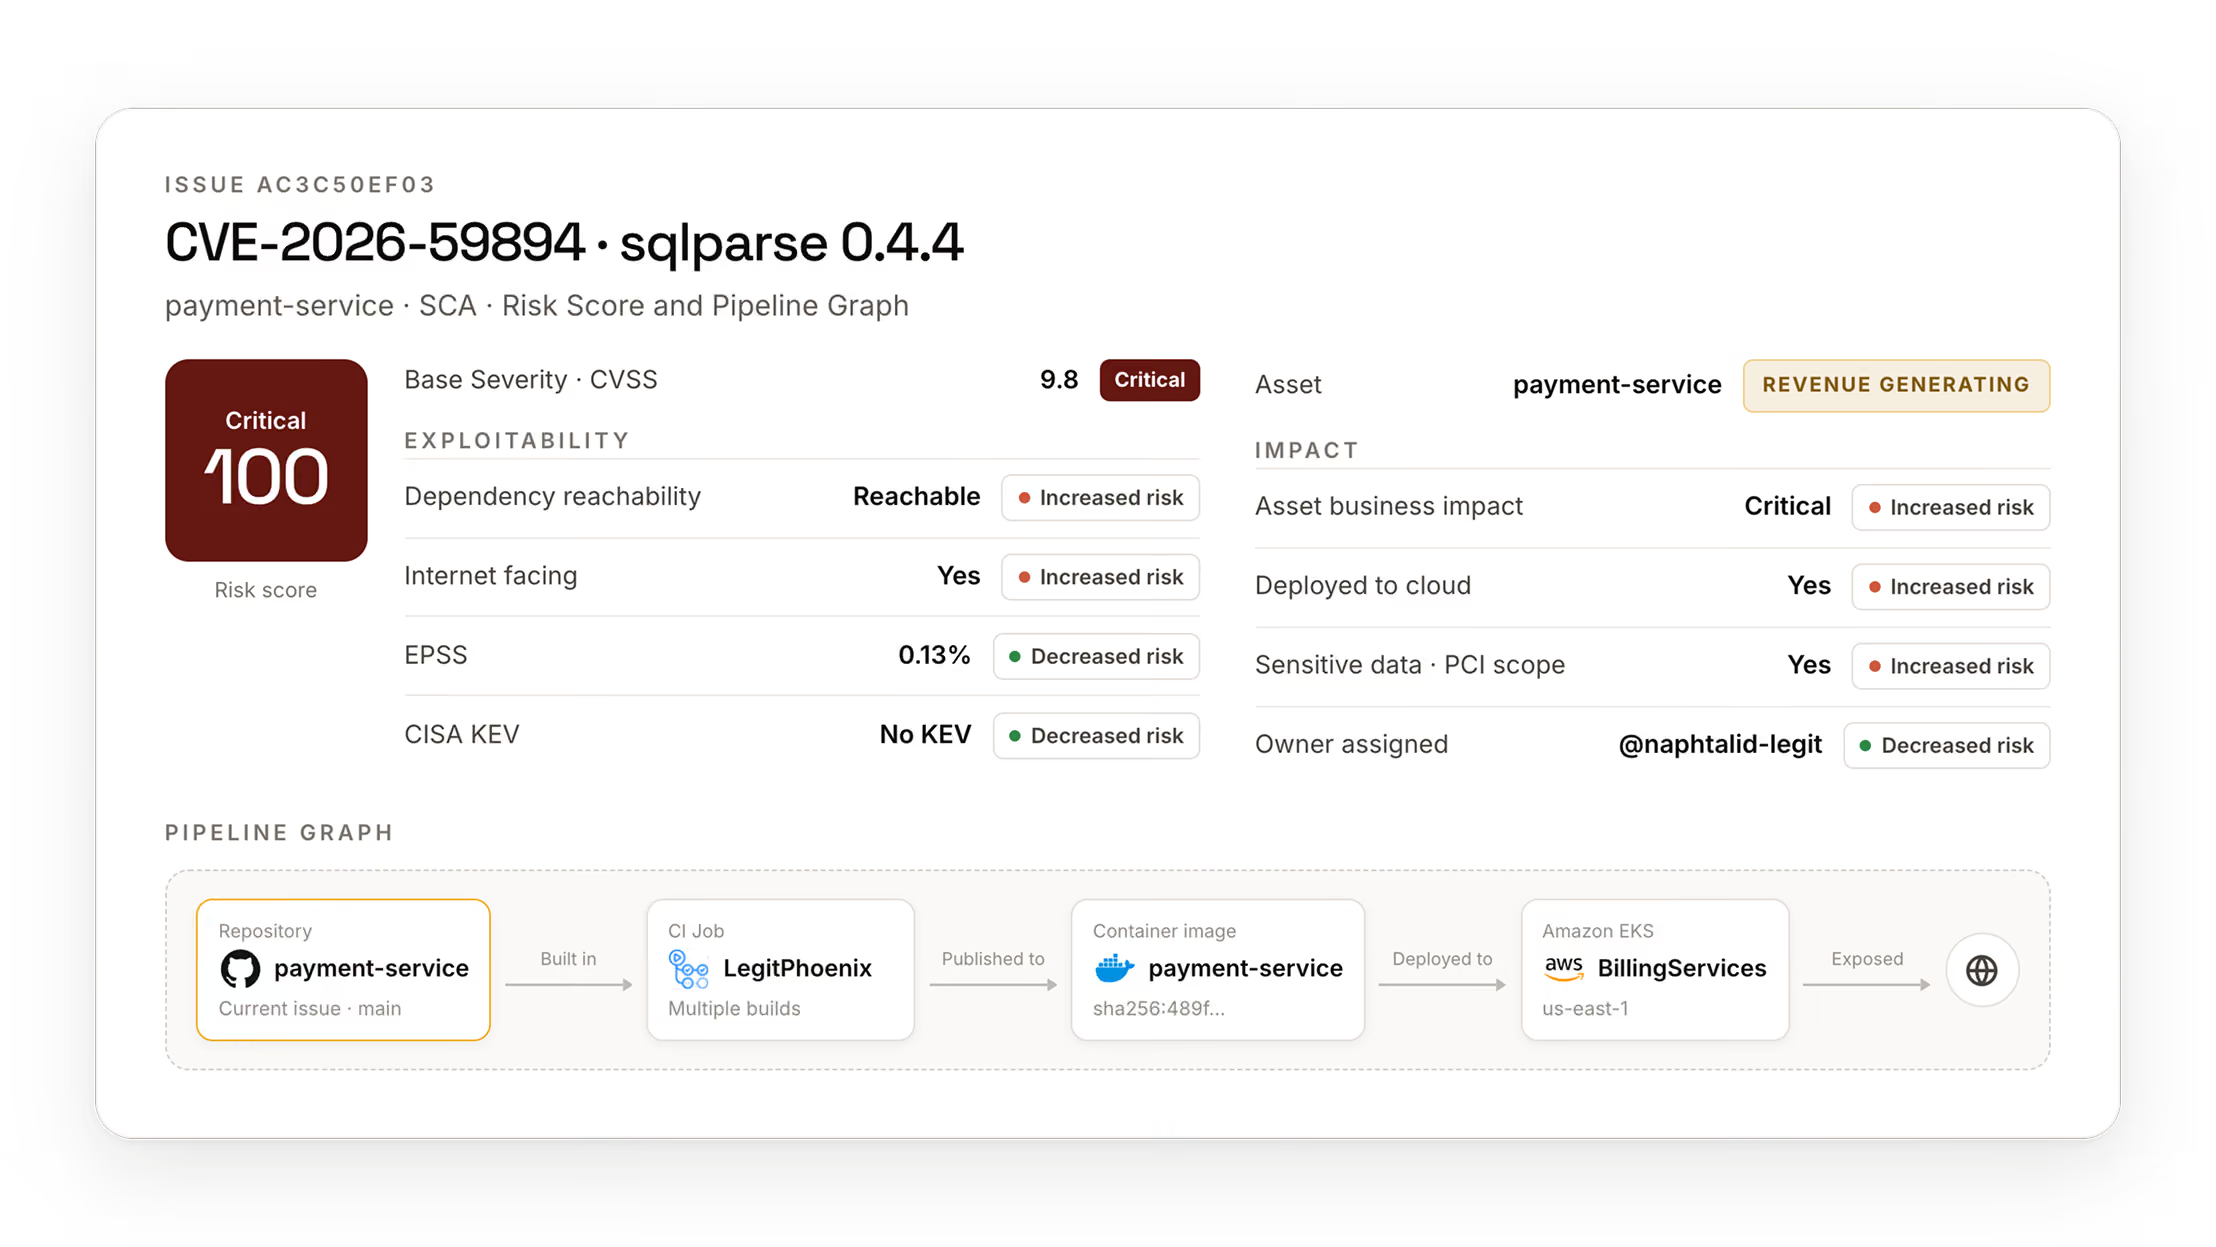
What changes with Legit
Prevent vulnerabilities earlier. Prioritize the risks that matter. Automate remediation.

Every remediation strengthens future AI-generated code, so your security program gets smarter with every release.

AI-powered correlation cuts total vulnerability noise by more than 90%, so teams keep shipping without slowing down.

Secrets scanning across code and collaboration tools cuts false positives by over 95%, protecting accounts and payment data.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."


More insights for modern AppSec teams

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
Agentic Remediation Just Got Bigger: Now Fixing Vulnerabilities in Your Dependencies, Not Just Your Code
Legit Security's Agentic Remediation now tackles vulnerabilities in dependencies, ensuring faster, verified fixes and enhancing AppSec in an AI-driven landscape.