Secure every link in your software supply chain.
Legit automatically discovers, correlates, and secures your entire software supply chain, from source code and CI/CD pipelines to open-source dependencies and third-party AI models, so nothing upstream goes unmonitored.
Your supply chain has more entry points than ever.
Open-source packages, CI/CD pipelines, containers, and now AI models and MCP servers all sit upstream of your code, and most teams have no consistent view across any of them.
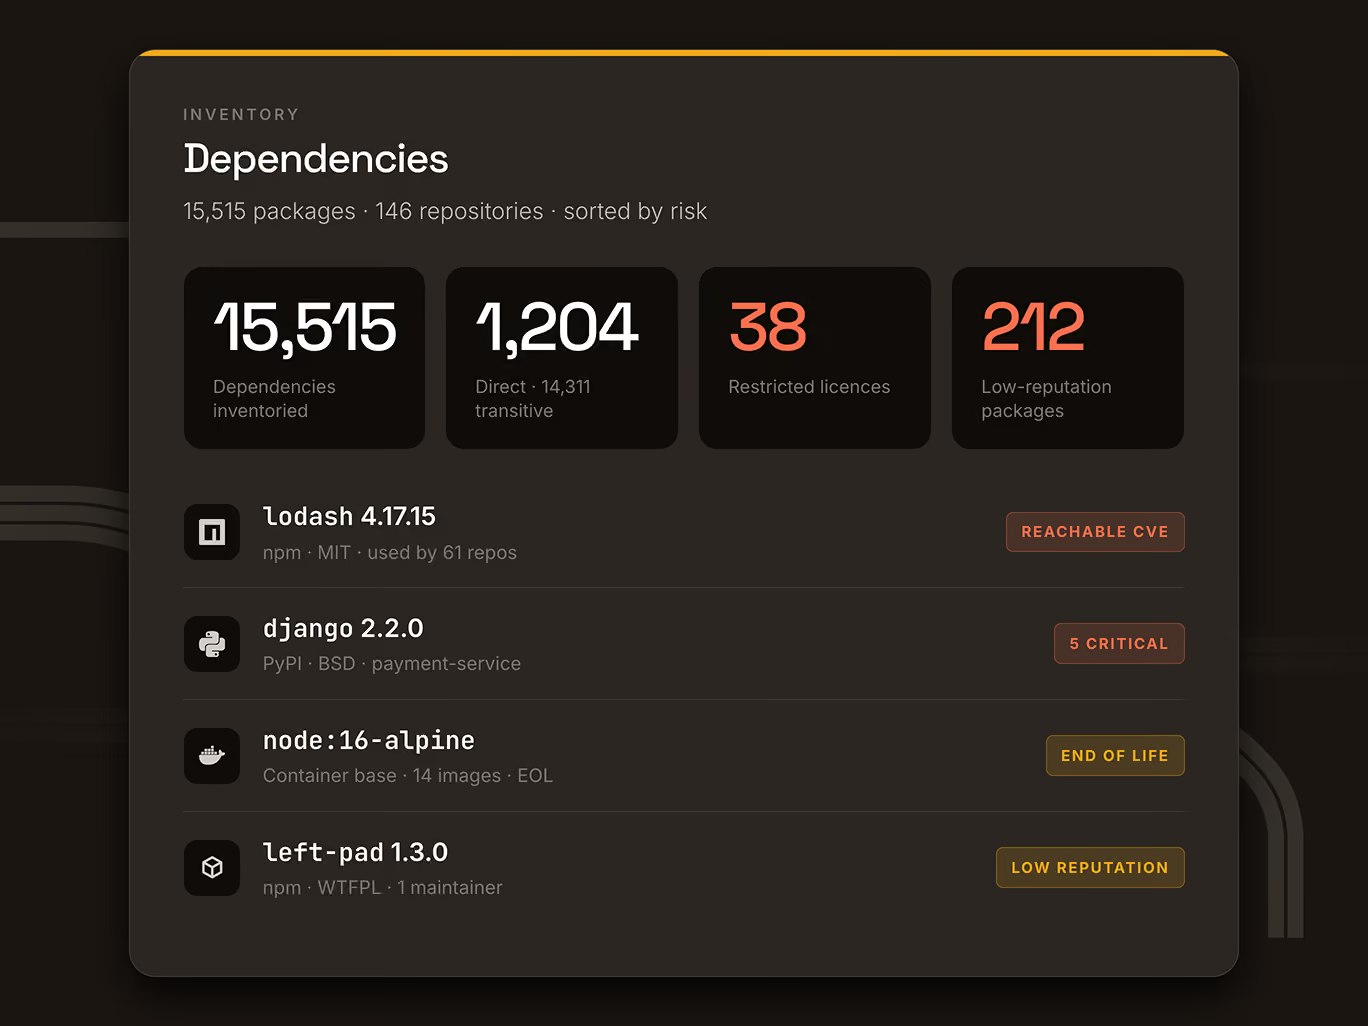
Legit maps your entire SDLC automatically, correlating code, pipelines, dependencies, and AI components into one real-time inventory, so you always know what’s connected and what’s exposed.
How Legit secures your
supply chain.
Point tools cover one piece of the supply chain at a time, leaving gaps between them. Legit discovers every asset and dependency, governs how third-party and AI components are used, then enforces the policies that keep pipelines and releases intact.
Discover

Prioritize
Automatically map source code, pipelines, dependencies, containers, and AI models across your entire SDLC, from code to cloud.
Govern

Act
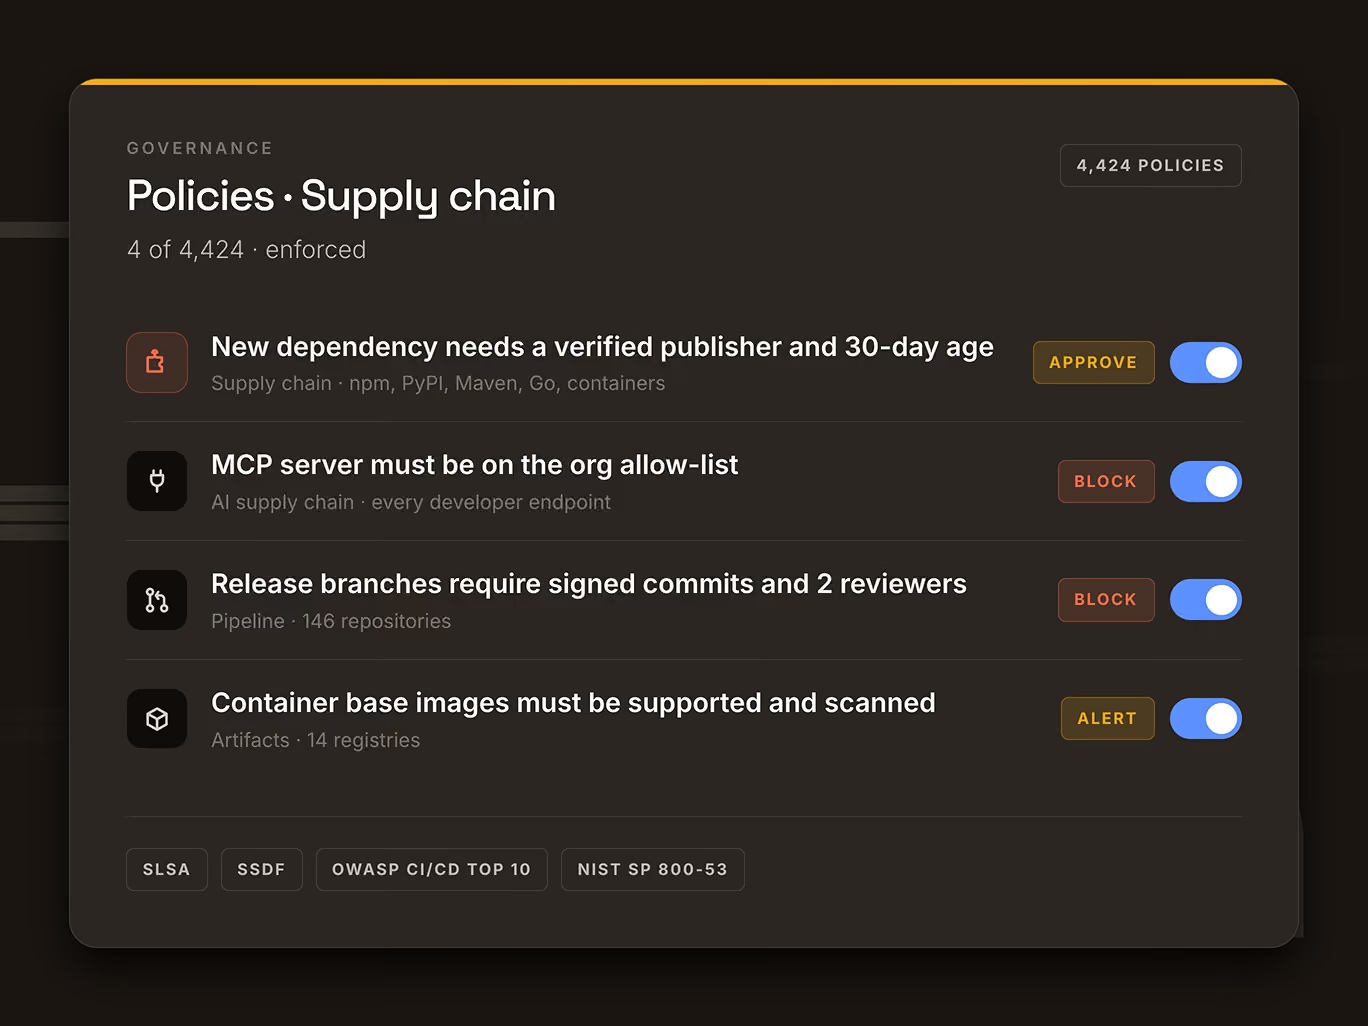
Apply consistent policy to third-party and open-source components, AI models, and MCP servers, with full SBOM life cycle management.
Enforce

Prevent
Continuously enforce security and integrity policies across pipelines, repositories, and releases to stop compromised software before it ships.
Everything security teams need to secure their supply chain.
Prevent vulnerabilities before they reach your repository.

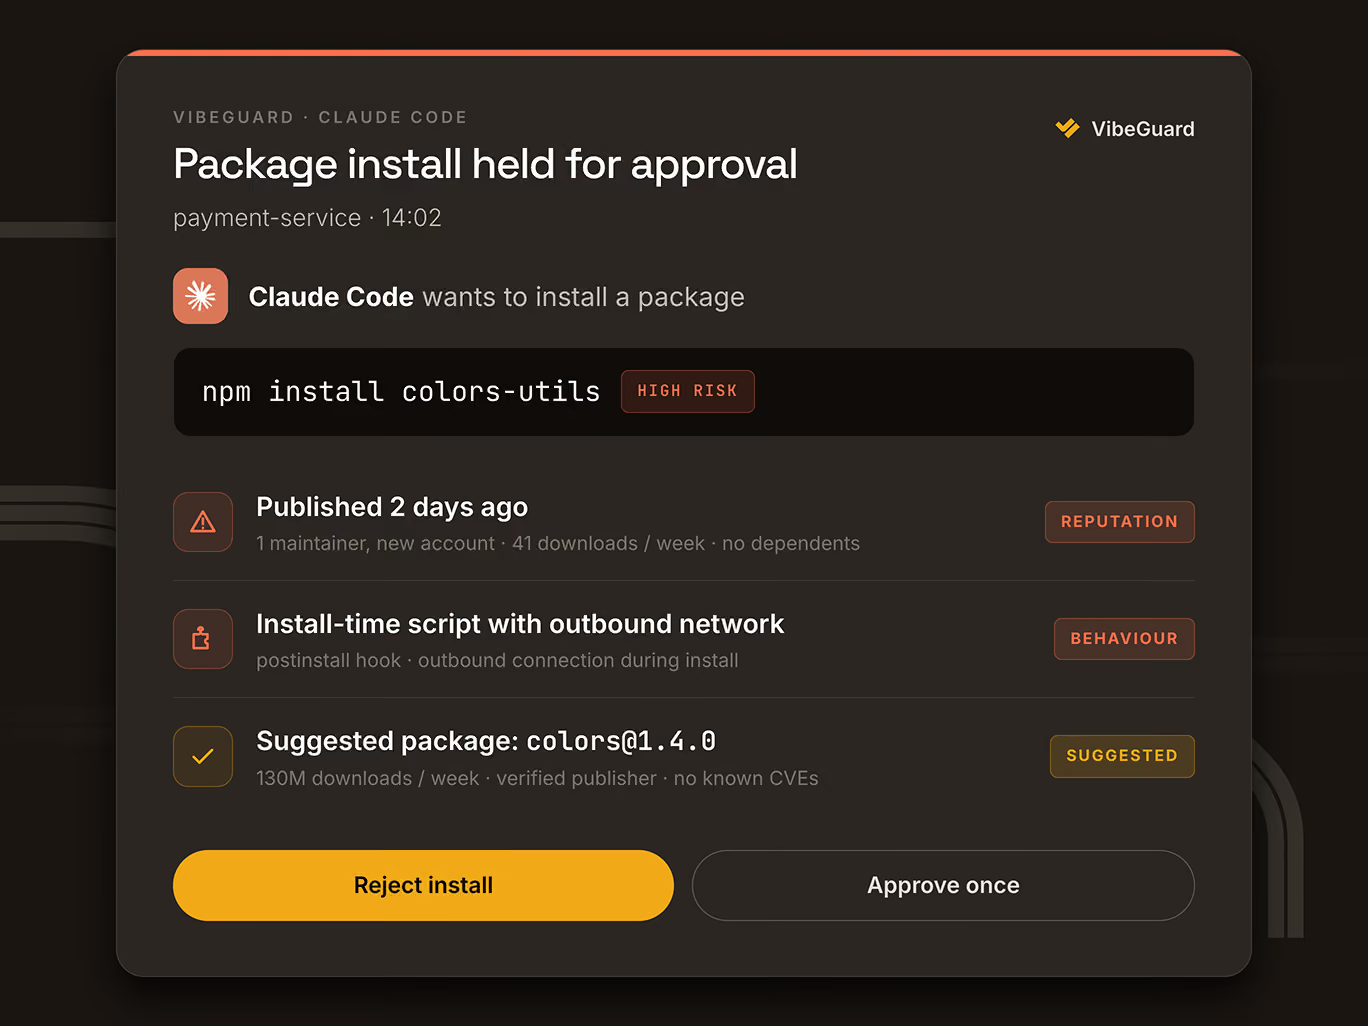
Always-on visibility across your applications and pipelines.
Fix what matters first — with AI.
Control how AI is used across development.
Not more alerts. Better ones.
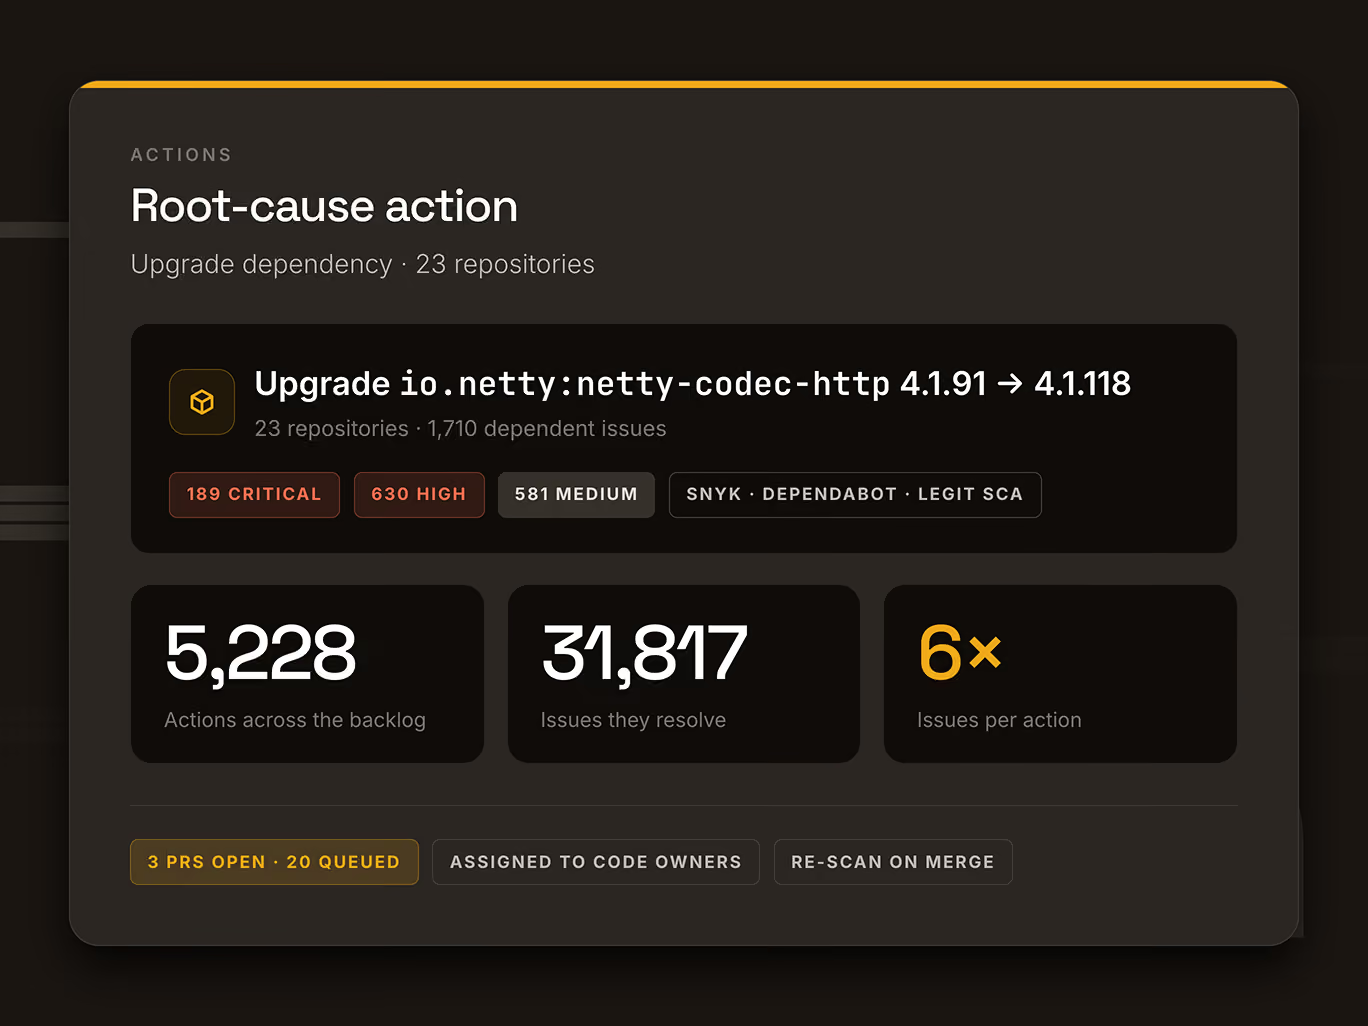
Most supply chain tools flag every dependency, secret, and pipeline finding the same way, leaving your team to sort through the noise. Legit correlates code, cloud, runtime, and business context to show which risks are actually reachable and which matter. The result is a prioritized view of real risk, not another list of alerts to chase.