Find what's exploitable. Fix it 10x faster.
Legit's native SAST, SCA, secrets, IaC, and CI/CD scanners cut through alert noise with reachability analysis and AI-aware detection, so teams fix what's actually exploitable.
AI changed what your codebase looks like. Your scanners didn't.
AI coding agents ship more code, more dependencies, and more infrastructure changes than any team can manually review. Legacy scanners just add more findings to an already unmanageable backlog.
Legit correlates, deduplicates and prioritizes every finding with reachability, exploitability, and business context, so security teams triage a short list of what's real instead of a long list of what's possible.
One platform, five native scanners, no blind spots.
Legacy AppSec stitches together point tools that scan in isolation and dump findings into a queue. Legit runs SAST, SCA, secrets, IaC, and pipeline scanning natively, then prioritizes and fixes what matters through one connected workflow.
Detect

Prioritize
Native scanners cover code, dependencies, secrets, infrastructure, and the CI/CD pipeline itself, with detection built for AI-generated code.
Prioritize

Act
Reachability analysis and business context cut through alert noise, so teams triage exploitable risk instead of theoretical findings.
Fix

Prevent
Root cause analysis clears related findings in one fix, and autonomous agents generate validated pull requests to close the loop.
Everything a security team needs to secure code,
dependencies, and pipelines.
Detection built for first-party and AI-generated code.

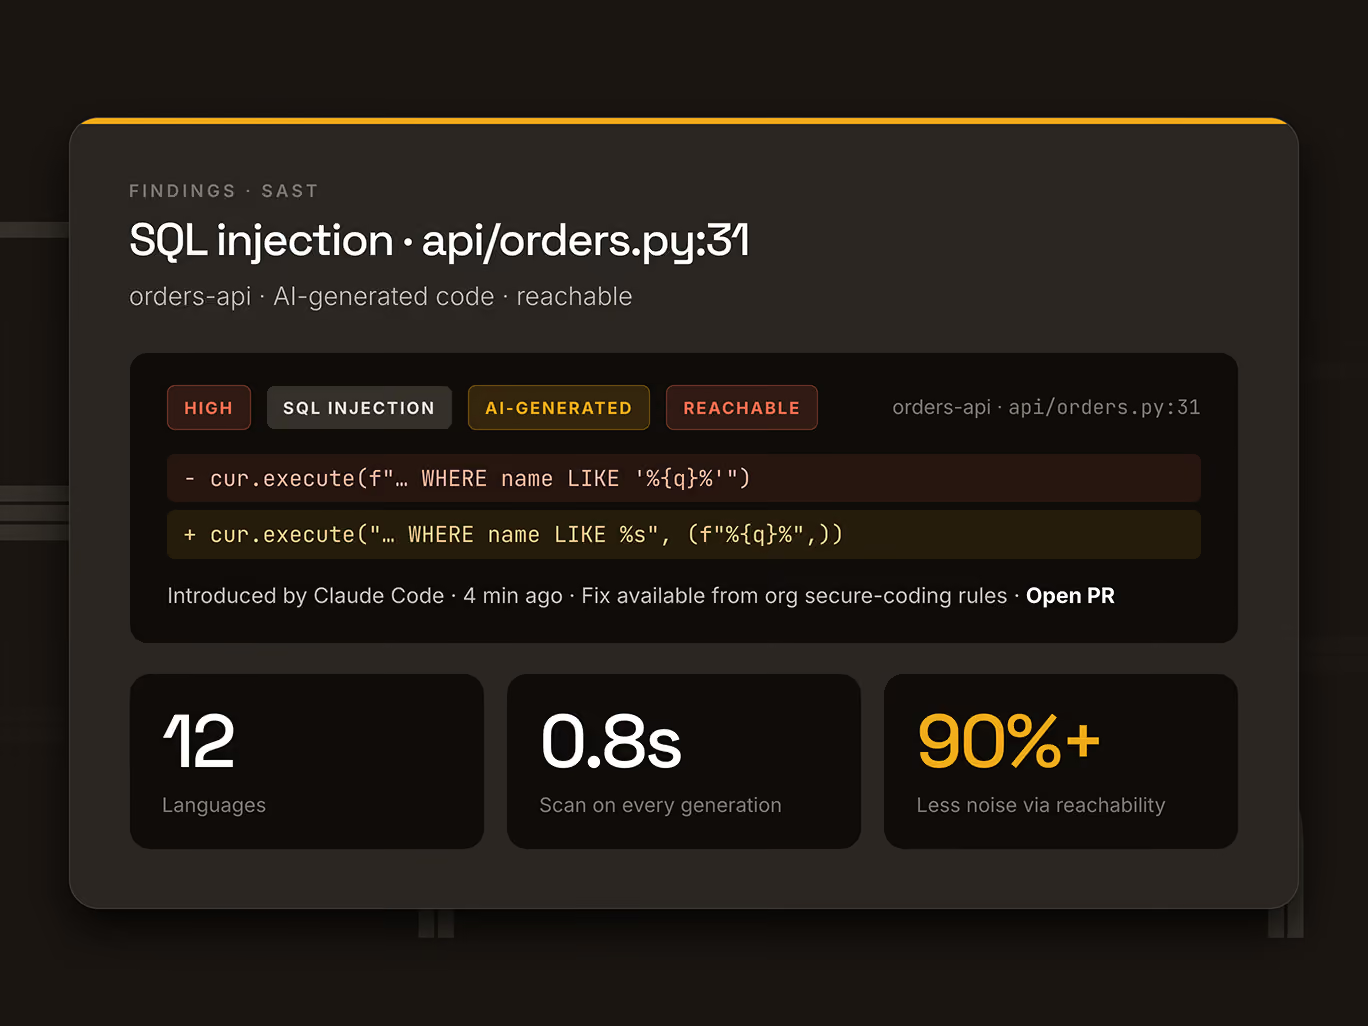
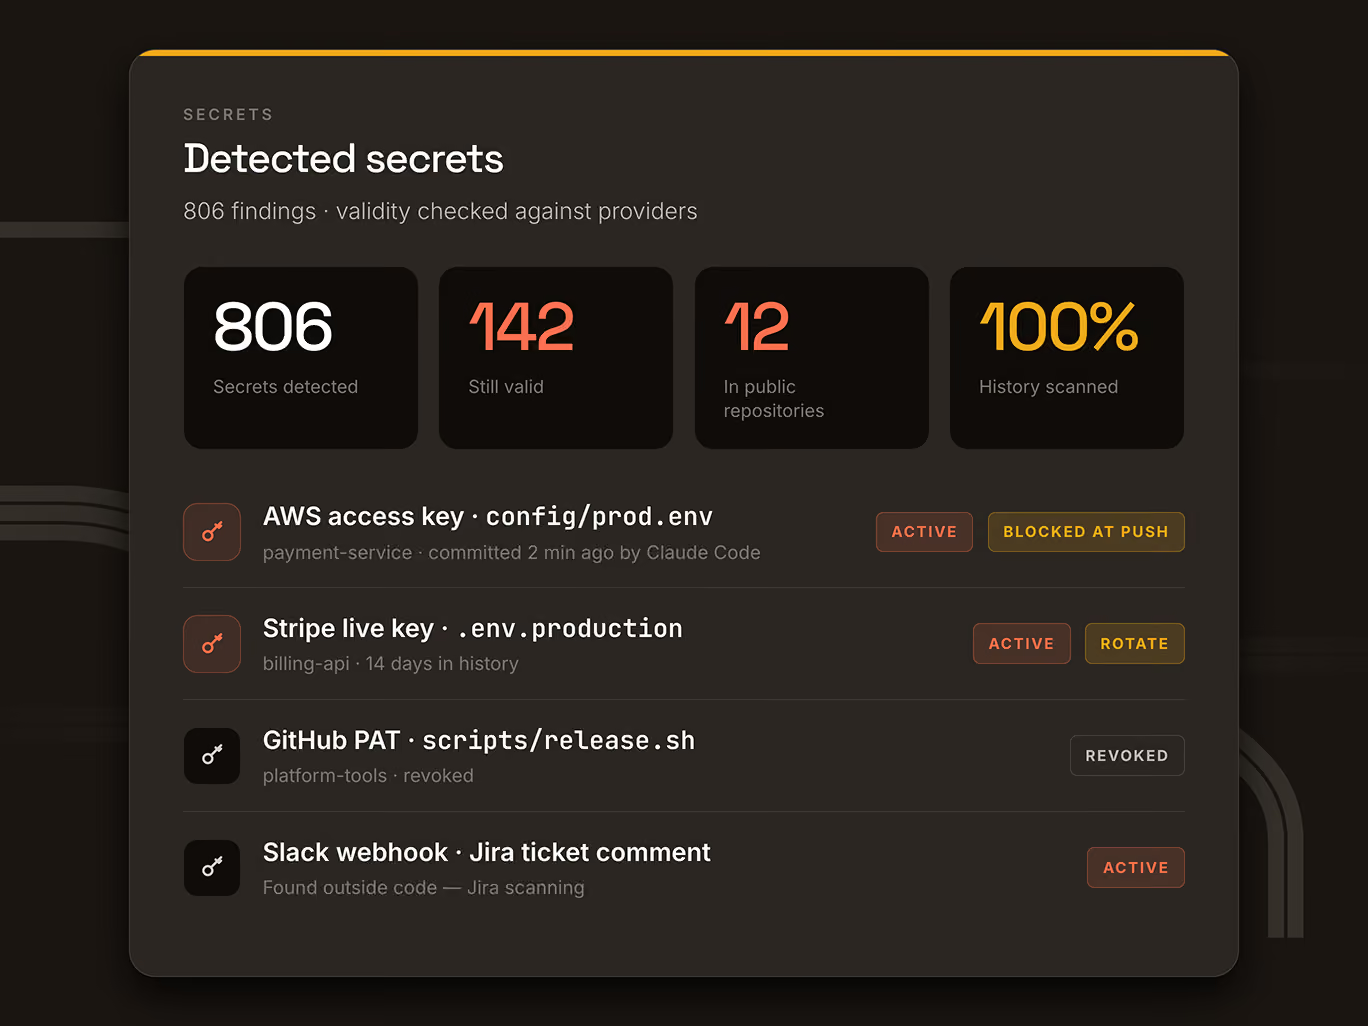
Catch secrets before they ever reach a public repo.
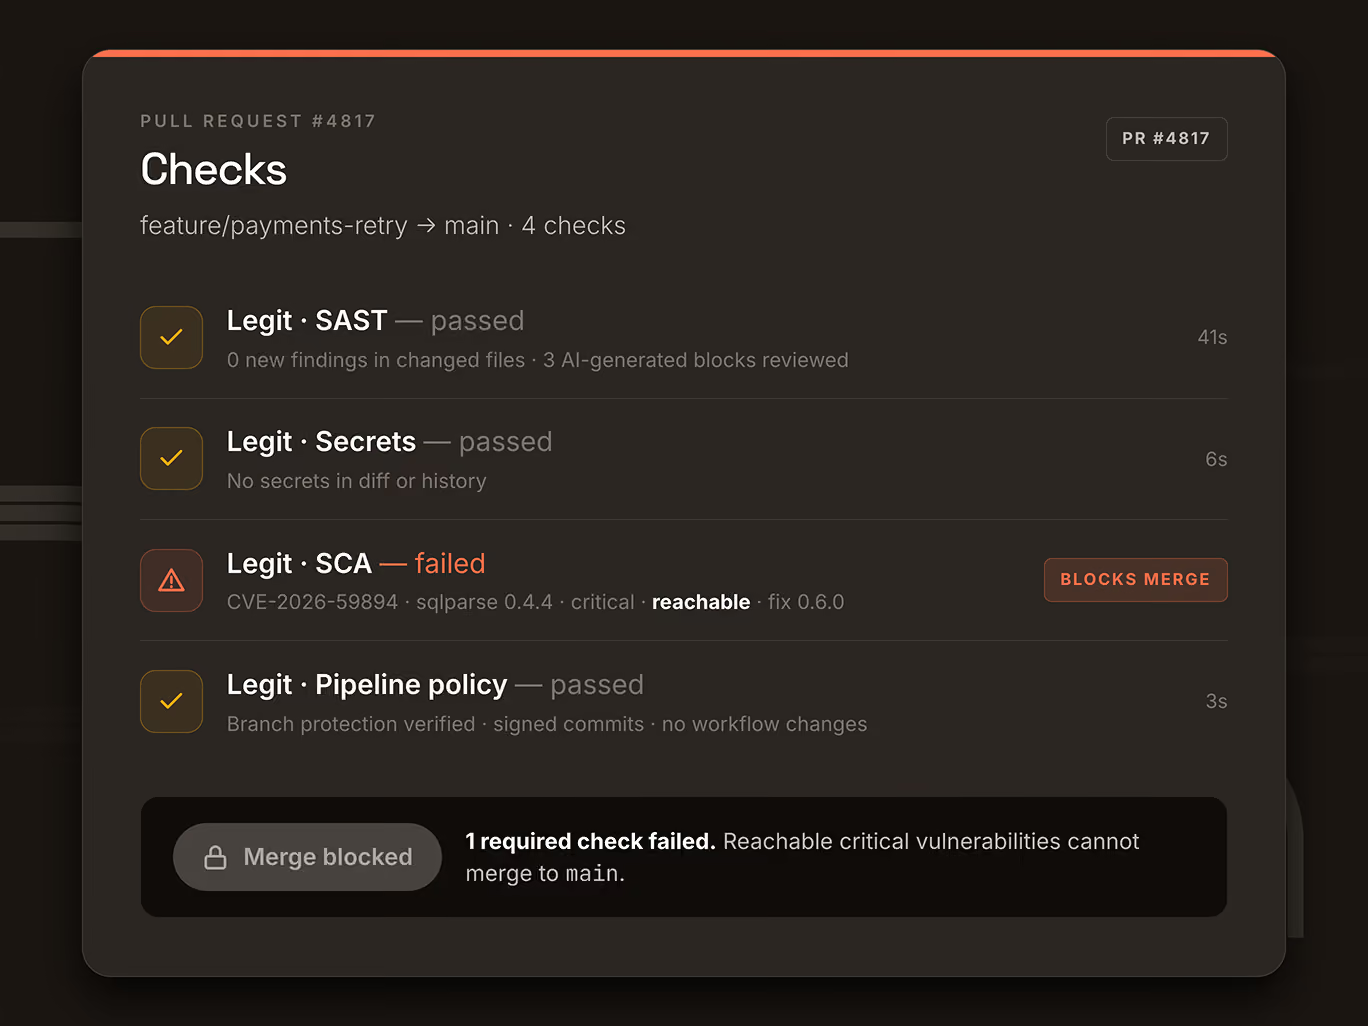
Security built into the build, not bolted on after.
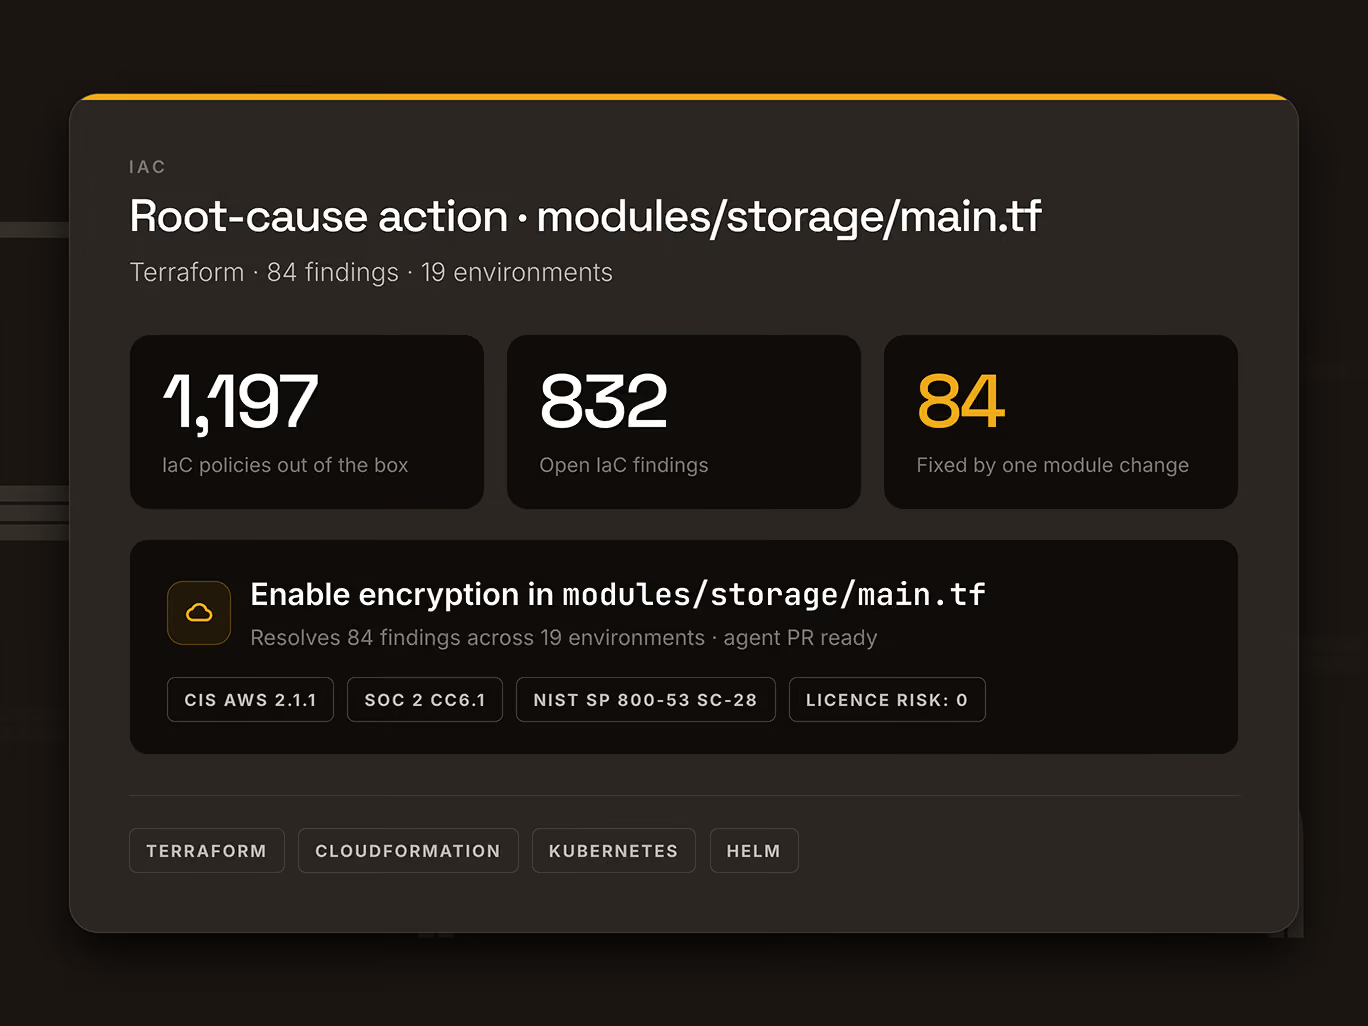
Infrastructure scanned, backlogs cleared in one fix.
Context changes everything.
Legit correlates code, cloud, runtime, and business context to understand what actually matters. Instead of treating every finding the same, the platform prioritizes risk based on real-world reachability, exploitability, and business impact so teams spend less time chasing alerts.