Slack logo
Chat on Slack

Security that keeps up with AI-driven development.

Legit's Agentic AppSec platform prevents vulnerabilities before they're introduced, gives security teams visibility into AI-driven development, and autonomously prioritizes and remediates risk - without slowing innovation.
A lock icon in a blue circle
A checkmark in a purple circle

AI changed how software is built.
AppSec has to change too.

AI coding agents accelerate development faster than traditional AppSec can keep up. More code is generated, more changes are shipped, and more risk is introduced before security ever gets involved.
‍
Finding vulnerabilities after commit isn’t enough. Security teams need to prevent issues and generate secure code before anything enters the codebase, understand what matters most, and enable innovation without slowing it down.

A fundamentally different AppSec architecture.

Traditional AppSec tools find and fix vulnerabilities after they’re introduced. Agentic AppSec prevents them, prioritizes them with context, and remediates them autonomously through a unified platform built to help security teams stay ahead of AI-driven development.

Prioritize

A yellow shield icon

Prioritize

Correlate code, cloud, runtime, and business context to cut through alert noise and identify the risks that need immediate attention.

Act

Act

Autonomous agents generate fixes, create pull requests, validate changes, and continuously improve over time, helping teams resolve critical risks faster without adding manual effort.

Prevent

Prevent

Secure AI-generated code in real time with policy enforcement, AI guardrails, and native scanning integrated directly into AI coding workflows.

Everything security teams need to secure AI-driven development.

Generate Secure Code

Prevent vulnerabilities before they reach your repository.

A checkmark in a yellow circle
Secure AI code generation
A checkmark in a yellow circle
Real-time SAST/SCA
A checkmark in a yellow circle
AI guardrails
A checkmark in a yellow circle
IDE & agent integrations
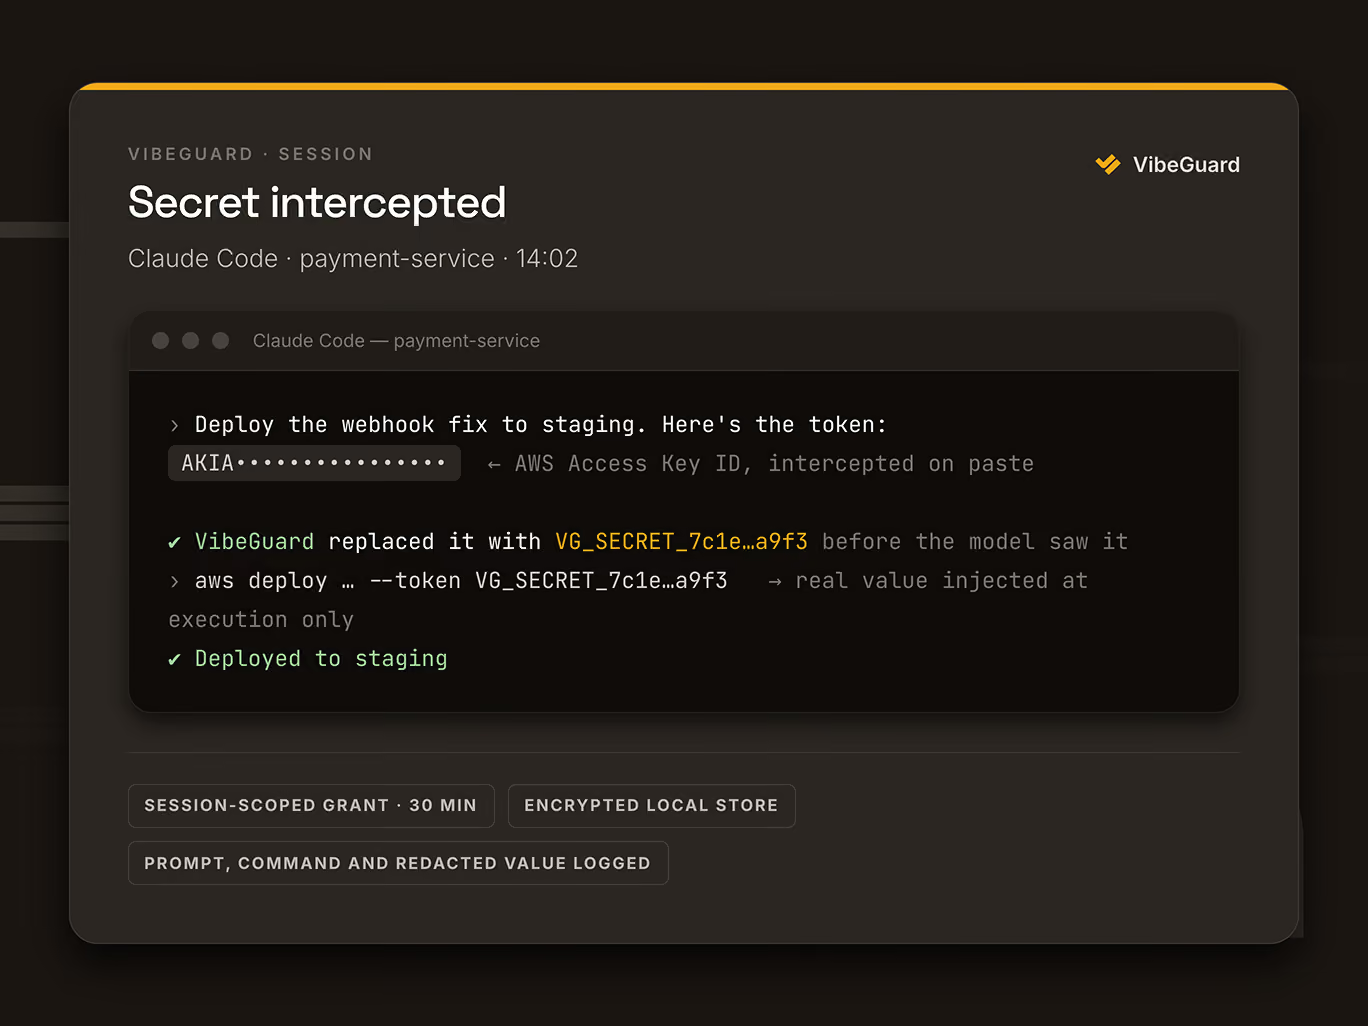
Dark mode user interface titled 'Secret intercepted' from VibeGuard showing a payment-service session log where an AWS Access Key ID token is intercepted and replaced securely with VG_SECRET before deployment to staging, indicating encrypted local storage and session-scoped grant for 30 minutes with prompt, command, and redacted value logged.
Detect Risk

Always-on visibility across your applications and pipelines.
A checkmark in a yellow circle
Native scanning
A checkmark in a yellow circle
Secrets, SAST, SCA, IaC
A checkmark in a yellow circle
CI/CD protection
A checkmark in a yellow circle
Continuous monitoring
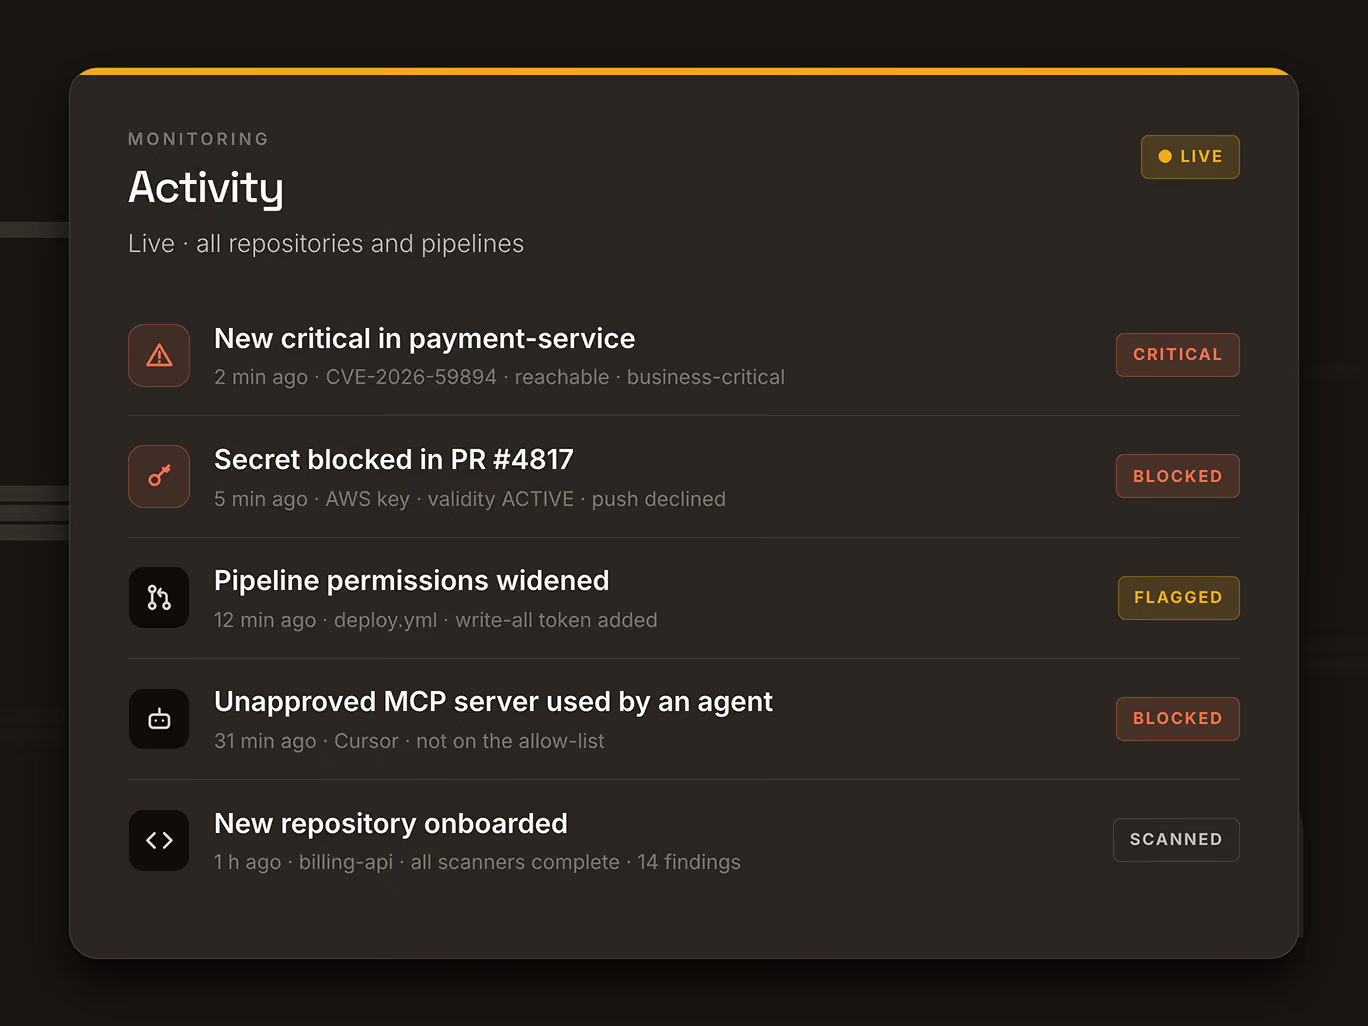
Software monitoring dashboard showing live activity for repositories and pipelines with alerts including new critical issue in payment-service labeled critical, secret blocked in PR #4817 labeled blocked, pipeline permissions widened labeled flagged, unapproved MCP server used by an agent labeled blocked, and a new repository onboarded labeled scanned.
Prioritize & Remediate

Fix what matters first — with AI.

A checkmark in a yellow circle
Context-driven prioritization
A checkmark in a yellow circle
Automated fixes
A checkmark in a yellow circle
PR generation
A checkmark in a yellow circle
Validation & rescanning
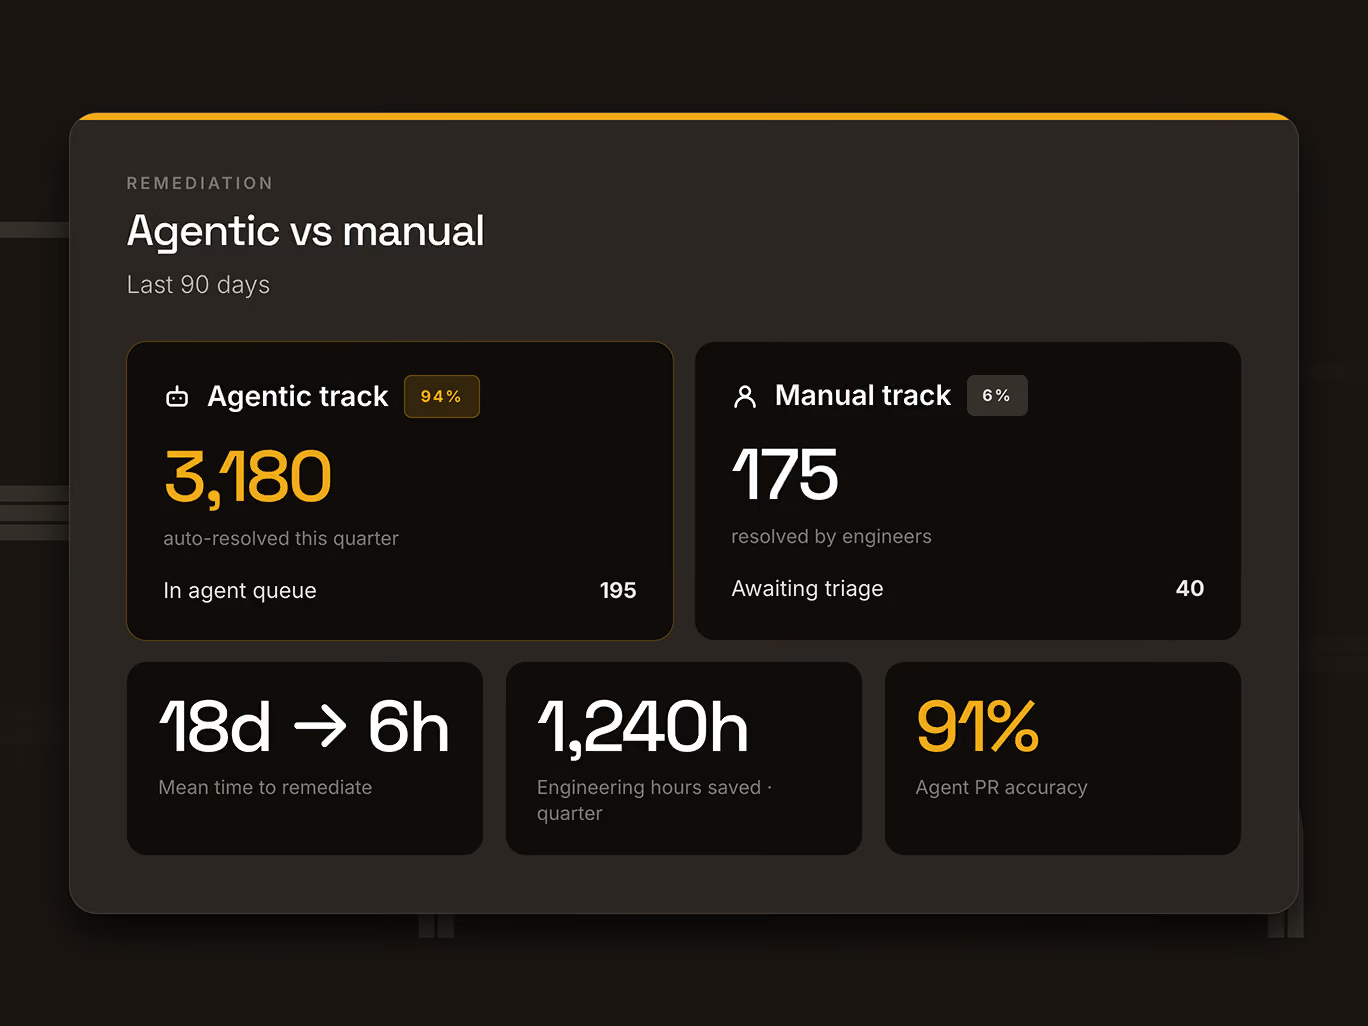
Dashboard comparing Agentic vs manual remediation over the last 90 days showing 3,180 issues auto-resolved by Agentic track with 195 in agent queue, and 175 issues resolved manually by engineers with 40 awaiting triage, mean time to remediate reduced from 18 days to 6 hours, 1,240 engineering hours saved this quarter, and 91% Agent PR accuracy.
Govern AI & Supply Chain

Control how AI is used across development.
A checkmark in a yellow circle
AI discovery
A checkmark in a yellow circle
Policy enforcement
A checkmark in a yellow circle
Supply chain security
A checkmark in a yellow circle
AI Advisory
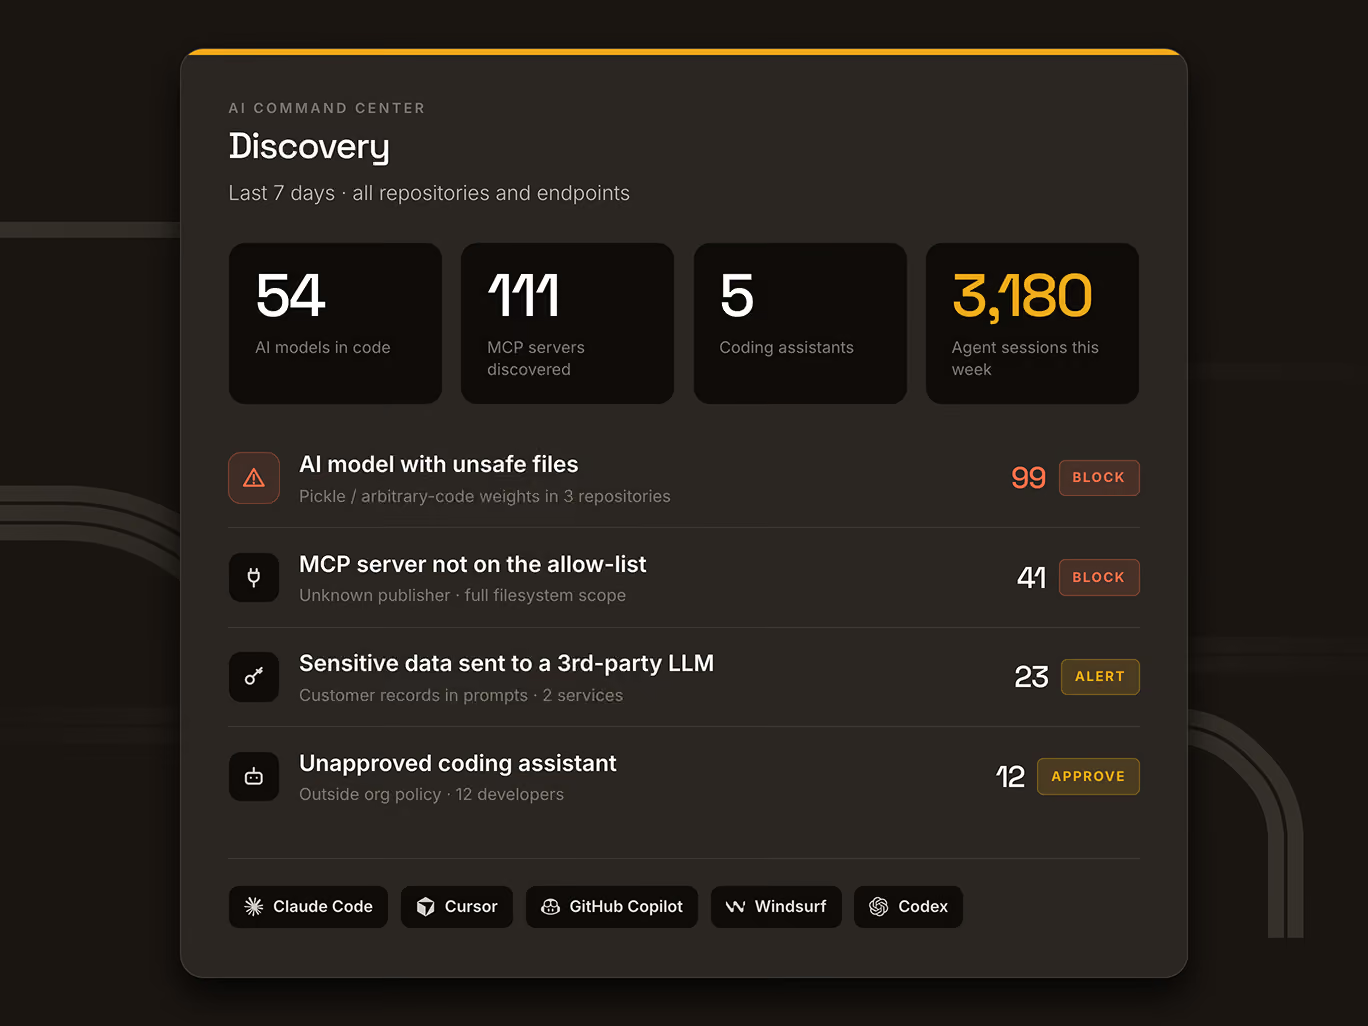
AI Command Center Discovery dashboard showing data from the last 7 days across all repositories and endpoints: 54 AI models in code, 111 MCP servers discovered, 5 coding assistants, and 3,180 agent sessions this week. Alerts include 99 instances of AI model with unsafe files marked to block, 41 MCP servers not on the allow-list also marked to block, 23 sensitive data sent to a third-party LLM with alert status, and 12 unapproved coding assistants recommended for approval. Buttons at bottom show integrations like Claude Code, Cursor, GitHub Copilot, Windsurf, and Codex.

Context changes everything.

Legit correlates code, cloud, runtime, and business context to understand what actually matters. Instead of treating every finding the same, the platform prioritizes risk based on real-world exposure, exploitability, and business impact. Security teams spend less time chasing alerts and more time addressing what matters most.
90%+
reduction in vulnerability noise
95%+
reduction in false positives for secret scanning

Built for your existing security ecosystem.

See All Integrations
GitHub logo
GitLab logo
Snyk logo
Wiz logo
Checkmarx logo
Jira logo
Slack logo
Bitbucket logo
Claude logo
VibeGuard vibe check illustration

See Agentic AppSec in action

From detect to fixed, automatically, closing the gap before attackers exploit it.