Legit Security vs Cycode Comparison.
Compare Legit Security vs. Cycode in a detailed side-by-side analysis and discover why Legit stands out as the top ASPM solution for your business.
How Do Cycode and Legit Security Compare?
Prevent vulnerabilities earlier. Prioritize the risks that matter. Automate remediation.

Legit offers discovery and a visual graph of SDLC build assets for full visibility into pipeline and code-to-production paths; Cycode does not.

Cycode doesn't map controls to compliance frameworks; Legit aligns with PCI-DSS, ISO 27001, NIST 800-53, FedRAMP, SLSA, and OWASP standards.

Legit inventories and identifies risk in GenAI, LLM, and MLOps usage across your codebase, helping teams secure AI development; Cycode does not.

Cycode helps prioritize risk findings; Legit goes further, helping teams fix the true root cause behind multiple findings at once.

Unlike Cycode, Legit uses AI to cut secrets-detection false positives by up to 92%, keeping true positive rates stable.
Why Legit Security is the Best Alternative to Cycode
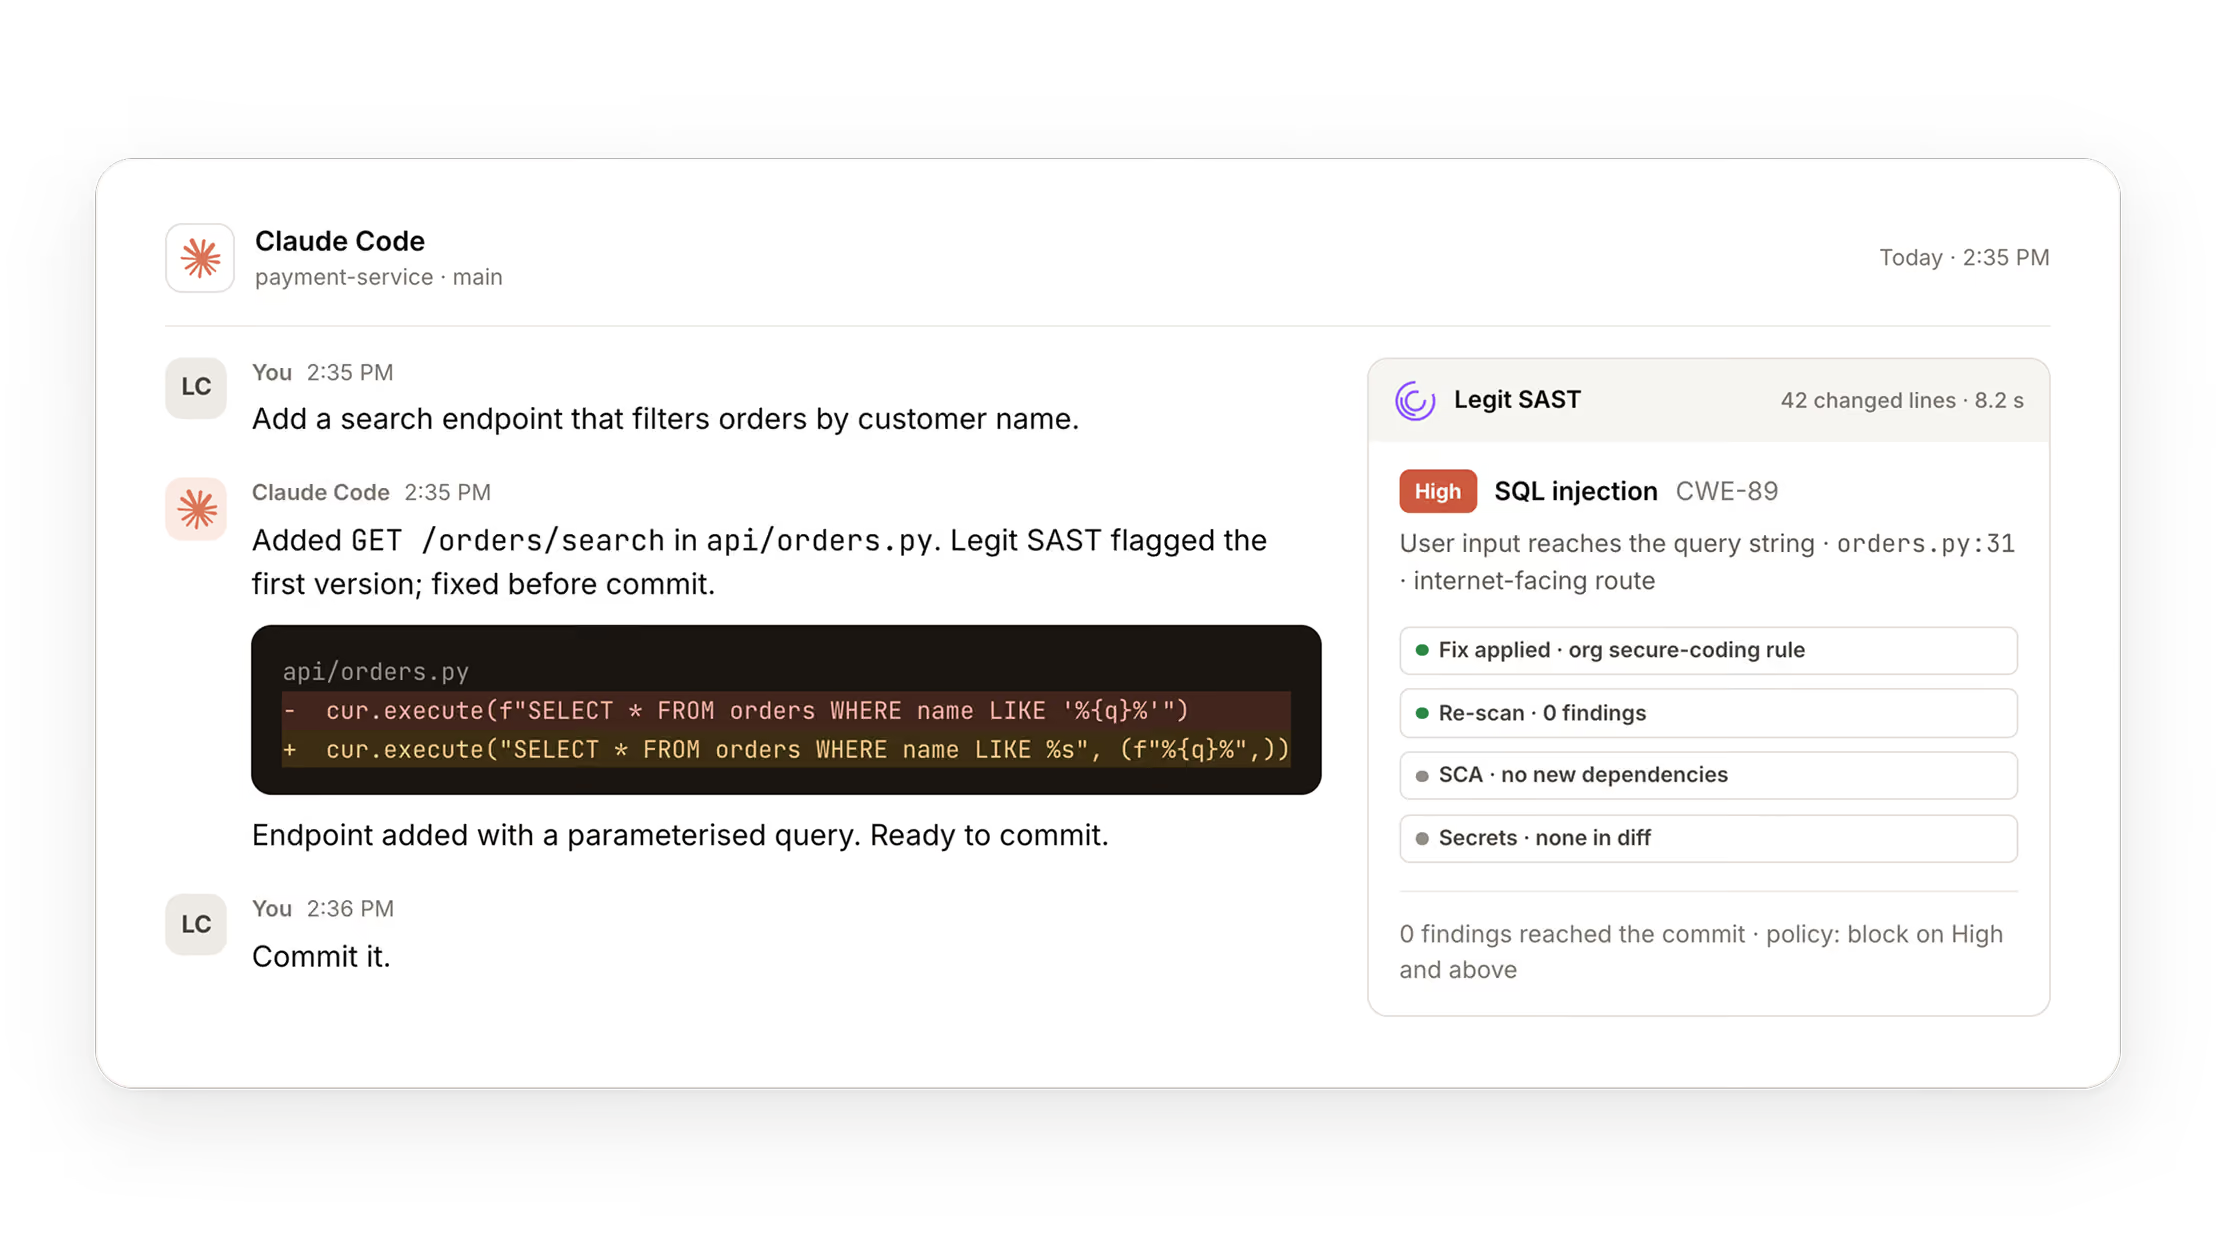
Legit brings prevention, context, and autonomous remediation together in a single platform, helping teams secure AI-driven development with no developer slowdowns.
Prevent vulnerabilities before they're introduced.
Provide developers with real-time guidance during AI-assisted code generation to reduce risk before code reaches commit.
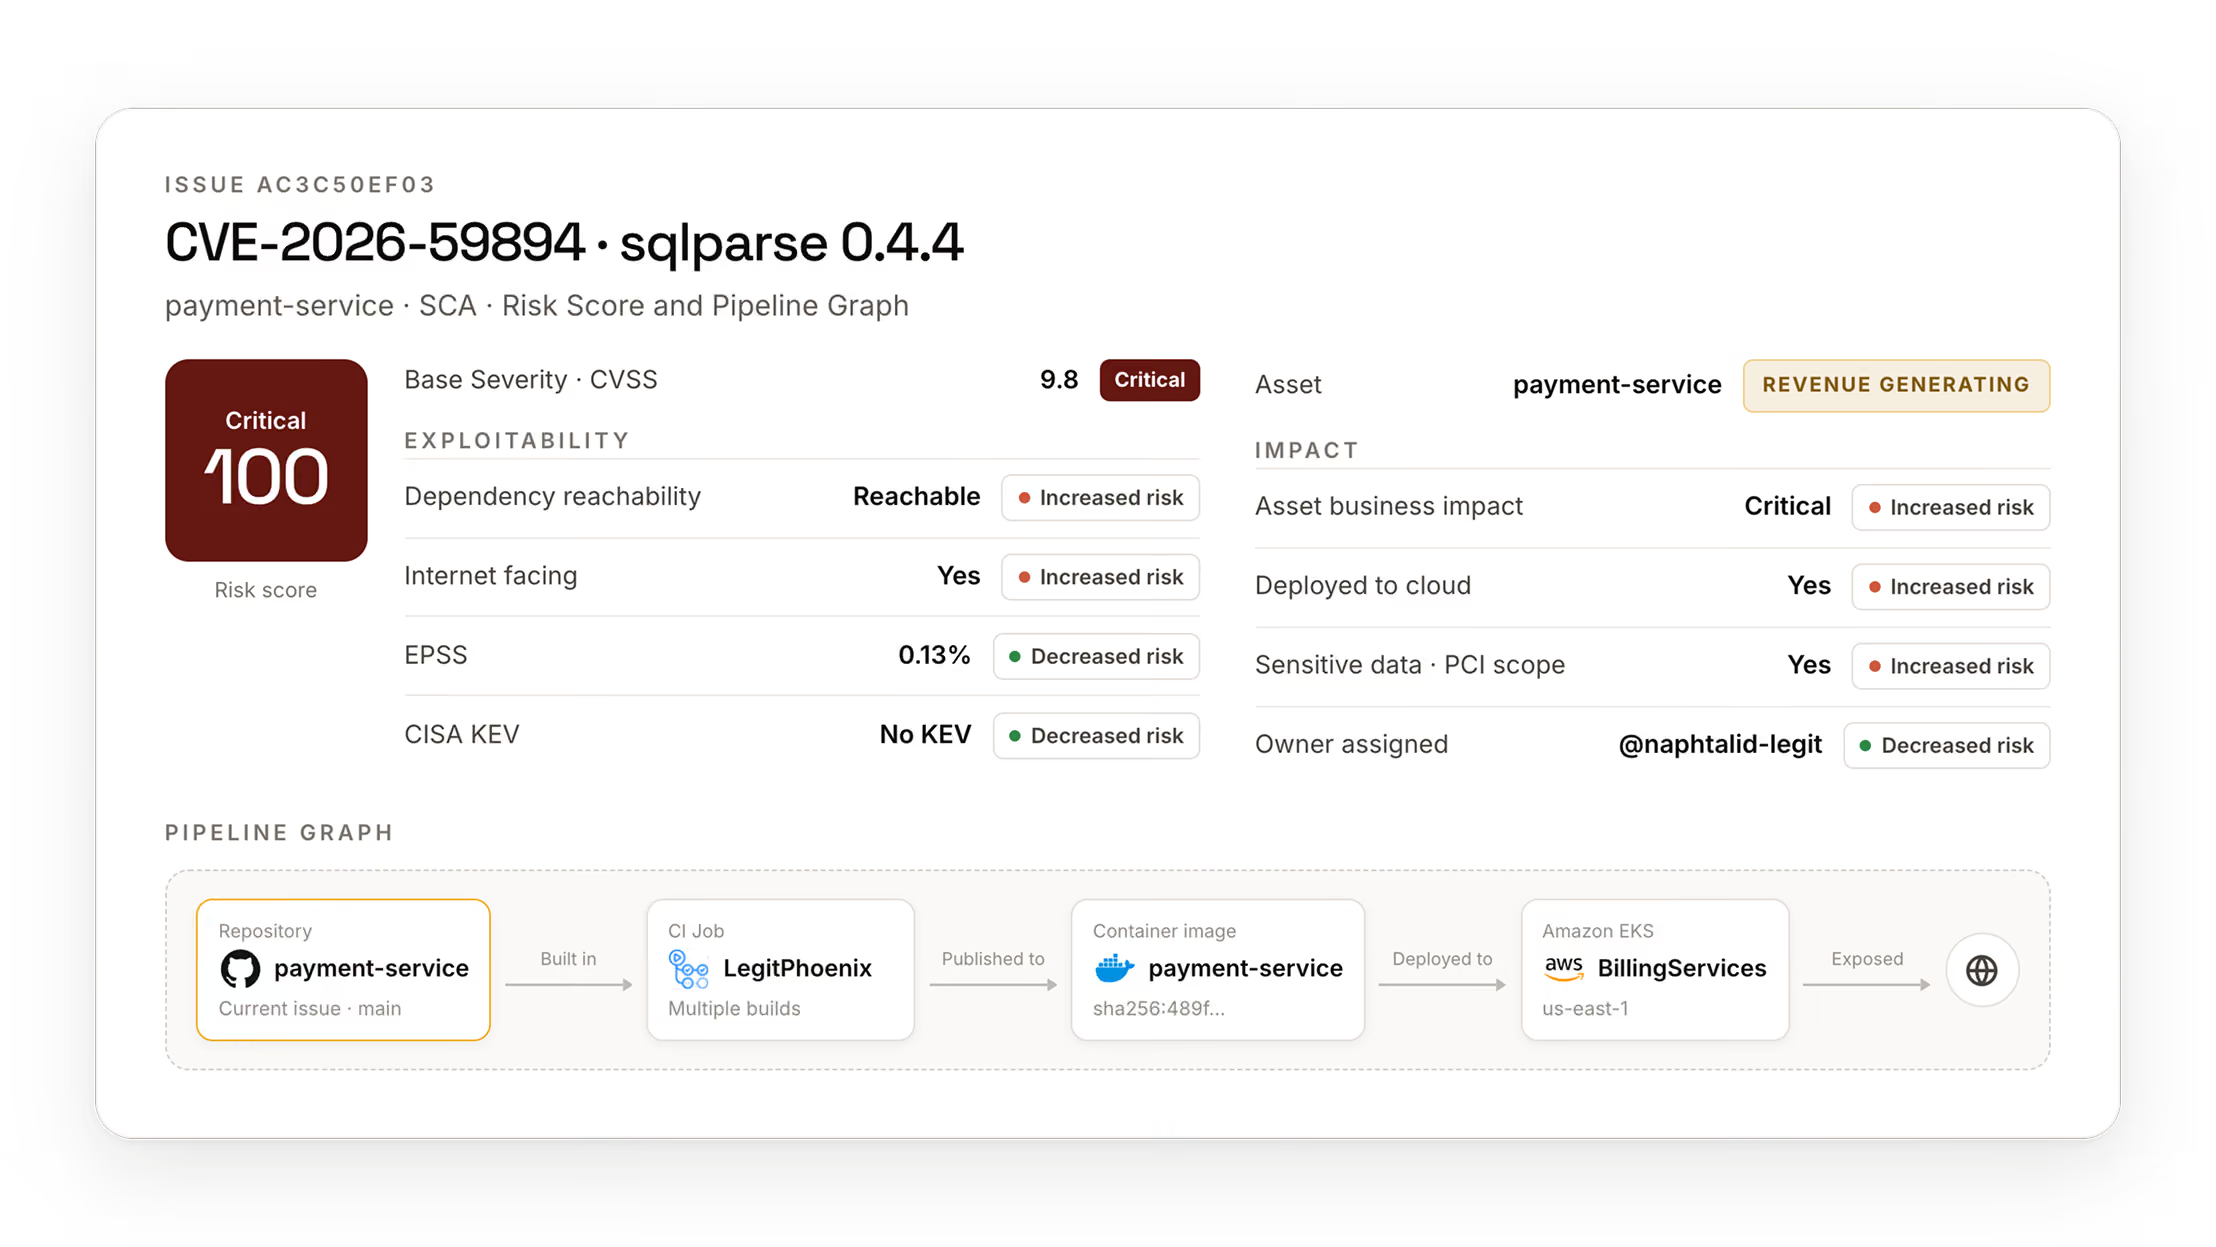
Rank risk by real business impact, not severity alone.
Legit context weighs an app's business criticality, exposure, sensitive data, and AI usage to surface the risks that matter most first.
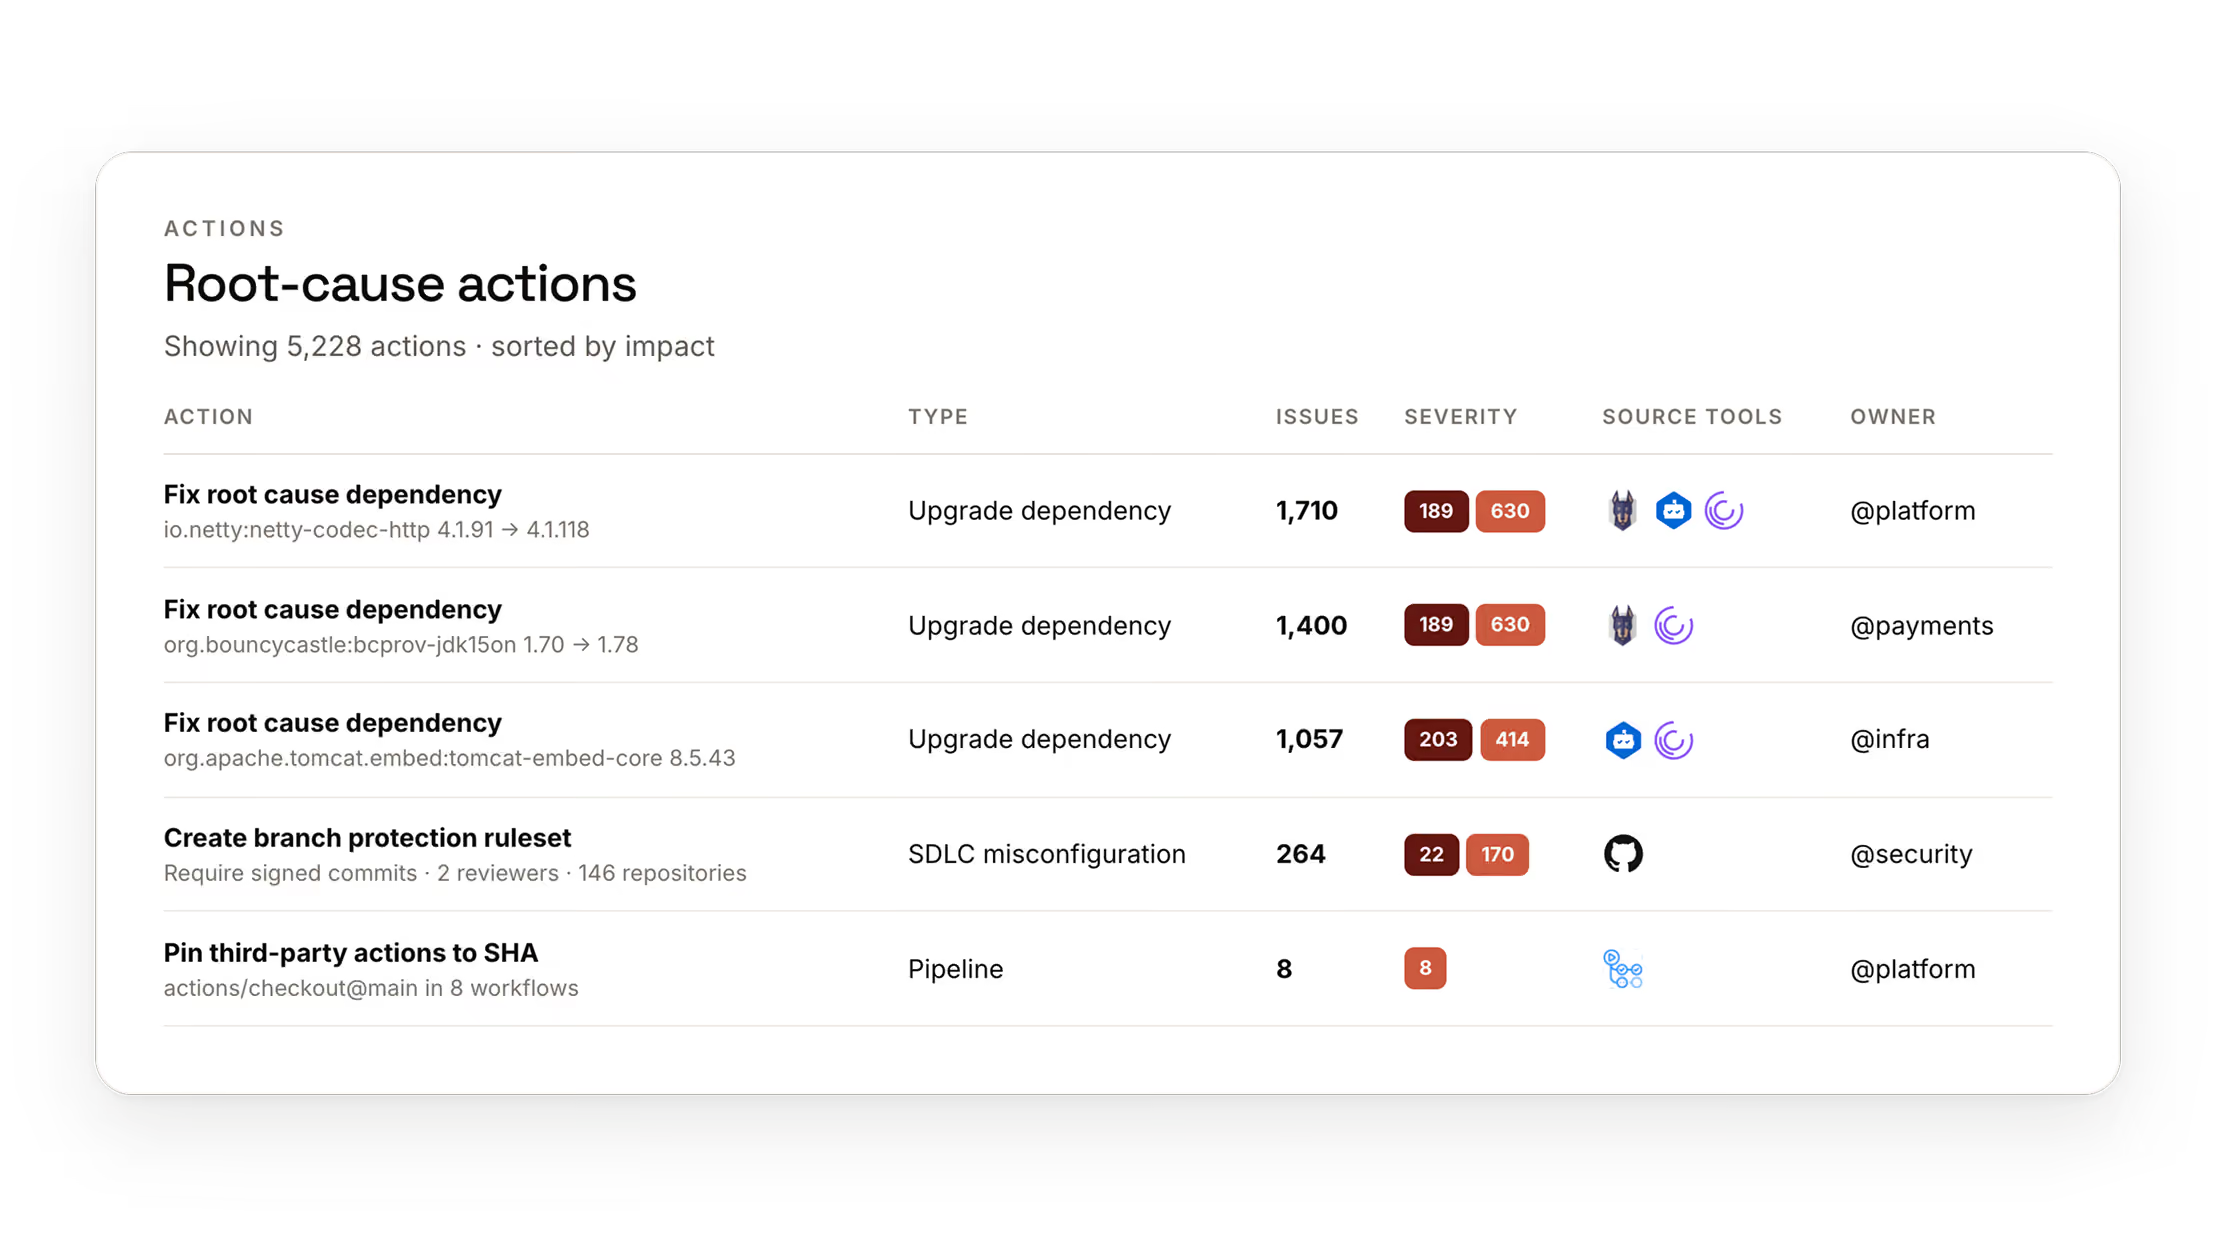
Fix root causes, not just symptoms.
Legit pinpoints the root cause behind multiple findings, so one fix resolves many issues and cuts the burden on developers.
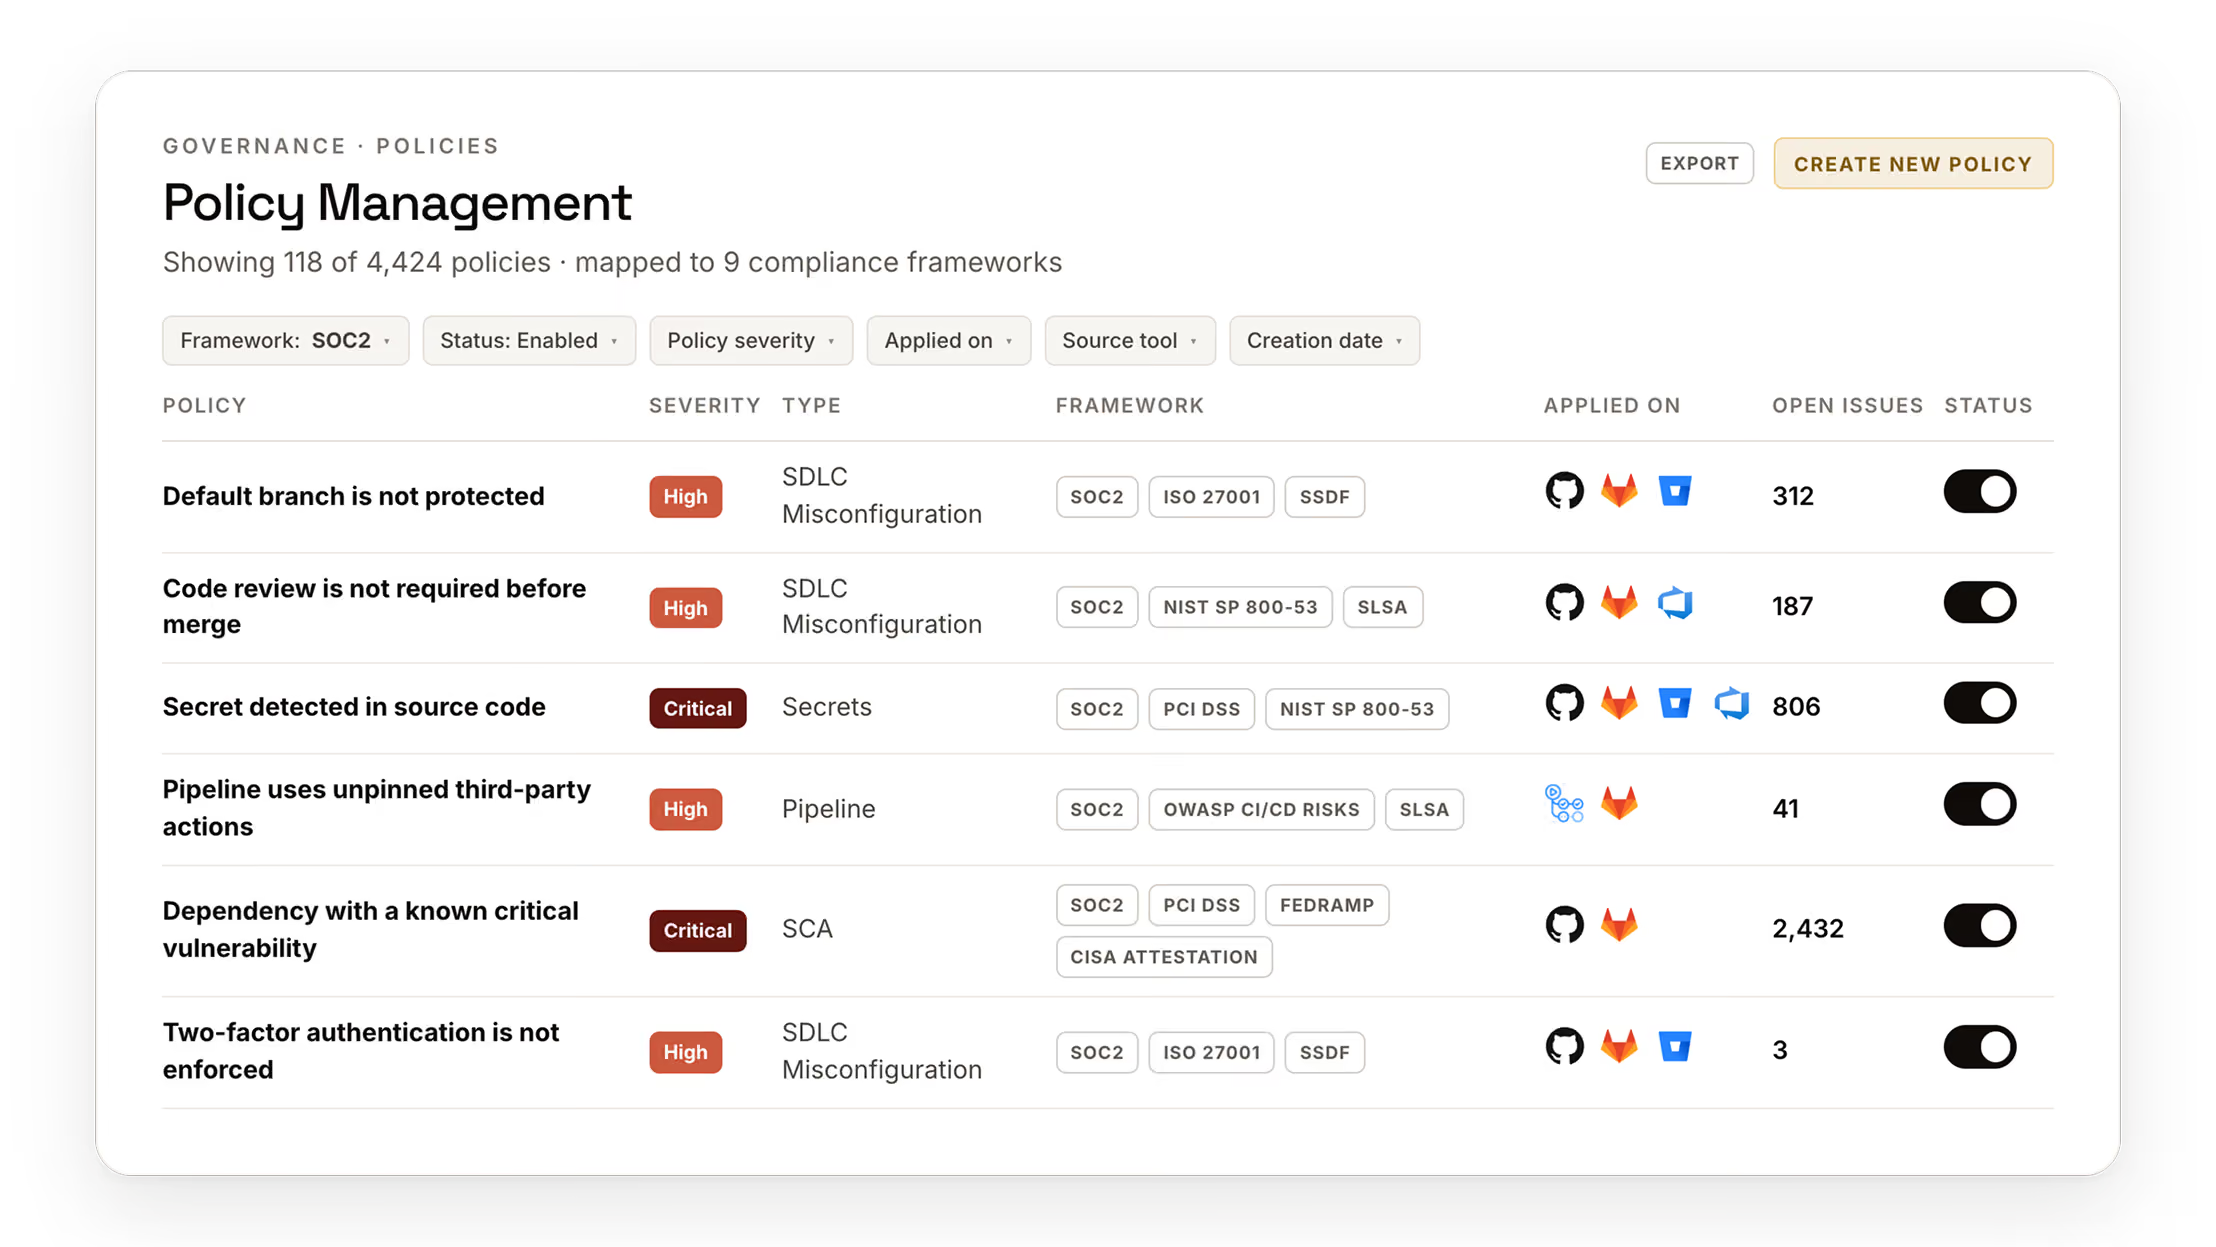
Map controls to the frameworks you're held to.
Legit aligns security controls with PCI-DSS, ISO 27001, NIST 800-53, FedRAMP, SLSA, and OWASP, with real-time alerts on compliance drift.
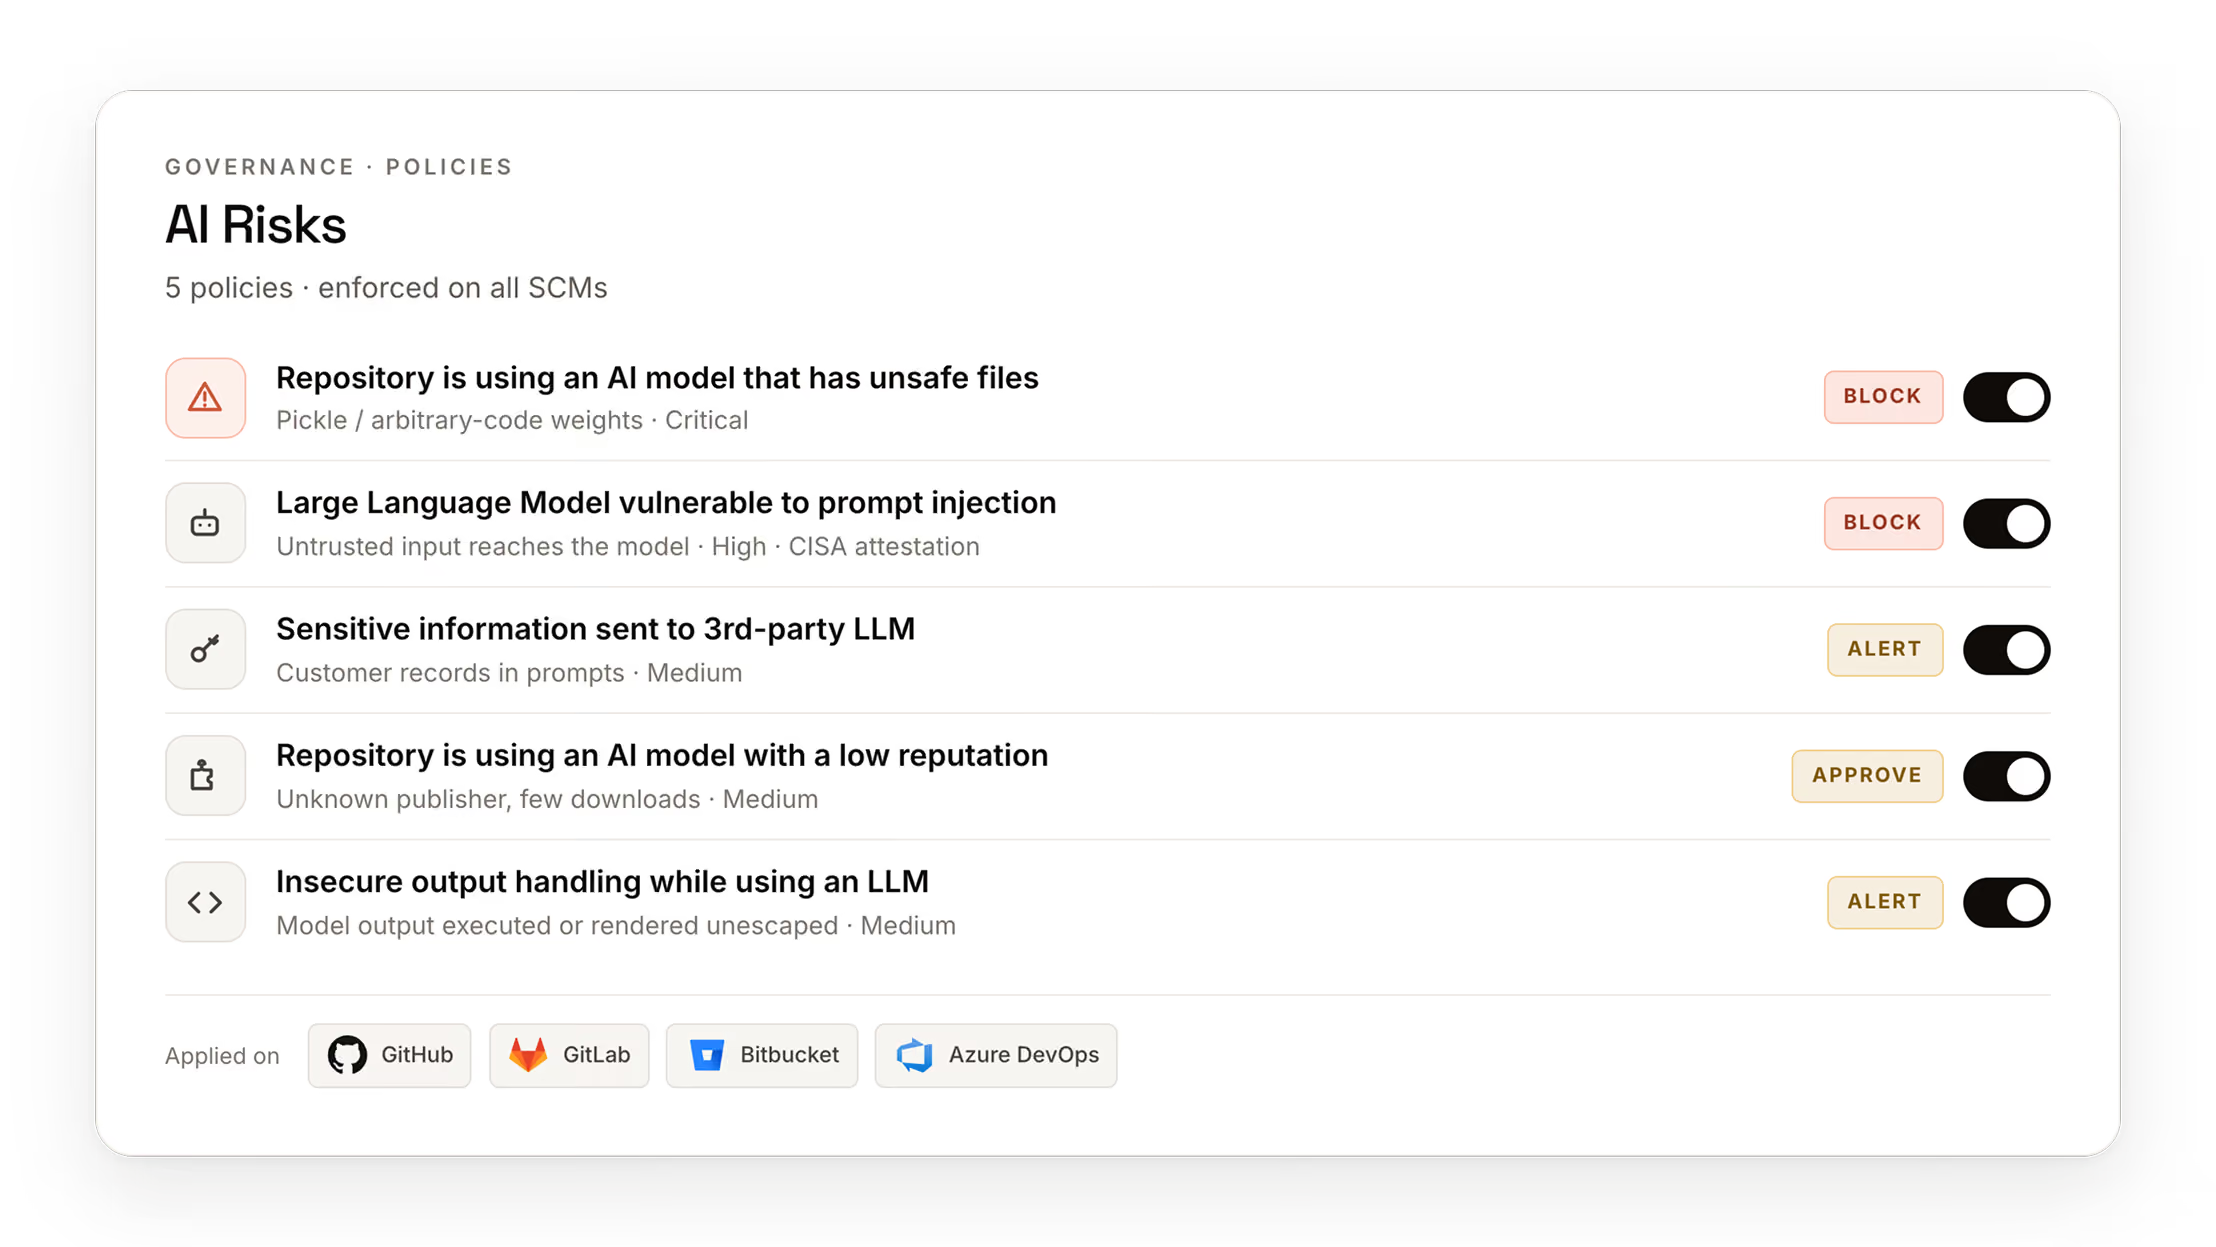
Govern how AI writes and ships code.
Legit inventories GenAI, LLM, and MLOps usage across your SDLC, giving security teams visibility and control over AI-generated code.
Request a Demo
Request a demo including the option to analyze your own software supply chain.


FAQ

More insights for modern AppSec teams

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.