Stay ahead of what’s next in Agentic AppSec.
Explore research, guides, webinars, analyst insights, and technical resources on securing AI-generated code and modern, AI-first software development.
Threats

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
Agentic Remediation Just Got Bigger: Now Fixing Vulnerabilities in Your Dependencies, Not Just Your Code
Legit Security's Agentic Remediation now tackles vulnerabilities in dependencies, ensuring faster, verified fixes and enhancing AppSec in an AI-driven landscape.
Claude Mythos 5 Can Find the Vulnerabilities. But Which Ones Actually Matter?
Discover how Claude Mythos 5 enhances vulnerability detection in AppSec and learn to prioritize findings effectively.

Your AI Agent Has New Skills. Can You Trust Them?
Discover how VibeGuard 2.0 enhances security for AI agents, ensuring visibility and control to prevent dangerous…
Secure Fast, Not Slow: What We Learned Building VibeGuard 2.0
Secure Fast, Not Slow. Read more from Legit's CTO and Co-Founder, Liav Caspi, on what we learned building VibeGuard 2.0.
GitHub Locks Down npm: What the New Install Defaults Mean for Your Supply Chain
In July 2026, GitHub is going to change how npm install works for the first time in npm's history - and it's going to…

The Government Just Made Our Case: Stop Fixing Everything, Fix What Matters.
On June 10, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a new directive on how federal…

Agentic AppSec: closing the remediation gap and automating application security
Application security has spent a decade getting brilliant at half of its job. This is about automating the other half…
Fable 5 Is Here. The AppSec Problem Hasn’t Changed.
Anthropic’s release of Fable 5 has reignited discussion about what AI means for cybersecurity. When the company…

The Missing Security Layer in AI-First Development
AI coding agents have changed how developers work. Alongside the productivity gains comes a new challenge: how do…

Scaling Our Vision: Welcoming Tamar Nulman and Omri Arnon to the Legit Team
Welcoming two world-class leaders to the Legit Security family: Tamar Nulman, our new VP of HR, and Omri Arnon, our…

Mythos: Just One Piece of the Cybersecurity Puzzle
Anthropic’s new AI model, Mythos, is being framed as a “cybersecurity reckoning.” Read more here.

Axios Hijacked: npm Account Takeover Deploys Cross-Platform RAT to Millions
Malicious Axios versions 1.14.1 and 0.30.4 were pushed to npm from a hijacked maintainer account. See what happened…
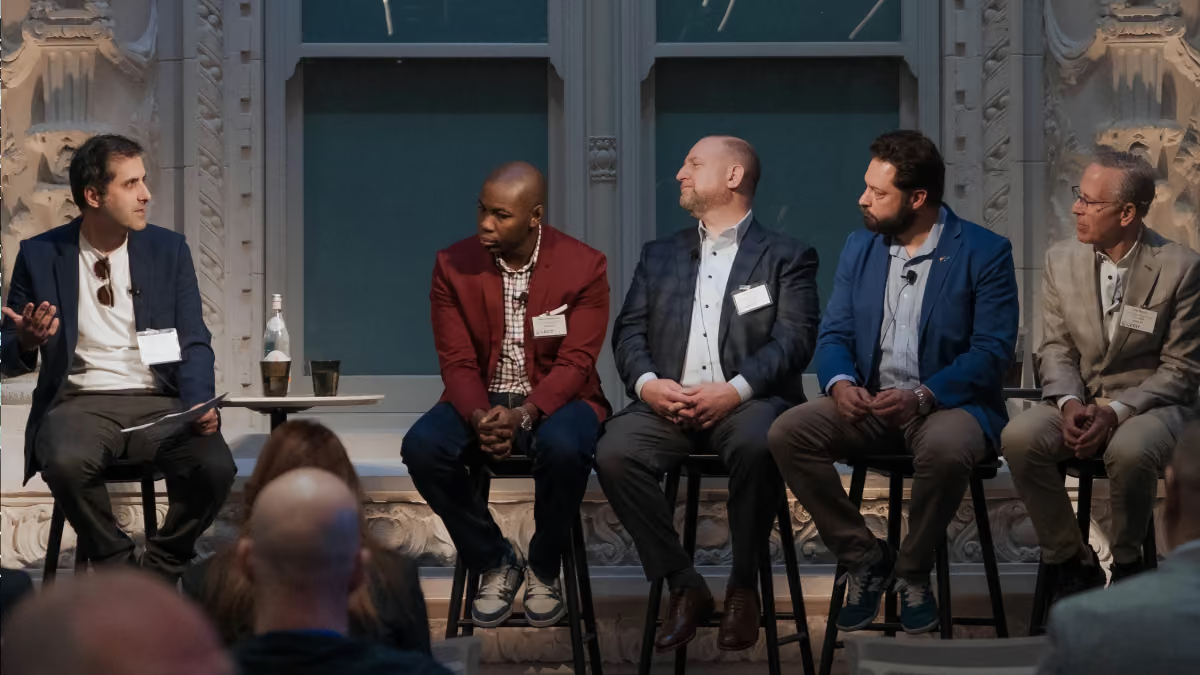
When AI Writes the Code, What Changes for Security?
Takeaways from our RSAC 2026 CISO panel: why AI-written code moves the AppSec control point, how disposable software…

When Your Scanner Becomes the Weapon: From Trivy to LiteLLM
A security breach linked to a compromised Trivy binary exposed LiteLLM. Learn how to protect your infrastructure now.

The Trivy Supply Chain Compromise: What Happened and Playbooks to Respond
Aqua Security's Trivy vulnerability scanner was compromised, exposing sensitive data. Learn how to respond and secure…

Legit Security Named 2026 AI Code Innovator in AppSec, Leader in AppSec Management
Legit Security recognized as a leader in AppSec for innovating AI code security. Discover the award-winning VibeGuard…
Legit License Scanning and Policy Enforcement
Legit’s SCA license scanning detects and classifies open-source licenses and enforces license policies in pull…
Software License Scanning vs. Manual License Review: The True Cost of Compliance
Compare manual license review with automated license scanning: coverage, speed, consistency, and cost, and when each…

Upgraded Custom ASPM Dashboards: Build Security Views That Match How Your Teams Work
Legit Security Custom Dashboards let teams build security views for executives, AppSec, DevOps and compliance, using…
Executive Brief: Questions AI is Creating that Security Can't Answer Today
AI-assisted development is outpacing AppSec governance. See the audit questions security teams can't answer today and…
Technical Architecture Guide: Fixing Code Issues Early to Protect Developer Flow
How AI-assisted coding changes SDLC architecture, why late security feedback breaks developer flow, and how pre-commit…
The AI Security Maturity Model for AI-First Development Teams
A five-stage maturity model for securing AI-assisted development, from shadow AI and reactive cleanup to proactive…

When Security Incidents Break: The Questions Every CISO Asks (And How We Securely Built a Solution in Record Time)
How Legit built its Threat Feed with AI-assisted development, secured the AI-generated code with VibeGuard, and…

Enterprise POV: Why AI Policy Without Enforcement Fails at Scale
AI usage policies don't scale without enforcement. Learn why enterprise AppSec needs guardrails at the moment…

What Breaks First When AI-Generated Code Goes Ungoverned?
The first five things that break when AI-generated code goes ungoverned, from visibility and technical debt to…

Vibe Coding Is Moving Faster Than Security - Market Research Agrees
Vibe coding is reshaping the SDLC, but security is falling behind. Explore new Gartner research on AI code risks and…
From Chatbot to Code Threat: OWASP’s Agentic AI Top 10 and the Specialized Risks of Coding Agents
Explore the OWASP Agentic AI Top 10 and how autonomous coding agents introduce unique risks to the SDLC. Secure your…
Introducing VibeGuard: AI Security & Governance for the Age of Intelligent Coding
Find out how Legit is giving organizations the visibility, control, and protection needed to safely adopt AI coding…
Securing AI-Generated Code: What Does It Look Like in Practice?
Get details on our recent survey on the security of AI-generated code.
CamoLeak: Critical GitHub Copilot Vulnerability Leaks Private Source Code
Get details on our discovery of a critical vulnerability in GitHub Copilot Chat.
Survey Reveals Consumer Sentiment on AI-Created Apps
A new Legit survey reveals 1 in 4 consumers would abandon apps over AI code vulnerabilities. Explore the data on AI…
The Risks of AI-Generated Software Development
Get details on how AI is introducing new risk to software.
How AI Is Changing the Software Development Process, and Product
Get details on how AI is transforming software, and how it is developed.

“Shai-Hulud” npm Attack: Supply Chain Attack Details
Get details on the Shai-Hulud npm, a major worm. Discover the number of compromised npm packages, the dangers, and how…
Application Security in 2025: Why Scale, AI, and Automation Are Reshaping Priorities
New survey results shed light on the state of AppSec in 2025.
Remote Prompt Injection in GitLab Duo Leads to Source Code Theft
The Legit research team unearthed vulnerabilities in GitLab Duo.
The 2025 State of Application Risk Report: Understanding AI Risk in Software Development
Get details on the AI risks Legit unearthed in enterprises' software factories.
Next.js Vulnerability: What You Need to Know
Get details on this recent vulnerability, how to respond, and how Legit can help.
GitHub Actions tj-actions/changed-files Attack
Get details on this recent supply chain attack and how to avoid similar attacks.
The 2025 State of Application Risk Report: Understanding Toxic Combinations in Application Security
Get details on the most common toxic combinations Legit unearthed in enterprises' software factories.
The Ultralytics Supply Chain Attack: How It Happened, How to Prevent
Get details on this recent supply chain attack and how to avoid falling victim to similar attacks.
Announcing Legit Root Cause Remediation
Get details on Legit's new capabilities that allow teams to quickly fix what matters most.

Announcing the 2025 State of Application Risk Report
Use the data and analysis in this report to prioritize your 2025 AppSec efforts.
How to Mitigate the Risk of GitHub Actions
How to Mitigate the Risk of GitHub Actions. Get highlights of our research into the security of GitHub Actions, and…

The Risks Lurking in Publicly Exposed GenAI Development Services
The Risks Lurking in Publicly Exposed GenAI Development Services. Get our research team's analysis of the security of…
ESG Survey Report Finds AI, Secrets, and Misconfigurations Plague AppSec Teams
ESG Survey Report Finds AI, Secrets, and Misconfigurations Plague AppSec Teams. Find out how your peers are managing…

Security Challenges Introduced by Modern Software Development
Security Challenges Introduced by Modern Software Development. Understand how modern software development is changing…
Don’t Protect Your Software Supply Chain, Defend the Entire Software Factory
Don't Protect Your Software Supply Chain, Defend the Entire Software Factory. Find out why a too-narrow definition of…
Securing the Gateway: Why Protecting Build Systems Is Crucial in Modern Software Development
Securing the Gateway: Why Protecting Build Systems Is Crucial in Modern Software Development. Understand why securing…

Verizon 2024 DBIR: Key Takeaways
Verizon 2024 DBIR Key Takeaways. Get key data points and takeaways from the 2024 Verizon Data Breach Investigations…

New Survey Finds a Paradox of Confidence in Software Supply Chain Security
New Survey Finds a Paradox of Confidence in Software Supply Chain Security. Get results of and analysis on ESG's new…

Dependency Confusion Vulnerability Found in an Archived Apache Project
Dependency Confusion Vulnerability Found in an Archived Apache Project. Get details on the Legit research team's…
Securing the Software Supply Chain: Risk Management Tips
Securing the Software Supply Chain: Risk Management Tips. Securing the software supply chain can seem daunting, but…

What You Need to Know About the XZ Utils Backdoor
What the XZ Utils backdoor (CVE-2024-3094) is, which xz/liblzma versions are affected, how to check your systems, and…

How to Get the Most From Your Secrets Scanning
How to Get the Most From Your Secrets Scanning. Secret scanning is essential for unlocking next-level software supply…
Microsoft Under Attack by Russian Cyberattackers
Microsoft Under Attack by Russian Cyberattackers. Understand how these attackers are operating and what their tactics…
Azure DevOps Zero-Click CI/CD Vulnerability
The Legit Security research team has found and reported a zero-click attack that allowed attackers to submit malicious…

SLSA Provenance Blog Series, Part 4: Implementation Challenges for SLSA Provenance for Enterprises
This blog series covers everything from SLSA levels to real-world adoption issues. It helps enterprises confidently…
GitHub, PyTorch and More Organizations Found Vulnerable to Self-Hosted Runner Attacks
Learn how vulnerable self-hosted runners can lead to severe software supply chain attacks.

SLSA Provenance Blog Series, Part 3: The Challenges of Adopting SLSA Provenance
In this part of the SLSA series, we break down SLSA provenance levels, explore the structure of provenance documents…
Legit Discovers "AI Jacking" Vulnerability in Popular Hugging Face AI Platform
Uncovering 'AIJacking': How Attackers Exploit Hugging Face for AI Supply Chain Attacks - A Deep Dive into…
Top Risks of Ignoring AI Code in Your Organization & LLM Embedding
Explore the security risks of generative AI, including code opacity and embedding concerns, in the evolving landscape…
Emerging Risks with Embedded LLM in Applications
Learn how the use of Large Language Models (LLMs) like OpenAI's GPT and Google's Bard can create security risks in…

How We Found Another GitHub Actions Environment Injection Vulnerability in a Google Project
This blog shows another case of GitHub Actions environment injection vulnerability in a Google repository.
Supply Chain Attacks Overflow: PyPI Suspended New Registrations
After PyPI paused new registrations due to a surge in malicious packages, learn how Legit Security helps protect your…
Deep Dive Into SLSA Provenance and Software Attestation
Discover the SLSA framework, designed to ensure the integrity of software artifacts and enhance overall software…
SLSA Provenance Blog Series, Part 1: What Is Software Attestation
In this blog series, we uncover the details of SLSA provenance which refers to the ability to trust the authenticity…
5 Ways Attackers Exploit Hardcoded Secrets & How to Prevent
Explore the risks of secret exposure through leaked source code & why traditional scanners may not fully protect…

The Business Risks and Costs of Source Code Leaks and Prevention Tips
Protect your business from the serious consequences of code leaks by taking proactive measures to enhance your…
Sophisticated 3CX Software Supply Chain Attack Affects Millions of Users
3CX, an international VoIP IPBX software, experienced software supply chain attack. We detail what occurred, and how…
Top 8 Cloud Application Security Challenges and Issues
Discover top cloud security threats and learn effective techniques to keep your cloud applications secure year-round.
Remote Code Execution Vulnerability in Azure Pipelines Can Lead To Software Supply Chain Attack
Our team has found a vulnerability in Azure Pipelines (CVE-2023-21553) that allows an attacker to execute malicious…
Exposing Secrets Via SDLC Tools: The Artifactory Case
Our team investigated how sensitive information can get exposed via SDLC tools that may be used as part of your…

Exposing Secrets Via SDLC Tools: The SonarQube Case
We investigate how sensitive information can get exposed via AppSec tools that you use in your dev pipeline, using the…
How to Continuously Detect Vulnerable Jenkins Plugins to Avoid a Software Supply Chain Attack
See how attackers used compromised Jenkins plugins to attack the software supply chain and how to continuously detect…
The MarkDownTime Vulnerability: How to Avoid DoS Attack on Business
Explore our findings on a common markdown syntax vulnerability and its potential to cause Denial-of-Service (DoS)…
Critical and Time Sensitive OpenSSL Vulnerability - The Race Between Attackers and Defenders
OpenSSL has announced a critical fix in version 3.0.7 to be released Nov 1st. It means that on Tuesday the race will…
Novel Pipeline Vulnerability Discovered; Rust Found Vulnerable
New software supply chain vulnerabilities use artifact poisoning and attack the software development pipelines on…
Toyota Customer Data Leaked Due To Software Supply Chain Attack
On Oct 7th, Toyota announced a possible data leakage incident. The compromised data contained 296,019 customers'…
Software Supply Chain Attack Leads to Trojanized Comm100 Installer
On the 29th of September, it was revealed that the installer for the widely used Comm100 Live Chat application…
New Software Supply Chain Attack Installs Trojans on Adobe's Magento E-Commerce Platform
A popular vendor of Magento-WordPress integrations, FishPig, was hacked and its extensions used to install the Rekoobe…
Software Artifacts Best Practices to Prevent Getting Hacked
Malicious actors are poisoning your artifacts to compromise your software supply chain. Learn how to protect your…
Attackers Can Bypass GitHub Required Reviewers to Submit Malicious Code
GitHub’s required reviewers capability can be bypassed if currently using this setting to require at least one code…
How Was LastPass Compromised? Software Supply Chain Attack Tips
LastPass data breach: unauthorized access compromised developer accounts and proprietary source code. Learn about the…
Breaking News: How a Massive Malware Attack Almost Occurred on GitHub
Stephen Lacy reported a massive malware attack attempt on GitHub. None of the original repositories were infected, but…
Google & Apache Found Vulnerable to GitHub Environment Injection
Learn how Legit Security discovered a vulnerable GitHub actions workflow that affected Google, Apache and potentially…
Vulnerable GitHub Actions Workflows Part 2: Actions That Open the Door to CI/CD Pipeline Attacks
We examine a bug we’ve found in a popular third-party GitHub action and how it could lead to your SDLC pipeline being…
Latest GitHub OAuth Tokens Attack Explained and How to Protect Yourself
This GitHub OAuth access token attack was announced by GitHub Security and is a compromise of OAuth access tokens…

A Cautionary Tale: The Untold Story of the GitLab CVE Backdoor (CVE-2022-1162)
On April 1st, GitLab announced Critical Security Release CVE-2022-1162, disclosing a very bizarre vulnerability and…
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline
Learn how Legit Security discovered a vulnerable GitHub Actions workflow. Get details on the vulnerability and what…