A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
The split security teams already know
Ask a product security engineer where automation ends and the hard work begins, and you often get a version of the same answer.
One senior product security engineer described it this way in a recent conversation: about 70% of the process was automated and 30% was manual. That remaining slice still requires hands-on work. Their team is trying to use AI tools to help prioritize those issues.
This is not an industry benchmark. It's a practitioner's own read of their pipeline. But it matches what we keep hearing from AppSec leaders: the scanners and orchestration are largely in place. The stuck work is deciding what deserves attention.
Automation solved volume. It didn't solve judgment.
The automated 70% is real progress. Findings get collected. Pipelines run without someone clicking through every tool. Tickets open. Dashboards update.
The manual 30% is where judgment lives:
- Is this finding reachable in a production path?
- Does the application handle sensitive data or sit on the internet?
- Is the issue exploitable, or is it just a theoretical severity label?
- Given the team's capacity this sprint, what should move first?
Answering those takes context, and adding another scanner doesn't give you any. Without context, "prioritization" is still a human sorting a queue that grows faster than anyone can review.
So when teams shop for AI right now, most want help with the part that still burns calendar time, which is ranking what matters.
Where context-aware prioritization fits
Context-aware prioritization is the capability that sits squarely on that 30%.
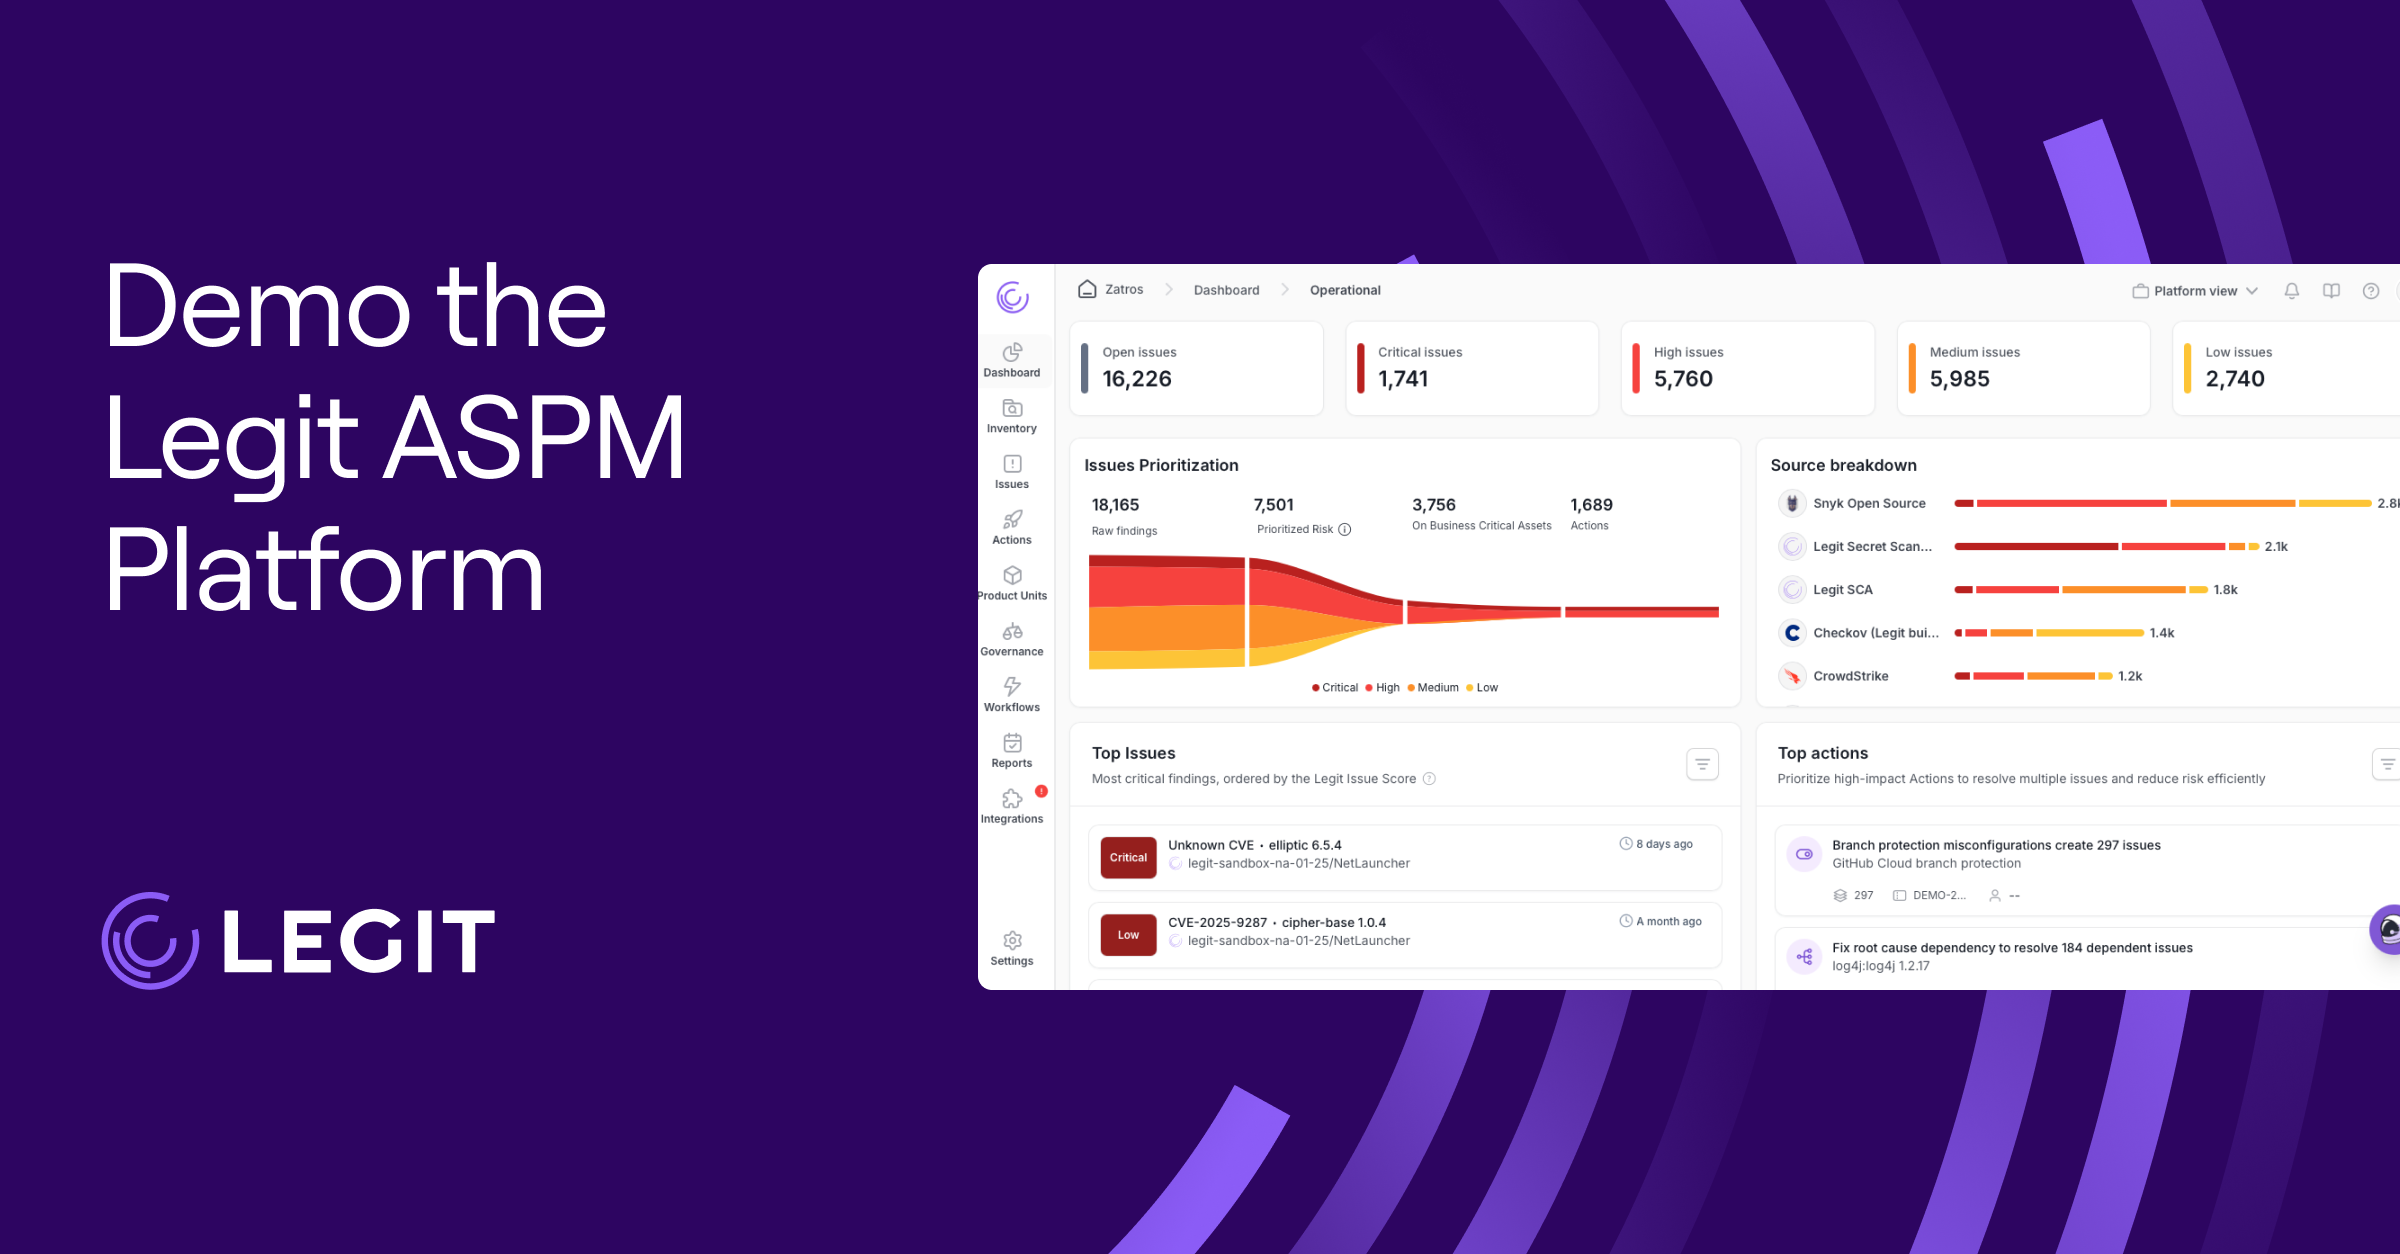
In Legit's Agentic AppSec platform, agentic context enriches every finding with the signals security teams use to decide: reachability, business criticality, exploitability, exposure, and related risk factors. AI-powered prioritization then surfaces the issues that are worth acting on, instead of treating every high-severity result as equal.
People still make the calls. They just shouldn't have to redo triage on findings that context could have ranked (or thrown out) already.
When Legit flags something as critical, it reflects application reality: a high-severity issue in an internet-facing, revenue-generating system that handles sensitive data is not the same priority as a similar-looking issue in an internal tool with no exposure. Most tooling still blurs that line, and context is what lets you draw it.
Don't stop at a better queue
Better prioritization alone still leaves you in find-it, fix-it mode. The stronger move is to use that prioritized set as fuel for the rest of the cycle.
Remediation agents can start with the highest-risk issues and apply fixes that match policy. Those fixes inform prevention at code generation, so coding agents introduce fewer of the same problems next time. Over successive cycles, the manual 30% should shrink because fewer noisy or low-value items reach the human desk in the first place.
That's the gap between "AI that helps us sort tickets faster" and Agentic AppSec. Sorting faster still leaves you with the same pile next month; a loop where context, remediation, and prevention build on each other makes the pile smaller.
A practical test for your program
If your team has already automated most of the pipeline, try this framing in your next planning conversation:
- Where does human time actually go each week: detection, triage, or fix coordination?
- Of the issues that reach a human, what share could context have ranked or filtered without a meeting?
- Are you buying AI to accelerate the 70% you already automated, or to finally shrink the 30%?
If your answer to that last one is the 30%, you're in good company. Product security teams are naming the same gap out loud.
So start with the 30%: put context on it, then let remediation and prevention keep shrinking it.
Download our new whitepaper.