
Stay ahead of what’s next in Agentic AppSec.
Explore research, guides, webinars, analyst insights, and technical resources on securing AI-generated code and modern, AI-first software development.
AI In Cybersecurity

Stop Drowning in the 30%
A product security engineer described their AppSec pipeline as roughly 70% automated and 30% still manual. That manual slice is where teams get stuck, and where context-aware prioritization belongs.
Agentic Remediation Just Got Bigger: Now Fixing Vulnerabilities in Your Dependencies, Not Just Your Code
Legit Security's Agentic Remediation now tackles vulnerabilities in dependencies, ensuring faster, verified fixes and enhancing AppSec in an AI-driven landscape.
Claude Mythos 5 Can Find the Vulnerabilities. But Which Ones Actually Matter?
Discover how Claude Mythos 5 enhances vulnerability detection in AppSec and learn to prioritize findings effectively.

Your AI Agent Has New Skills. Can You Trust Them?
Discover how VibeGuard 2.0 enhances security for AI agents, ensuring visibility and control to prevent dangerous…
Secure Fast, Not Slow: What We Learned Building VibeGuard 2.0
Secure Fast, Not Slow. Read more from Legit's CTO and Co-Founder, Liav Caspi, on what we learned building VibeGuard 2.0.
GitHub Locks Down npm: What the New Install Defaults Mean for Your Supply Chain
In July 2026, GitHub is going to change how npm install works for the first time in npm's history - and it's going to…

The Government Just Made Our Case: Stop Fixing Everything, Fix What Matters.
On June 10, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a new directive on how federal…

Agentic AppSec: closing the remediation gap and automating application security
Application security has spent a decade getting brilliant at half of its job. This is about automating the other half…
Fable 5 Is Here. The AppSec Problem Hasn’t Changed.
Anthropic’s release of Fable 5 has reignited discussion about what AI means for cybersecurity. When the company…

The Missing Security Layer in AI-First Development
AI coding agents have changed how developers work. Alongside the productivity gains comes a new challenge: how do…

Scaling Our Vision: Welcoming Tamar Nulman and Omri Arnon to the Legit Team
Welcoming two world-class leaders to the Legit Security family: Tamar Nulman, our new VP of HR, and Omri Arnon, our…

Mythos: Just One Piece of the Cybersecurity Puzzle
Anthropic’s new AI model, Mythos, is being framed as a “cybersecurity reckoning.” Read more here.

Axios Hijacked: npm Account Takeover Deploys Cross-Platform RAT to Millions
Malicious Axios versions 1.14.1 and 0.30.4 were pushed to npm from a hijacked maintainer account. See what happened…
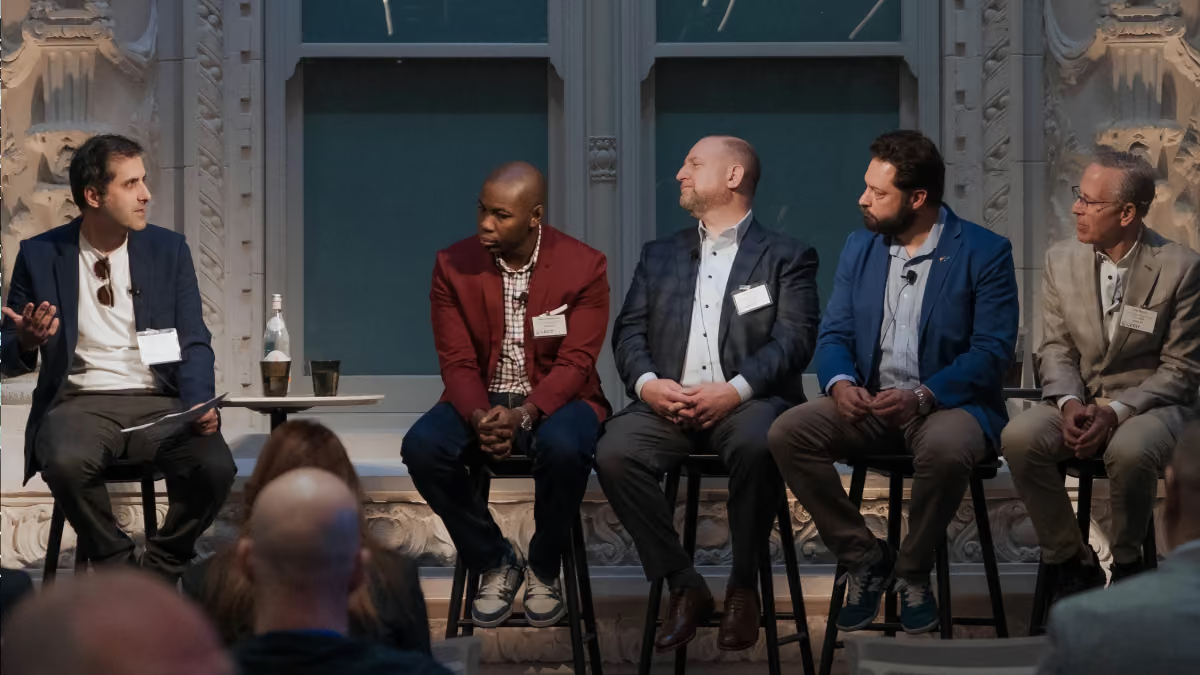
When AI Writes the Code, What Changes for Security?
Takeaways from our RSAC 2026 CISO panel: why AI-written code moves the AppSec control point, how disposable software…

When Your Scanner Becomes the Weapon: From Trivy to LiteLLM
A security breach linked to a compromised Trivy binary exposed LiteLLM. Learn how to protect your infrastructure now.

The Trivy Supply Chain Compromise: What Happened and Playbooks to Respond
Aqua Security's Trivy vulnerability scanner was compromised, exposing sensitive data. Learn how to respond and secure…

Legit Security Named 2026 AI Code Innovator in AppSec, Leader in AppSec Management
Legit Security recognized as a leader in AppSec for innovating AI code security. Discover the award-winning VibeGuard…
Legit License Scanning and Policy Enforcement
Legit’s SCA license scanning detects and classifies open-source licenses and enforces license policies in pull…
Software License Scanning vs. Manual License Review: The True Cost of Compliance
Compare manual license review with automated license scanning: coverage, speed, consistency, and cost, and when each…

Upgraded Custom ASPM Dashboards: Build Security Views That Match How Your Teams Work
Legit Security Custom Dashboards let teams build security views for executives, AppSec, DevOps and compliance, using…
Executive Brief: Questions AI is Creating that Security Can't Answer Today
AI-assisted development is outpacing AppSec governance. See the audit questions security teams can't answer today and…
Technical Architecture Guide: Fixing Code Issues Early to Protect Developer Flow
How AI-assisted coding changes SDLC architecture, why late security feedback breaks developer flow, and how pre-commit…
The AI Security Maturity Model for AI-First Development Teams
A five-stage maturity model for securing AI-assisted development, from shadow AI and reactive cleanup to proactive…

When Security Incidents Break: The Questions Every CISO Asks (And How We Securely Built a Solution in Record Time)
How Legit built its Threat Feed with AI-assisted development, secured the AI-generated code with VibeGuard, and…

Enterprise POV: Why AI Policy Without Enforcement Fails at Scale
AI usage policies don't scale without enforcement. Learn why enterprise AppSec needs guardrails at the moment…





