
Stay ahead of what’s next in Agentic AppSec.
Explore research, guides, webinars, analyst insights, and technical resources on securing AI-generated code and modern, AI-first software development.
Explainers
The 2025 State of Application Risk Report: Understanding AI Risk in Software Development
Get details on the AI risks Legit unearthed in enterprises' software factories.
The 2025 State of Application Risk Report: Understanding Toxic Combinations in Application Security
Get details on the most common toxic combinations Legit unearthed in enterprises' software factories.
How to Reduce Risk From Exposed Secrets
Understand how secrets end up exposed, and how to prevent this risk.
What is ASPM? Application Security Posture Management 101
Learn how Legit Security enhances Application Security Posture Management (ASPM) by automating key processes to ensure…
Securing the Vault: ASPM's Role in Financial Software Protection
Discover the importance of Application Security Posture Management (ASPM) in financial software protection. Learn how…

Dependency Confusion Vulnerability Found in an Archived Apache Project
Dependency Confusion Vulnerability Found in an Archived Apache Project. Get details on the Legit research team's…
How to Reduce the Risk of Using External AI Models in Your SDLC
How to Reduce the Risk of Using External AI Models in Your SDLC. Understand how AI models add risk and how to address…
Securing the Software Supply Chain: Risk Management Tips
Securing the Software Supply Chain: Risk Management Tips. Securing the software supply chain can seem daunting, but…
Understanding the White House Report on Secure and Measurable Software
Understanding the White House Report on Secure and Measurable Software. Get details on the report, how to address it…

How to Address CISA Attestation
How to Address CISA Attestation. Get details on the CISA Attestation, how to address it, and how Legit can help.
Rethinking Shift Left: Overcoming Context Gaps to Reduce AppSec & Developer Friction
Discover how ASPM reduces friction and shifts security left for AppSec and developers with deep context. Optimize your…

SBOM Management Best Practices
Learn SBOM best practices for application security. Explore its evolution, significance, and optimization strategies…
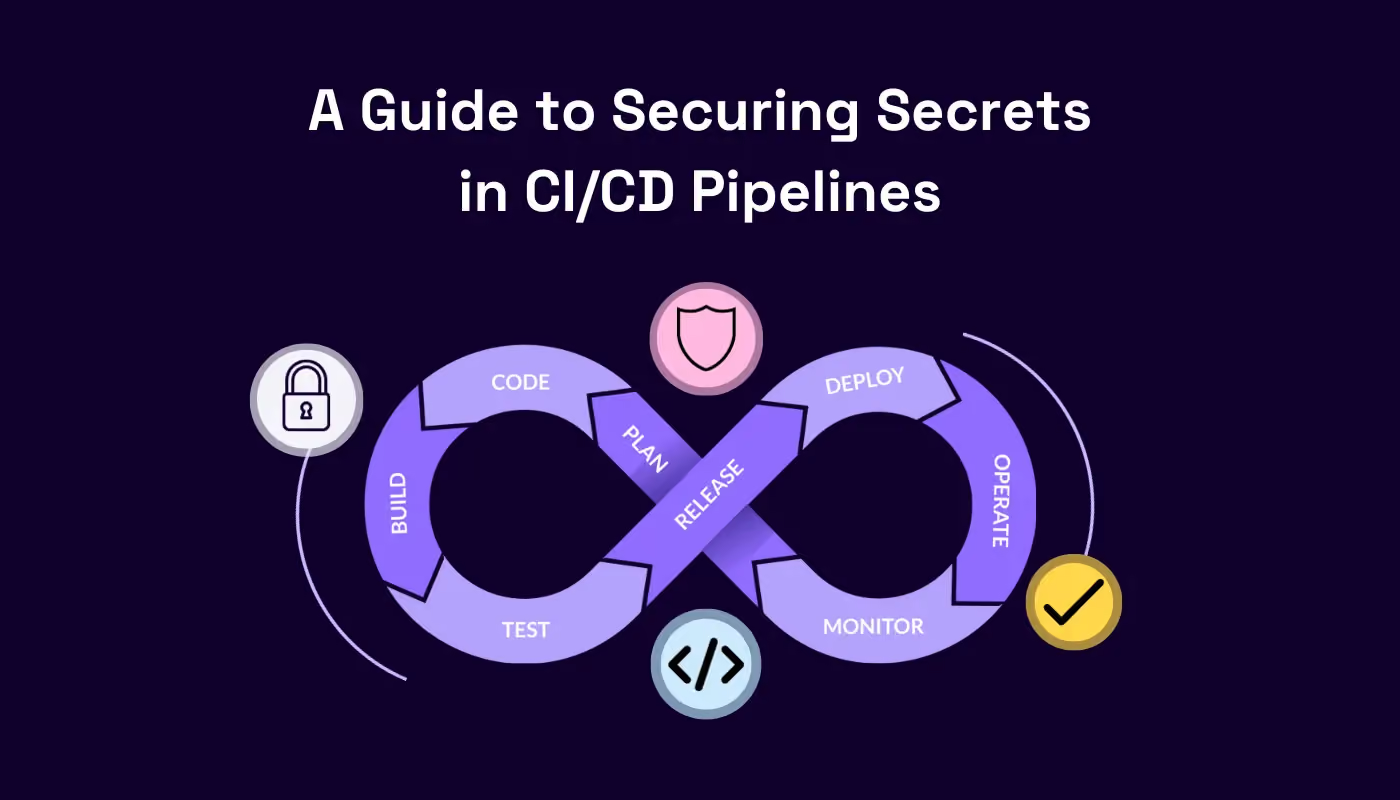
A Guide to Securing Secrets in CI/CD Pipelines
Dive into the world of software secrets, learn best practices for secure CI/CD, and safeguard sensitive data in this…

How CNAPP Security Revolutionizes Cloud Protection
Enhance your cloud security with CNAPP. Explore benefits and find the right provider to protect your cloud environment…

Guide to Secure Your CI/CD Pipelines by NIST
Explore NIST SP 800-204D for secure DevSecOps CI/CD pipelines. Learn key strategies for effectively integrating…
What Is Cloud Security Posture Management? CSPM Explained
Discover how cloud security posture management (CSPM) helps identify cloud misconfigurations, enforce compliance, and…

An In-Depth Guide to the Vulnerability Management Lifecycle
Learn to master the vulnerability management lifecycle. Safeguard against threats, implement best practices, and…

SCA vs SAST: Cybersecurity Comparison Tools
Compare SCA vs SAST to enhance cybersecurity. Understand their methods, benefits, and how they protect against…

How to Choose the Right Vulnerability Management Tools
Discover core functions, benefits, and tips for selecting the best vulnerability management solutions to boost your…
Securing Your CI/CD Pipeline: Exploring the Dangers of Self-Hosted Runners
CI/CD automates software development, while self-hosted runners enable general customization. SaaS platforms provide…

NIST Secure Software Development Framework Tips to Stay Ahead of Future Requirements
Boost the security of your code with the NIST SSDF (Secure Software Development Framework). Safeguard your business…
Securing AI-Generated Code
Explore Legit Security's revolutionary AI application security, risks, and solutions in our blog.

Embracing the Future of Secure Software Development: A Comprehensive Look at the SSDF
Explore the benefits of the Secure Software Development Framework (SSDF) and how it differs from traditional SSDLC…
Supply Chain Attacks Overflow: PyPI Suspended New Registrations
After PyPI paused new registrations due to a surge in malicious packages, learn how Legit Security helps protect your…

Tips to Secure the Software Development Lifecycle (SDLC) in Each Phase
With the explosion of attacks in the modern DevOps stack, it has become a vital business requirement to provide…
Sophisticated 3CX Software Supply Chain Attack Affects Millions of Users
3CX, an international VoIP IPBX software, experienced software supply chain attack. We detail what occurred, and how…
Top 8 Cloud Application Security Challenges and Issues
Discover top cloud security threats and learn effective techniques to keep your cloud applications secure year-round.

What is Secure SDLC? Best Practices for Enhanced Security
Understand SDLC security with our breakdown of each Software Development Life Cycle stage for enhanced software…
GUAC Explained in 5 Minutes
We cover GUAC and its value for your team once GUAC reaches maturity and untangle the complexity of security and…

What are the Five Elements of the NIST Cybersecurity Framework?
This blog details the five elements of the NIST cybersecurity framework and identifies the critical aspects of…
What Are Immutable Tags And Can They Protect You From Supply Chain Attacks?
Some tags cannot be trusted to reference the same object all the time, and can be changed without the users’…
Latest GitHub OAuth Tokens Attack Explained and How to Protect Yourself
This GitHub OAuth access token attack was announced by GitHub Security and is a compromise of OAuth access tokens…
What is an SBOM? SBOM explained in 5 minutes
What is an #SBOM, how is it used and why it is important to software supply chain security? We explain the SBOM in 5…
Detecting Secrets in Your Source Code
What are secrets in source code, why they must be protected, and how to keep them safe.





