Legit Scans for Secrets in SharePoint
Get details on Legit's new ability to scan for secrets in SharePoint.
Get details on Legit's new ability to scan for secrets in SharePoint.
Secrets, credentials, and non-human identities (NHIs) are proliferating, causing massive headaches for security teams. Some recent incidents include the Sisense breach and Snowflake's stolen credentials. While much of the secrets spotlight has been on hard-coded passwords in source code, there are other popular, but often overlooked, spots for this type of exposure, such as collaboration software.
With this in mind, Legit is happy to announce the new ability to scan SharePoint for exposed secrets, broadening our coverage and defense against this challenge.
Many organizations rely on SharePoint to store and share documents, spreadsheets, and internal resources. While this makes collaboration easier, it also introduces a significant security risk — sensitive information, such as API keys, passwords, and certificates often get uploaded and stored unintentionally.
Why SharePoint is a blind spot for secrets management
Unlike source code repositories, which are regularly scanned for secrets as part of DevSecOps pipelines, SharePoint is often overlooked.
However, it is common for employees to:
- Store API keys, database credentials, and passwords in spreadsheets or text documents in SharePoint for easy access.
- Share sensitive configuration files that contain hardcoded credentials in SharePoint.
- Save backups of scripts or code snippets that include authentication tokens in SharePoint.
Since SharePoint is designed for easy sharing, these exposed secrets can quickly spread across teams, departments, or even external collaborators, increasing the risk of unauthorized access.
The consequences of exposed secrets in SharePoint
If an attacker gains access to a SharePoint environment with exposed credentials, they could:
- Use cloud API keys to access and modify infrastructure, leading to data exfiltration or service disruption.
- Leverage database credentials to extract sensitive customer data.
- Exploit OAuth tokens to hijack user sessions and gain unauthorized access to critical applications.
Because SharePoint is not a traditional code repository, security teams lack visibility into or overlook these risks, until it's too late. That's why automated secrets scanning for SharePoint is critical for securing an organization's data.
How Legit Security's SharePoint secrets scanning works
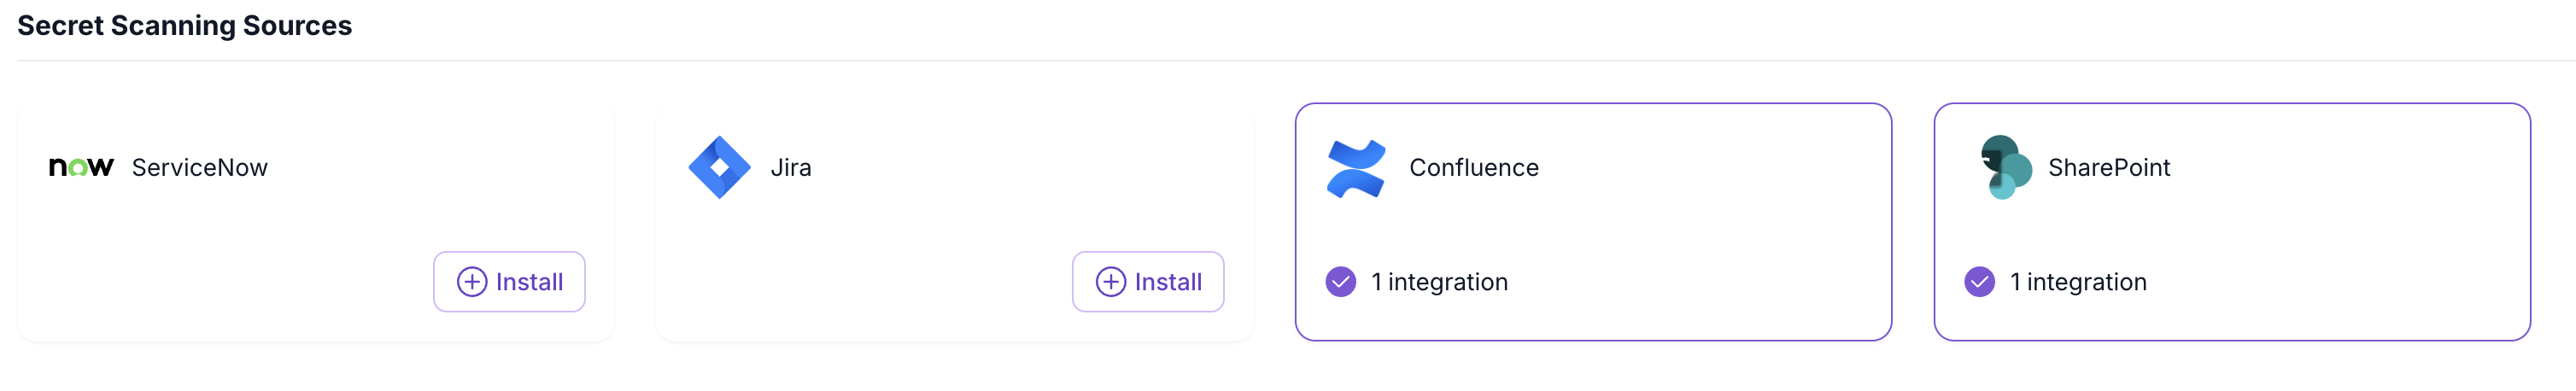
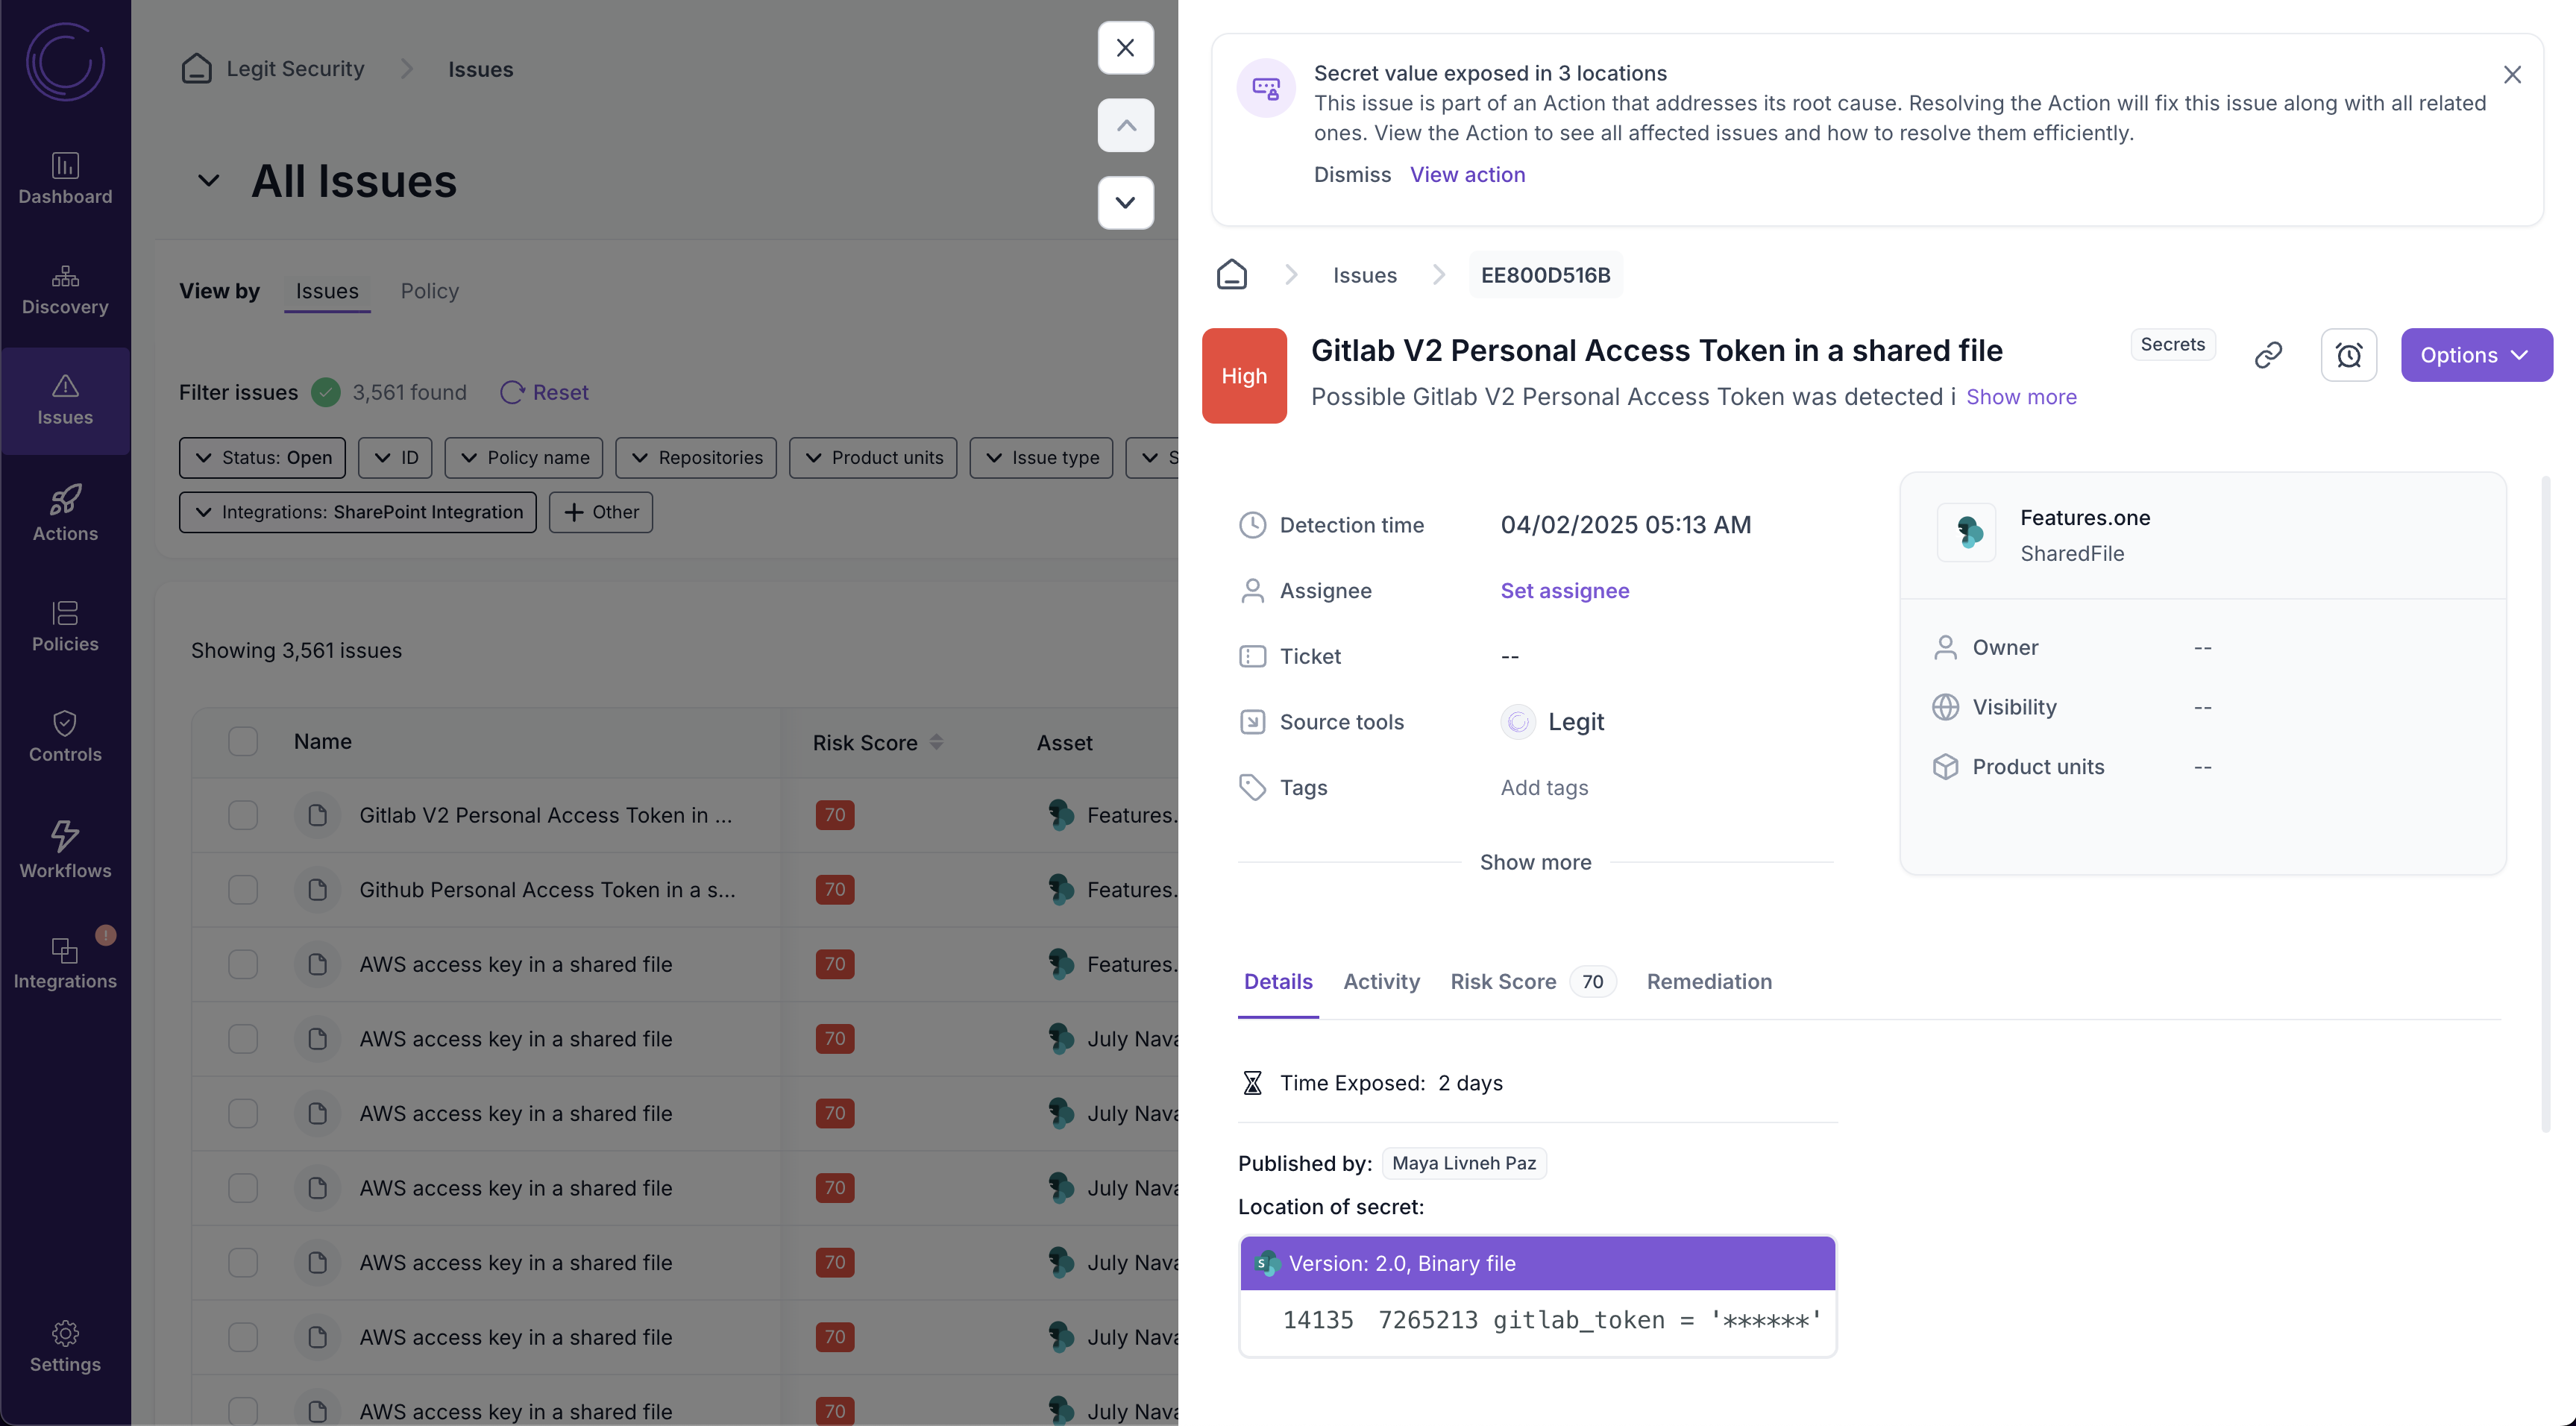
The Legit ASPM platform continuously scans SharePoint repositories for exposed secrets, such as cloud credentials, database connection strings, and OAuth tokens, using advanced detection algorithms.
Legit further integrates seamlessly with existing security workflows to automate remediation. The platform offers developer-friendly remediation guidance to quickly rotate compromised secrets.
Learn More
Learn more about Legit’s secrets scanning capabilities, or, for a limited time, get a 2-week free trial to see first-hand the power of Legit secrets detection and prevention.
Legit Security needs the contact information you provide to us to contact you about our products and services. You may unsubscribe from these communications at any time. For information on how to unsubscribe, as well as our privacy practices and commitment to protecting your privacy, check out our Privacy Policy.
More insights for modern AppSec teams
Why I Joined Legit
We believe that security tools had become very good at identifying problems, but that developers were still left with the hardest part: understanding those findings and turning them into secure code changes.

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.