How to Mitigate the Risk of GitHub Actions
How to Mitigate the Risk of GitHub Actions. Get highlights of our research into the security of GitHub Actions, and…

Preview of State of GitHub Actions Security Report: Security of GH Workflows Building Blocks
Security of the Building Blocks of GitHub Actions Workflows. Understand the security status of GitHub Actions…
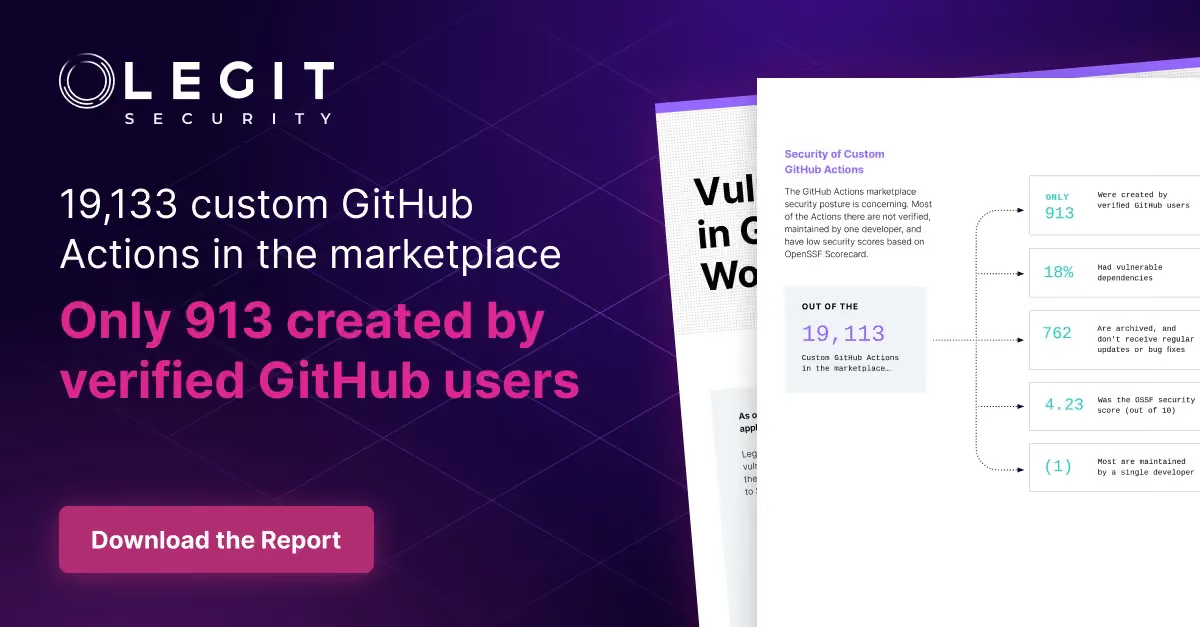
Security of Custom GitHub Actions
Security of Custom GitHub Actions. Get details on Legit's research on the security of custom GitHub Actions.
Announcing The State of GitHub Actions Security Report
Announcing the State of GitHub Actions Security Report. Get details on Legit's research on the security of GitHub…
Using AI to Reduce False Positives in Secrets Scanners
Using AI to Reduce False Positives in Secrets Scanners. Get an overview of how secrets scanners work, and how Legit is…
GenAI-Based Application Security 101
Gain insights into GenAI applications and how they represent an innovative category of technology, leveraging Large…
OpenSSF SCM Best Practices Guide Released With Contributions From Legitify
Explore the collaborative effort by OpenSSF and leading security vendors in the release of SCM Best Practices Guide.
Legit Security and CrowdStrike: Securing Applications from Code Creation to Cloud Deployment
Legit Security partnered with CrowdStrike to simplify cloud runtime protection. Reduce noise, streamline remediation…

How We Found Another GitHub Actions Environment Injection Vulnerability in a Google Project
This blog shows another case of GitHub Actions environment injection vulnerability in a Google repository.
Novel Pipeline Vulnerability Discovered; Rust Found Vulnerable
New software supply chain vulnerabilities use artifact poisoning and attack the software development pipelines on…
GitHub Codespaces Security Best Practices
GitHub configurations aren't secure out of the box. It's up to you to secure them. This blog discusses GitHub's new…
Attackers Can Bypass GitHub Required Reviewers to Submit Malicious Code
GitHub’s required reviewers capability can be bypassed if currently using this setting to require at least one code…
How Was LastPass Compromised? Software Supply Chain Attack Tips
LastPass data breach: unauthorized access compromised developer accounts and proprietary source code. Learn about the…
Google & Apache Found Vulnerable to GitHub Environment Injection
Learn how Legit Security discovered a vulnerable GitHub actions workflow that affected Google, Apache and potentially…
Vulnerable GitHub Actions Workflows Part 2: Actions That Open the Door to CI/CD Pipeline Attacks
We examine a bug we’ve found in a popular third-party GitHub action and how it could lead to your SDLC pipeline being…