Stay ahead of what’s next in Agentic AppSec.
Read our blogs to learn more about Agentic AppSec and the future of security when AI writes the code.

Search Resources
What Is Cloud Security Posture Management? CSPM Explained
Discover how cloud security posture management (CSPM) helps identify cloud misconfigurations, enforce compliance, and…
Emerging Risks with Embedded LLM in Applications
Learn how the use of Large Language Models (LLMs) like OpenAI's GPT and Google's Bard can create security risks in…

An In-Depth Guide to the Vulnerability Management Lifecycle
Learn to master the vulnerability management lifecycle. Safeguard against threats, implement best practices, and…

Application Security Testing: Types and Best Practices
Enhance your application security testing and identify vulnerabilities faster. Learn best practices and improve your…

How We Found Another GitHub Actions Environment Injection Vulnerability in a Google Project
This blog shows another case of GitHub Actions environment injection vulnerability in a Google repository.

SCA vs SAST: Cybersecurity Comparison Tools
Compare SCA vs SAST to enhance cybersecurity. Understand their methods, benefits, and how they protect against…

How to Choose the Right Vulnerability Management Tools
Discover core functions, benefits, and tips for selecting the best vulnerability management solutions to boost your…
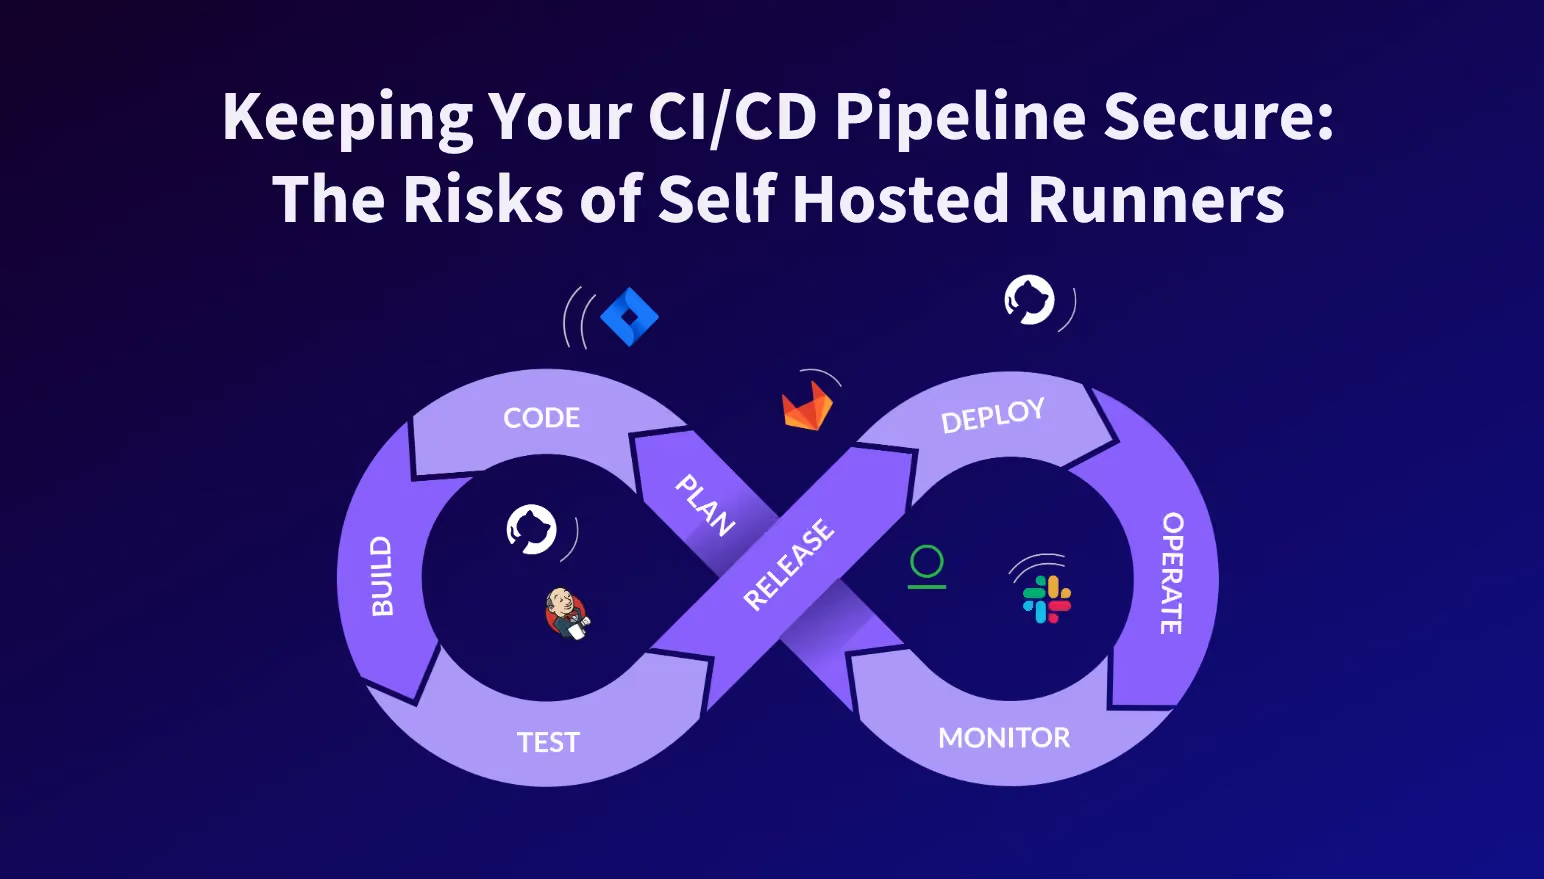
Securing Your CI/CD Pipeline: Exploring the Dangers of Self-Hosted Runners
CI/CD automates software development, while self-hosted runners enable general customization. SaaS platforms provide…

NIST Secure Software Development Framework Tips to Stay Ahead of Future Requirements
Boost the security of your code with the NIST SSDF (Secure Software Development Framework). Safeguard your business…
Securing AI-Generated Code
Explore Legit Security's revolutionary AI application security, risks, and solutions in our blog.

Embracing the Future of Secure Software Development: A Comprehensive Look at the SSDF
Explore the benefits of the Secure Software Development Framework (SSDF) and how it differs from traditional SSDLC…
Supply Chain Attacks Overflow: PyPI Suspended New Registrations
After PyPI paused new registrations due to a surge in malicious packages, learn how Legit Security helps protect your…
Deep Dive Into SLSA Provenance and Software Attestation
Discover the SLSA framework, designed to ensure the integrity of software artifacts and enhance overall software…