Azure DevOps Zero-Click CI/CD Vulnerability
The Legit Security research team has found and reported a zero-click attack that allowed attackers to submit malicious…
Legit Discovers "AI Jacking" Vulnerability in Popular Hugging Face AI Platform
Uncovering 'AIJacking': How Attackers Exploit Hugging Face for AI Supply Chain Attacks - A Deep Dive into…
Top Risks of Ignoring AI Code in Your Organization & LLM Embedding
Explore the security risks of generative AI, including code opacity and embedding concerns, in the evolving landscape…
Emerging Risks with Embedded LLM in Applications
Learn how the use of Large Language Models (LLMs) like OpenAI's GPT and Google's Bard can create security risks in…
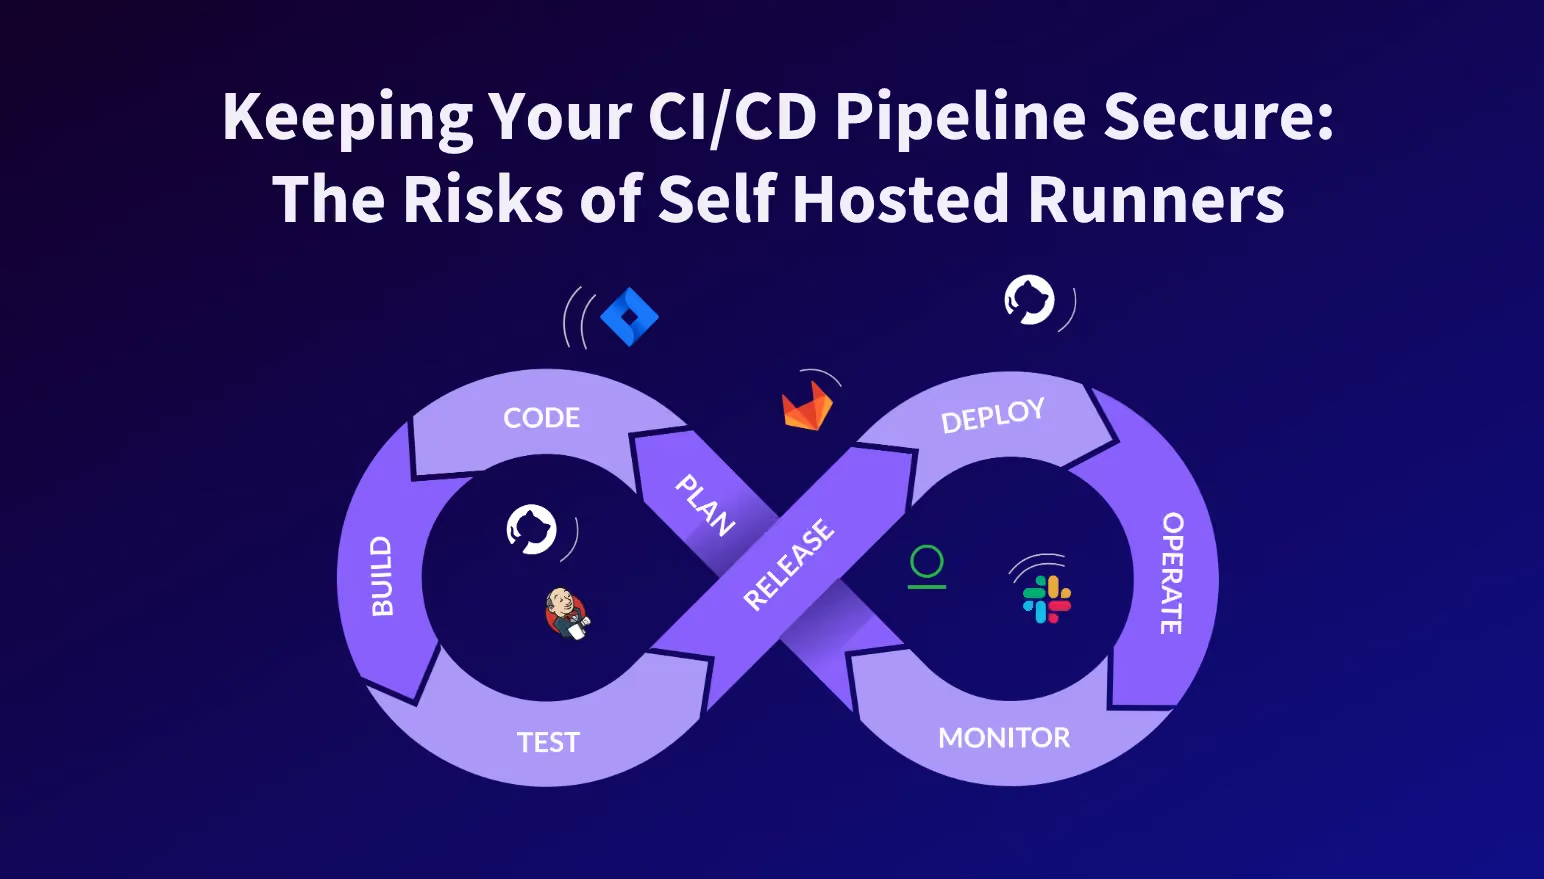
Securing Your CI/CD Pipeline: Exploring the Dangers of Self-Hosted Runners
CI/CD automates software development, while self-hosted runners enable general customization. SaaS platforms provide…
Securing AI-Generated Code
Explore Legit Security's revolutionary AI application security, risks, and solutions in our blog.
Sophisticated 3CX Software Supply Chain Attack Affects Millions of Users
3CX, an international VoIP IPBX software, experienced software supply chain attack. We detail what occurred, and how…
Remote Code Execution Vulnerability in Azure Pipelines Can Lead To Software Supply Chain Attack
Our team has found a vulnerability in Azure Pipelines (CVE-2023-21553) that allows an attacker to execute malicious…
How to Continuously Detect Vulnerable Jenkins Plugins to Avoid a Software Supply Chain Attack
See how attackers used compromised Jenkins plugins to attack the software supply chain and how to continuously detect…
Toyota Customer Data Leaked Due To Software Supply Chain Attack
On Oct 7th, Toyota announced a possible data leakage incident. The compromised data contained 296,019 customers'…